Can Agencies Use OpenAI Dots on Privacy Act Records?
Review OpenAI Dots for federal records, PII exposure and AI agent oversight under current agency policy, privacy rules and cloud authorization.
 redactsure
Research topic
Research on Privacy Act for AI agent workflows, with tokenization, access controls and evidence for teams handling sensitive business data.
Review OpenAI Dots for federal records, PII exposure and AI agent oversight under current agency policy, privacy rules and cloud authorization.
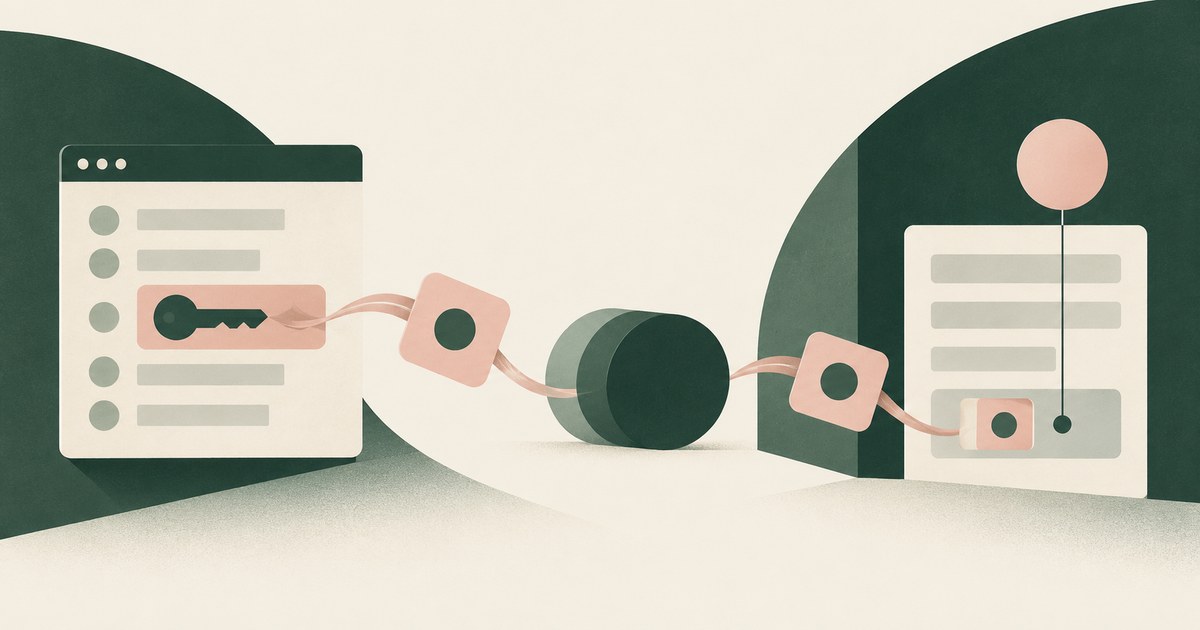
No, not while a state eligibility screen draws an applicant's name, date of birth and Social Security number into the model's context, because a Medicaid record is protected health information and a Privacy Act record at once. Check the system-of-records notice and the model contract, then require tokens on that screen and a named approver.
No. A records request can be logged, routed, tracked and answered without the responsive record ever reaching a model, but the redaction step has to run in a trusted room where someone reads the values it removes; ask which room each agent runs in and what the model receives on the screen.