How Do AI Agents End Up With Full Access to Sensitive Company Records?
By inheritance: an agent takes over a signed-in session, reads overshared data and runs under a broad service identity. Check which path each agent took.
 redactsure
Research topic
Research on service accounts: AI agent security, tokenization and checks for sensitive data access before allowing enterprise workflows to run.
By inheritance: an agent takes over a signed-in session, reads overshared data and runs under a broad service identity. Check which path each agent took.

Only when the agent never holds root or owner credentials, works under scoped roles, and a named person approves billing, IAM and network changes.
Everything the agent's service account can read, so an over-scoped account exposes whole projects. Check each account's grants and what the model reads.
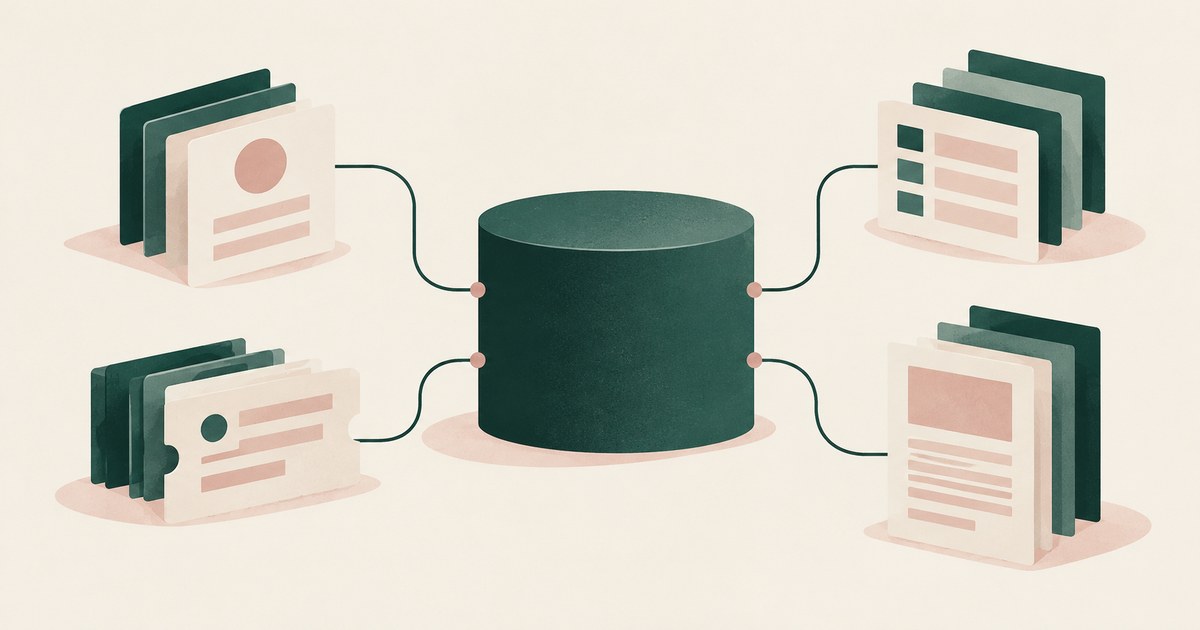
Whatever the service accounts behind each connector can read, which for HR and IT means tickets, cases and profiles at table level. Check connector scope.