
Data Report · By Chris Sowa · Published
Last updated
Does Keeping Credentials Outside the Sandbox Slow Down a Coding Agent?
Not as a network cost: the swap runs on the machine that hosts the sandbox, where a local proxy catches the request and rewrites the header without adding a hop, and no page reviewed gives a figure for that step. Time one proxied call, then count the approvals the same task needs.

A coding agent that never holds a credential still has to make the call, and for the platform team running it something other than the agent has to hold the value and attach it to that call. What the arrangement costs is really three questions: where the substitution runs, how many components a request crosses to reach it, and what else in the run has to wait. Vendor documentation answers the first two for the designs that exist, and it answers them in a way that keeps the work on one machine. The third is where a team's own stopwatch will disagree with a diagram, because an approval is a person or a policy making a decision, and a decision is not a step in a network path. The distinction matters because one of those costs can be reduced by configuration and the other has to be designed around. The example throughout is one record type, an API keys page in a cloud console where a coding agent creates a deploy credential, read against what each vendor page records. The page ends with a way to time one proxied call so the swap and the approval land in separate columns, which is the only comparison that tells a team which of the two it is paying for.
Key findings
- Docker's credentials page states that "An HTTP/HTTPS proxy on your host intercepts outbound requests from the sandbox" and "overwrites the auth header before forwarding," work that happens on the machine that already runs the sandbox (Docker, Manage, 2026).
- The isolation page states that "Credential values are never stored inside the VM," so the sandbox holds nothing the agent could read to make the call alone (Docker, Isolation, 2026).
- Anthropic's permissions page states that "To block Claude's file tools from reading a file or directory, add a
Readdeny rule for its path," which is upkeep measured in rules rather than in time per call (Anthropic, 2026). - A governed environment replaces a value with a consistent token before any model reads the screen, so the model works with a placeholder such as KEY_004 and never holds the string (What Is Render-Layer Tokenization?).
- Real values resolve only at the approved destination, at the moment of an approved action, so the wait a team can time is the decision and not the model's request (What Is Least Exposure?).
- Commits co-authored by an AI coding agent leak credentials at roughly double the baseline rate, which is why a value the agent never held is worth one local step (How Do You Let an AI Agent Manage API Keys Without Reading Them?).
Where does the credential swap sit in a coding agent's run?
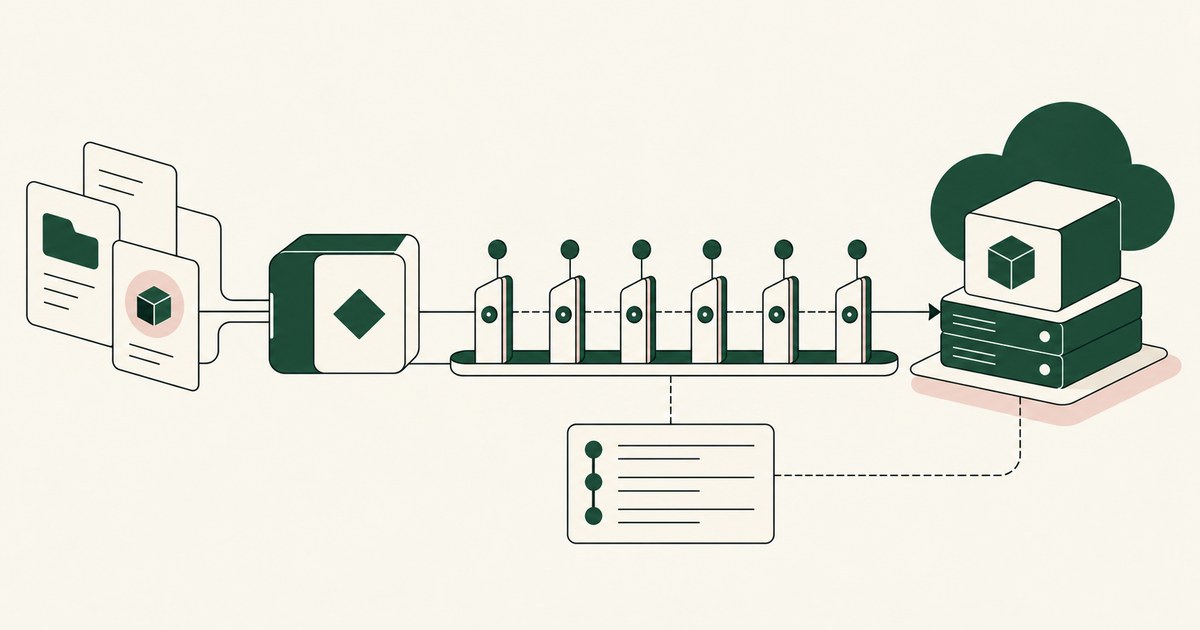
The swap is a step between the sandbox and the network, and it belongs to the host. The credentials page states that "The real credential stays on the host when proxy management is active; the sandbox sees only a sentinel value" (Docker, Manage, 2026). The sandbox composes a request with the sentinel, the proxy on the host replaces it, and the request continues to the destination. Nothing there asks the model to do anything new.
Two controls meet there and cover different surfaces. A governed browser environment covers what an agent reads and does on a rendered page, which is a dashboard, a console, a settings page or a sign-up form. It does not cover the terminal, the IDE, the local filesystem, direct API calls or MCP. A proxy that rewrites an authorization header on an outbound API call is outside that environment, and neither decides what the other does. A review that blurs the two ends up asking a browser control to bound a shell command, which it cannot do.
The proxy governs the request and not the tree. The architecture page notes that "A directly mounted workspace appears at the same absolute path as on your host," so a credential written into a file in the workspace remains a file the agent can open, sentinel or not (Docker, Architecture, 2026). A workspace is where credentials already collect: SecretBench counts "97,479 secrets (of which 15,084 are true secrets)" in public source (Basak et al., 2023). That is why the swap and the file rule are separate controls.
The definition in What Is a Tethered Agent? draws the line this page needs: the tether is "a description of authority, not of capability." A proxy changes what the agent holds; it does not change where the agent may go, and a control that narrows reach can slow a run by refusing work.
What does one proxied call add to the clock?
The record is one call, timed. A coding agent opens the API keys page of a cloud console, fills the create form for a deploy credential, and submits it; the request the page makes to the cloud's API is the call under measurement. The sandbox that makes it runs "inside a lightweight microVM with its own Linux kernel," and "The agent has no path to your host Docker daemon," so the request crosses one boundary to reach the proxy (Docker, Isolation, 2026).
What the proxy does not add is a second service. The step being timed is a process on the machine that already runs the agent, not a call to a gateway in another network, and the queue for it, if there is one, is local. That is why the vendors section below asks what the same pages require of a person, because that requirement, and not the hop, is what a team usually feels during a run.
What the step costs in time is not described in the pages reviewed, and that absence is the reason to measure rather than to assume. The documentation records where the substitution sits, not how long it takes, and it does not compare a run with the proxy to a run without one.
| Part of the run | What the documentation records | What a timing run should hold constant |
|---|---|---|
| Sandbox | A microVM with its own kernel and no path to the host Docker daemon | The image, the task and the model |
| Request | Outbound TCP from the sandbox through a proxy on the host | The destination path and the payload |
| Substitution | The proxy overwrites the auth header; the sandbox holds a sentinel | Whether a passthrough kit is enabled |
| Approval | A permission rule, documented by the tool | Counted in its own column |
| Workspace | A mounted workspace at the same absolute path, with no sync process | Whether the task writes files during the run |
Which credential sits behind the proxy matters more than the hop. The advice against creating access keys for a cloud account's root user applies to any durable credential an agent may reach, since the point of the swap is to bound what a stolen or misdirected value can do (Is It Safe to Let an AI Agent Set Up Your Cloud Environment?).
What do the vendors themselves say?
Docker documents the mechanism in pages that answer different parts of the question. The credentials page puts the substitution on the host and then limits it: these flows "apply to local sandboxes," and a kit with passthrough enabled "sends the real token response into the sandbox and reduces credential isolation" (Docker, Manage, 2026). The isolation page adds that "Credential values are never stored inside the VM," and that a sandbox runs in a microVM with no path to the host Docker daemon, so the step is documented as a boundary crossing on one machine and not as a service call.
The other half is the part a person maintains. Anthropic's page records the gap that keeps teams editing rules: they "don't apply to a command that reads files without naming them, such as grep -r pattern . run from the directory that holds the file" (Anthropic, 2026). The page does not give a duration for writing a rule, for the prompt a rule produces or for the review that follows it. It documents the rule and the gap, which is what a team schedules against.
| Dimension | Docker Sandboxes, per its documentation | What a buyer should verify |
|---|---|---|
| Where the value is | On the host, when proxy management is active | Which process on the host can read it back |
| What the sandbox holds | A sentinel value | Whether a passthrough kit is enabled |
| Path of a call | Through a proxy on the host, with the header overwritten | Whether every destination uses the same proxy |
| Scope | Local sandboxes | Whether a hosted sandbox behaves the same way |
| Timing | No duration for the hop on the page | Time one call with the same model and destination |
| Approvals | Not the subject of the page | Where the approval sits, and who answers it |
Read together, the pages answer the title in two parts: the swap is documented as a local step, and the permission layer is documented as work a person does. A team that times only the call will see the first and miss the second, which is why the next section takes the second apart.
Where does the delay a team notices come from?
A permission model is upkeep: the page notes that a .claudeignore file "has no effect, so move its entries into Read deny rules" (Anthropic, 2026). Every rule covers a path, a tool or a command shape, and the gap the same page records is the reason the set keeps growing. That work happens before a run, and it is invisible in a stopwatch.
The other documented cost is capability. Willison's patterns "constrain the actions of agents to explicitly prevent them from solving arbitrary tasks," and his page adds that "Agents can trigger tools, but cannot be exposed to or act on the responses from those tools" (Willison, 2025). A design that gives up capability can present as a slower one, because the work comes back to a person.
Scope design produces the rest of the friction. The Model Context Protocol's security guidance states that "Poor scope design increases token compromise impact, elevates user friction, and obscures audit trails" (Model Context Protocol, 2026). That guidance is written for MCP implementers and says nothing about how a coding agent's own credentials are held, so it is cited for the pattern: a credential scoped for one host and one task is cheap to explain; one issued for everything produces a queue.
An approval is also the one step whose duration is a person's attention. A team can automate a decision or narrow what needs one; it cannot make the decision arrive sooner by moving the substitution. The proxy is deterministic; the queue is not.
How should a team time one proxied call?
Start with one agent, one task and one destination. Run the task with the credential outside the sandbox, take each call's duration from the console's own network log, and put the approval wait in a separate column with the approver's name.
Two variables will spoil the comparison if they move. The first is the model: Claude Opus 5.5 shipped on September 22 at $4 and $20 per million tokens, and Sonnet 5.5 on September 28 at $2 and $10, so a baseline is a baseline for one model, as Can AI Models Change Without Changing Their Controls? sets out.
The second is what the test may expose. A team cannot measure the swap by turning passthrough on, because that setting returns the value to the sandbox and removes the property under test. So keep the value outside, time the call, and read the transcript afterward for the string; if it appears, the run measured something else.
Sonatype's release states that "56% of the malware discovered in Q1 2025 was related to data exfiltration," up from 26% in the fourth quarter of 2024 (Sonatype, 2025). An injection study of agentic coding editors reports that "attack success rates can reach as high as 84% for executing malicious commands" (Liu et al., 2026). A value the model never held cannot be carried out by either route.
A durable credential narrows the gain further: Carlini and colleagues extracted training data from a large language model verbatim, the record that makes a value's presence in a context a lasting problem (How to Use AI Agents to Deploy Azure GPU Virtual Machines).
What does a governed environment change?
A governed environment treats the value as something the model never needs and the task sometimes does. On a rendered page, values chosen by policy are replaced with consistent tokens before any model reads the screen, so a field, a confirmation and the next page show the same reference for the whole run. The model works on KEY_004 the way it would work on the string, and the record shows which pages carried the token.
Real values resolve only at the approved destination, at the moment of an approved action. That is a different guarantee from keeping a value out of a process: the value is not merely absent, it is available once, in one place, when a named person has approved the action that needs it. Every screen as tokens, every action and every approval is written to a record that exports to the organization's own monitoring.
For this page's question the change is where the wait lands. A local proxy adds a step a stopwatch can measure and mostly cannot see. A governed environment puts the substitution at the render layer and the decision with a person, so the two costs appear in different columns by design rather than by accident, and a review can say which one it is paying for.
Its scope is the rendered page: the dashboard, the console, the settings page the agent reads. It does not govern the terminal, the IDE, the local filesystem, direct API calls or MCP, so a proxy that attaches a credential to an outbound call remains a separate control with its own review. A team that wants both can have both; it should not describe one as the other.
Methodology and limitations
This page rests on three Docker Sandboxes documentation pages, Anthropic's Claude Code permissions page, the Model Context Protocol's security best practices, one practitioner analysis of prompt injection design patterns, one vendor research release from Sonatype, two research preprints on credentials and on injection against coding editors, and two existing RedactSure research pages. The Docker pages are cited for the proxy mechanics and for what the sandbox holds, the Anthropic page for the permission rules and their gaps, and the release and the preprints for what the swap buys down. Vendor pages were read between October 20, 2026 and October 21, 2026, and each Sources line carries the date for its page. Quoted facts appear as the page states them, and figures from the preprints are cited as their abstract pages report them.
RedactSure did not test Docker Sandboxes, Claude Code or any other product hands-on, and the duration a hop adds to a call is not described in the pages reviewed. Those pages describe where the substitution happens and what a permission model requires, which is what this page uses them for. Vendor features change, and the page carries its date; a release after that date should be treated as unreviewed until the call is timed again. Statements about RedactSure describe its current design, and RedactSure is deploying now with enterprise and government customers. The example describes a record type, an API keys page in a cloud console, and not an organization.
Determinations about whether a coding agent's use of a credential meets a contractual, regulatory or internal control requirement belong to counsel, assessors and the organization's own security and compliance officers. Nothing here replaces a timed run of the organization's own agent against a test credential, repeated after each model or tool release. The timing method above is a control check for one team on one machine, not a benchmark, and a single timed run does not measure a product.
What the record shows
The documented designs put the swap on the machine that runs the sandbox, so what they add is one local step, and none of the pages reviewed gives that step a duration. What the same pages document is the work around it: a rule for every path, a migration from a file that has no effect, an exception for a command that reads files without naming them, and a sandbox setting for enforcement. That work takes a person's time, and it happens inside the run, so it reads as the arrangement being slow. None of the controls changes what the model reads on a page before the call. The two costs separate in a simple test: pick one agent and one API call, run it twice with the same model and destination, and record the call duration and the approval count in separate columns; if the approval column is the long one, the swap is not the cost.
Frequently asked questions
Does keeping credentials outside the sandbox slow down a coding agent?
It adds one step on the machine that already runs the agent: a proxy on the host that overwrites the authorization header before the request continues. Docker's pages describe that arrangement for local sandboxes and publish no duration for the step, so the answer is a small step with no recorded figure. The larger delay in the same run is the approval a permission rule or a person adds, and the two are worth timing separately. The step itself is worth one timed pair on the team's own machine.
What does the proxy add to a single call?
One header rewrite, performed by a process on the host between the sandbox and the destination. The sandbox still composes the request and still receives the response; the credential it would have held is a sentinel, and the real value is attached after the request leaves the virtual machine. Nothing in that sequence adds a second service. What a team measures is a local step, and only a timed pair of runs on its own hardware shows its size. Both halves are cheaper to check than to argue about.
Why do approvals feel like latency?
Because they happen inside the run and wait on a person. A permission rule has to exist before the action it covers, and the pages reviewed show how much rule writing that takes: a rule per path, a migration from a file that has no effect, and a gap for commands that read files without naming them. A stopped run looks the same whether the wait is a network step or a reviewer, and the record says which one. A log of approvals answers it; a faster proxy does not.
How should a team measure the difference?
Fix one agent, one task and one destination, then record the duration of each call the console makes and the number of approvals the task needs, in two columns. Keep the model constant, because a new model resets the baseline, and keep passthrough off, since that setting returns the value and removes what is being tested. One run on one machine is a control check, not a benchmark. Write both columns down, and repeat the pair after each release.
Does a faster model change the answer?
It changes the baseline, not the conclusion. A faster model shortens the turns that dominate a run, which makes a fixed local step a larger share of what remains, so the ratio moves while the step itself does not. So the comparison to keep is between two runs of the same model, and a figure from last quarter should not be carried forward without timing a call on the current one. Record which model each number came from.
What should a security review ask for in writing?
Where the credential is held while the agent works, which process attaches it, which destinations may receive the real value, and what setting would return it to the sandbox. Then ask who approves an action that uses it, and what record shows the approval. A vendor that answers the first four and not the last has described a proxy rather than a governed run, and the gap appears in a review after an incident. Ask for that record before the pilot, not after it.
Related reading
What Is Render-Layer Tokenization? · What Is Least Exposure? · How Do You Let an AI Agent Manage API Keys Without Reading Them? · What Is a Tethered Agent? · Is It Safe to Let an AI Agent Set Up Your Cloud Environment? · Can AI Models Change Without Changing Their Controls? · How to Use AI Agents to Deploy Azure GPU Virtual Machines · Can a Coding Agent Read My AWS Credentials File? · How Do I Keep Credentials Outside the Sandbox Where the Agent Runs? · Can Credentials Stay Outside the Sandbox and Still Be Used Inside It? · On the RedactSure blog: Operating Inside the Lethal Trifecta · What If the Agent Never Had Your Data? · RedactSure
Sources
Peer-reviewed research and preprints
-
Basak, Neil, Reaves, Williams, "SecretBench: A Dataset of Software Secrets," arXiv:2303.06729 (preprint, 2023). https://arxiv.org/abs/2303.06729
-
Liu, Zhao, Lyu et al., "Your AI, My Shell: Demystifying Prompt Injection Attacks on Agentic AI Coding Editors," arXiv:2509.22040 (preprint, revised 2026-04-28). https://arxiv.org/abs/2509.22040
Vendor documentation
-
Docker, "Manage credentials," Docker Sandboxes documentation, updated October 20, 2026 (vendor documentation; read October 21, 2026). https://docs.docker.com/ai/sandboxes/configuration/credentials/
-
Docker, "Isolation layers," Docker Sandboxes documentation (vendor documentation; read October 20, 2026). https://docs.docker.com/ai/sandboxes/security/isolation.md
-
Docker, "Architecture," Docker Sandboxes documentation (vendor documentation; read October 20, 2026). https://docs.docker.com/ai/sandboxes/architecture.md
-
Anthropic, "Configure permissions," Claude Code Docs (vendor documentation; read October 20, 2026). https://code.claude.com/docs/en/permissions
Regulation, standards and official guidance
- Model Context Protocol, "Security Best Practices," modelcontextprotocol.io specification (standard; read October 20, 2026). https://modelcontextprotocol.io/specification/latest/basic/security_best_practices
Industry analysis and press
-
Sonatype, "Nearly 18,000 Malicious Packages Discovered in Q1," April 2, 2025 (vendor research). https://www.sonatype.com/en/press-releases/18000-new-malicious-packages-discovered-in-q1
-
Willison, "Design Patterns for Securing LLM Agents against Prompt Injections," June 13, 2025 (practitioner analysis). https://simonwillison.net/2025/Jun/13/prompt-injection-design-patterns/
RedactSure documents
-
RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization/
-
RedactSure Research, "What Is Least Exposure?" (2026). https://redactsure.com/research/what-is-least-exposure/
-
RedactSure Research, "How Do You Let an AI Agent Manage API Keys Without Reading Them?" (2026). https://redactsure.com/research/how-do-you-let-an-ai-agent-manage-api-keys-without-reading-them/
-
Product behavior described on this page reflects RedactSure's current design. Third-party products are described from their public documentation as read between October 20, 2026 and October 21, 2026. Compliance determinations belong to the organization's counsel.

What Is Render-Layer Tokenization? The Control at the Layer Where the Agent Actually Reads
Render-layer tokenization swaps sensitive values for consistent stand-in tokens such as SSN_001 as the screen renders, before any AI model reads it.

What Is Least Exposure? Reading the Principle, the Gap It Closes and the Published Numbers Behind It
Least Exposure is a security approach for AI agents that gives each task only the data it needs, applied before any model reads the screen.
How Do You Let an AI Agent Manage API Keys Without Reading Them?
Swap the key for a token as the dashboard renders it, and resolve the real value in the approved field when a person confirms. Check where keys show.

What Is a Tethered Agent? The Plain-Words Name for an Agent a Named Person Answers For
A tethered agent stays tied to a named person for the whole run: that person grants access, sees what the agent sees and approves consequential actions.

Is It Safe to Let an AI Agent Set Up Your Cloud Environment?
Only when the agent never holds root or owner credentials, works under scoped roles, and a named person approves billing, IAM and network changes.
Can an Enterprise Change AI Models Without Changing Its AI Controls?
Yes, when input policy, approvals and audit records are enforced independently of the model. A model change still needs capability and supplier review.
How to Use AI Agents to Deploy an Azure N-Series Virtual Machine and Configure NVIDIA GPU Drivers
Deploy an Azure N-Series VM with NVIDIA drivers via an AI agent in a governed environment where subscription and secrets are tokens and a person approves.
Can a Coding Agent Read My AWS Credentials File?
Any agent with filesystem access can read ~/.aws/credentials unless the harness blocks the path. Claude Code and Cursor document path blocks;
How Do I Keep Credentials Outside the Sandbox Where the Agent Runs?
Put the credential in a process on the other side of the boundary that makes the call for the agent: the agent sends a reference.
Can Credentials Stay Outside the Sandbox and Still Be Used Inside It?
Yes, when the request leaves the sandbox with a placeholder and the credential is attached outside it, on the host or at a proxy.

Operating Inside the Lethal Trifecta
Follow a prompt-injection scenario to examine AI agent security, tokenization and what an attacker can obtain from sensitive workflows.

What If the Agent Never Had Your Data?
Explore AI agent security built around tokenization, controlled browser actions and human approval before sensitive payments proceed.
How RedactSure Keeps the Credential Swap Off the Critical Path
The credential swap is local, and the wait that costs real time belongs to an approval decision that the pages reviewed leave to whichever tool asks.
The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company.
Before: the API keys page renders the new key, the model reads it while it fills the form, and the request leaves with the string. Inside: the page renders KEY_004, the model submits that token, and the value is attached at the approved destination after a named person approves it.
RedactSure is deploying now with enterprise and government customers. An injection study of agentic coding editors reports "attack success rates can reach as high as 84% for executing malicious commands."
Everyone else controls where data can go. RedactSure controls what the AI can see.
See it on your own workflow
Controls that slow an agent down tend to get switched off within a few weeks of rollout. Bring a task your agent runs every day, watch it run with test values, and judge the pace for yourself. Book a demo