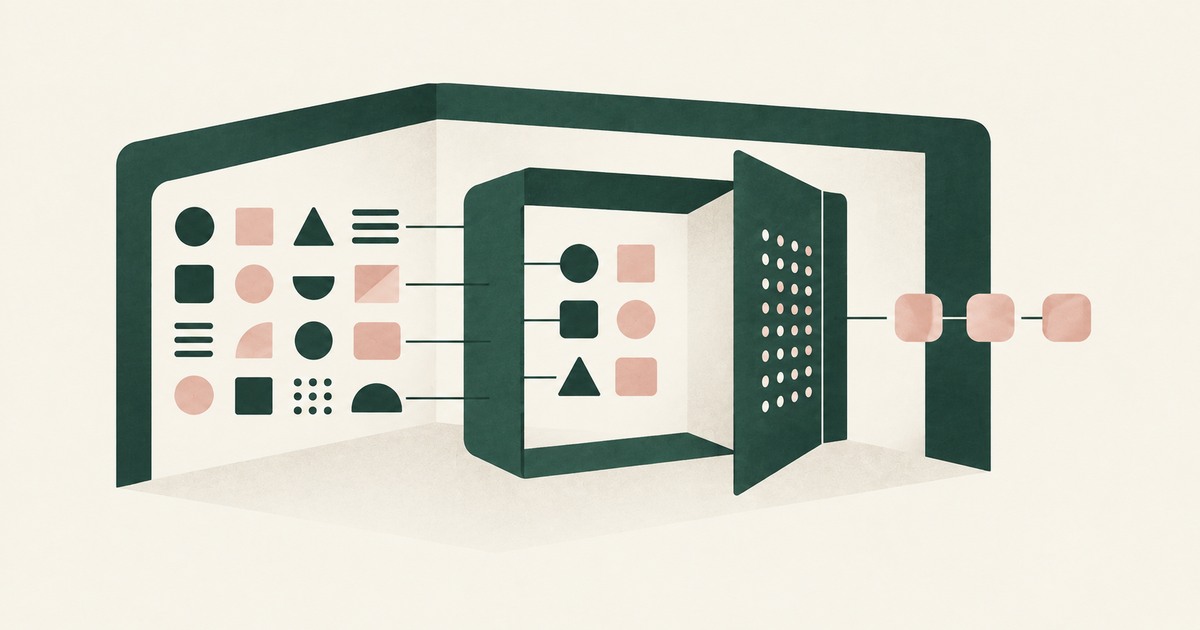
The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.
 redactsure
Read articles on AI agent architecture, tokenization and sensitive PII boundaries, with source links and practical questions for regulated teams.
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.
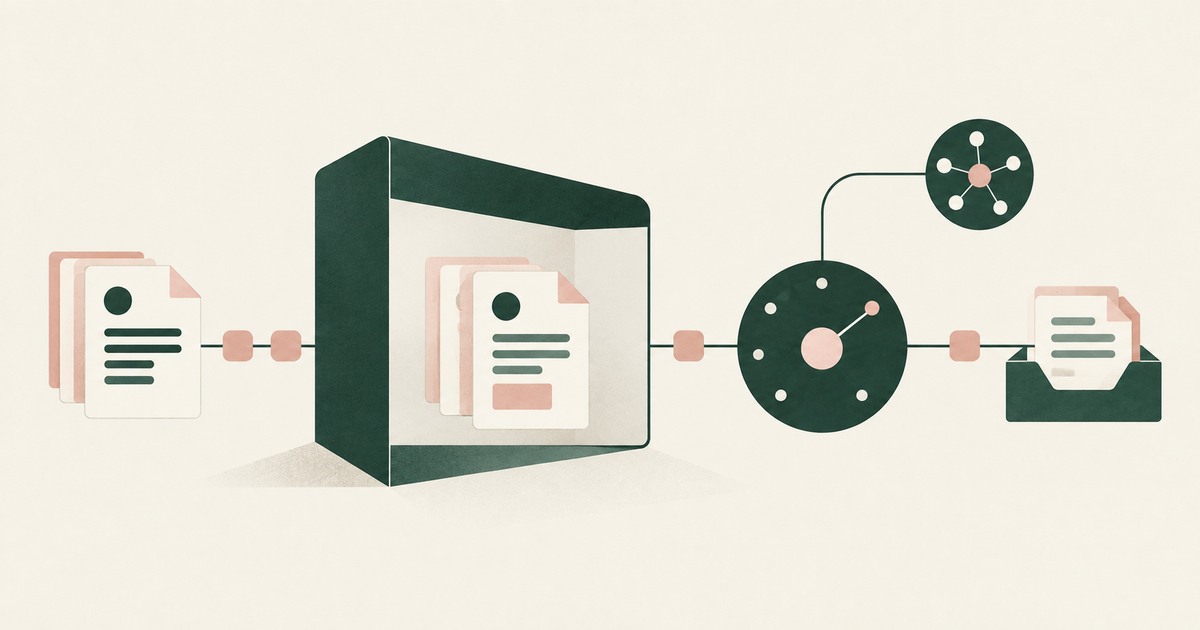
Learn how AI agents can cross billing, claims and enterprise systems while tokenization and human approval keep sensitive work governed.
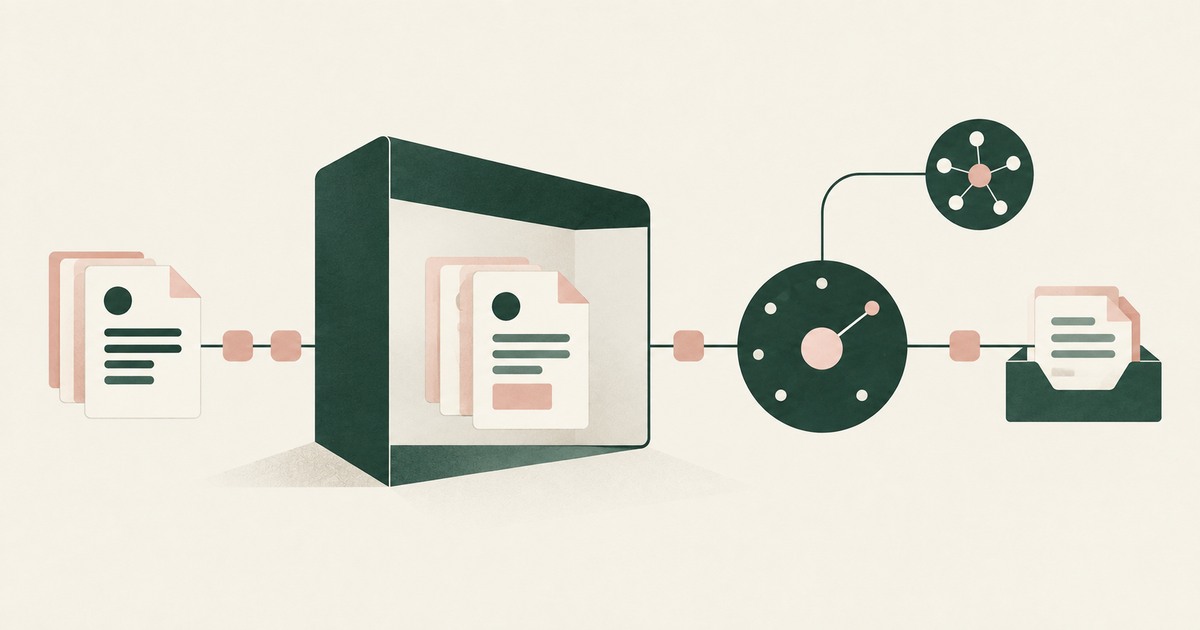
Explore AI agent governance for billing and claims, with named supervisors, data masking, approval boundaries and a useful audit record.
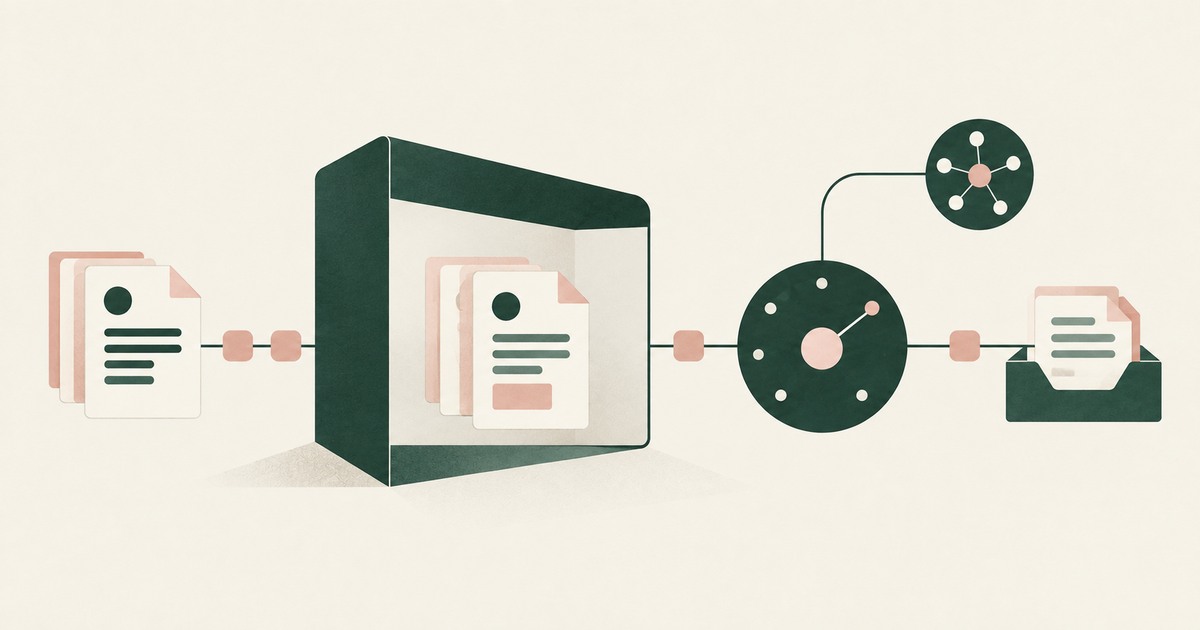
Explore AI agents that work across billing, collections and enterprise systems while tokenization protects PII at each workflow step.
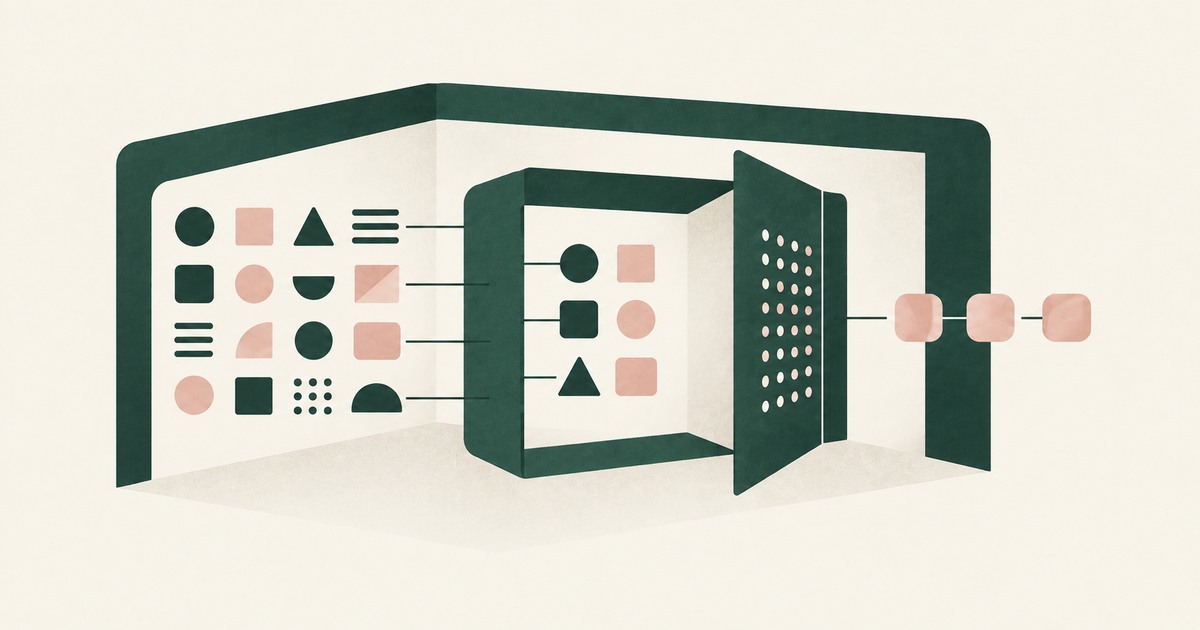
Examine AI agent security gaps in regulated workflows, from PII exposure and shadow AI to the controls needed before payments move.
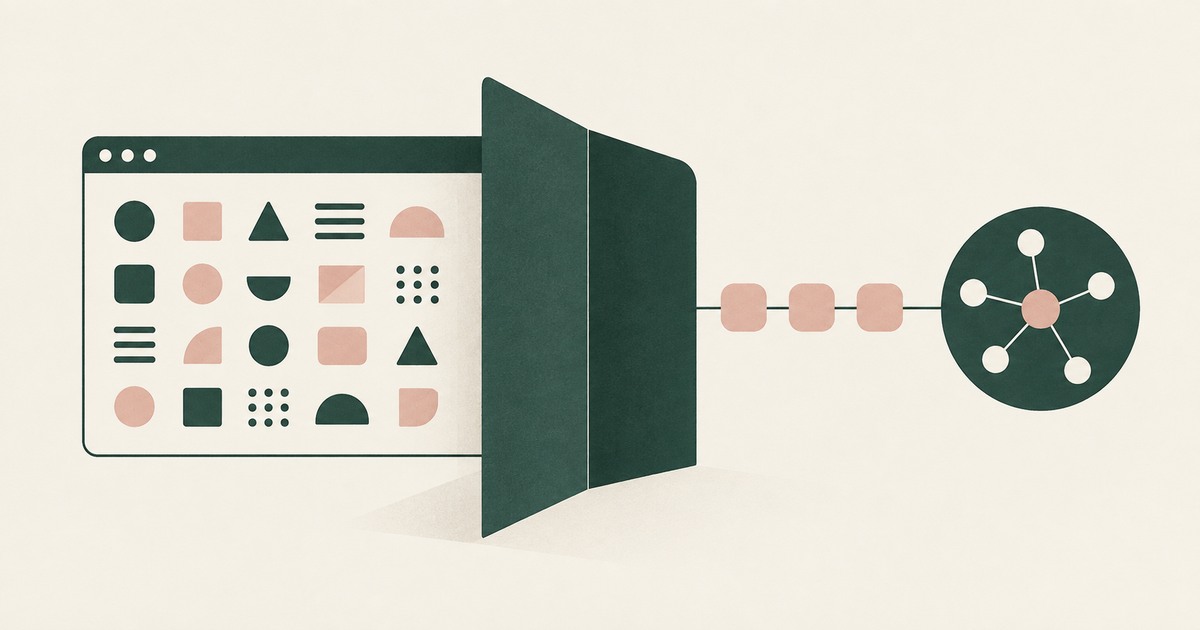
Explore AI agent security built around tokenization, controlled browser actions and human approval before sensitive payments proceed.
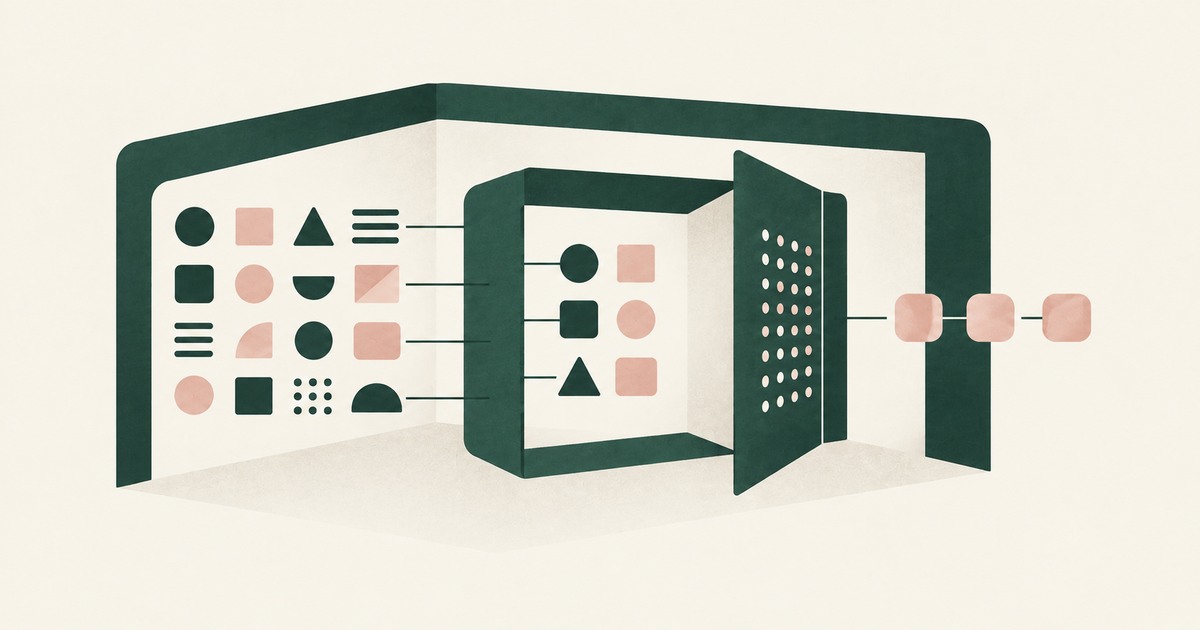
Follow a prompt-injection scenario to examine AI agent security, tokenization and what an attacker can obtain from sensitive workflows.
Bring one billing, collections, claims or patient-account workflow and your questions.
Book a demo