Does Prompt Injection Expose Customer Records?
Yes, when the injected agent sees real customer data and can send outward; attacks leaked data at 20 to 70 percent. Check what the model holds.
 redactsure
Research topic
Research on AI agent data protection: AI agent security, tokenization and checks for sensitive data access before allowing enterprise workflows to run.
Yes, when the injected agent sees real customer data and can send outward; attacks leaked data at 20 to 70 percent. Check what the model holds.
Only partly. An allowlist controls where an agent goes, not what it reads on an approved page. Check what the model receives from each approved screen.
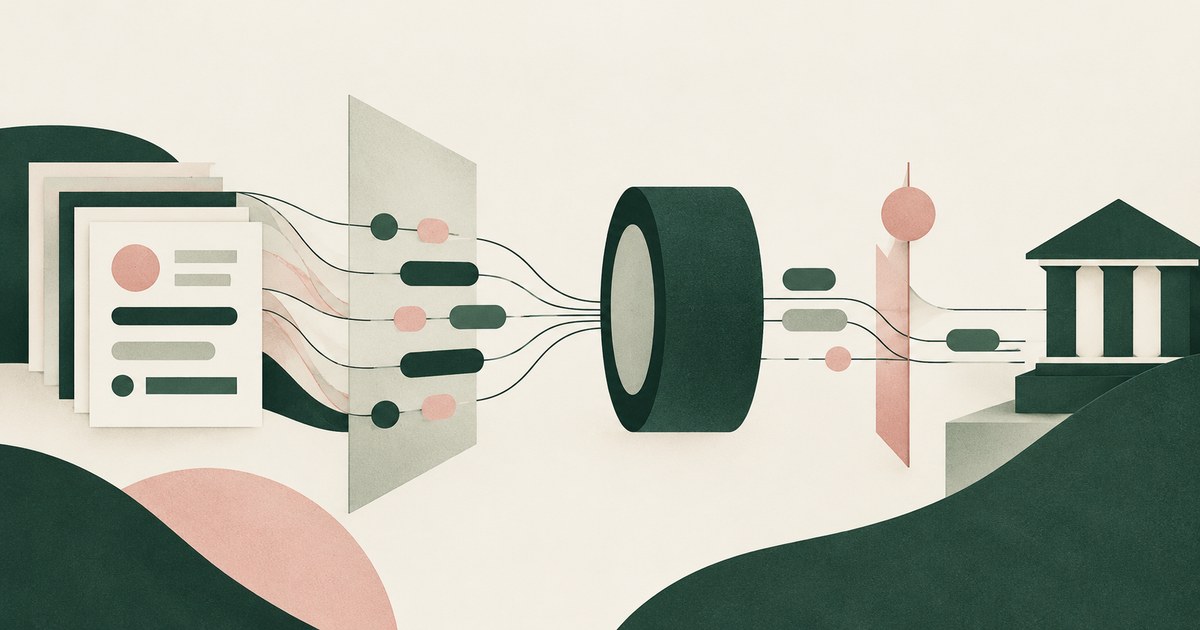
They can, if the model never receives nonpublic personal information: identifiers are tokenized on screen and resolve only at approved destinations.
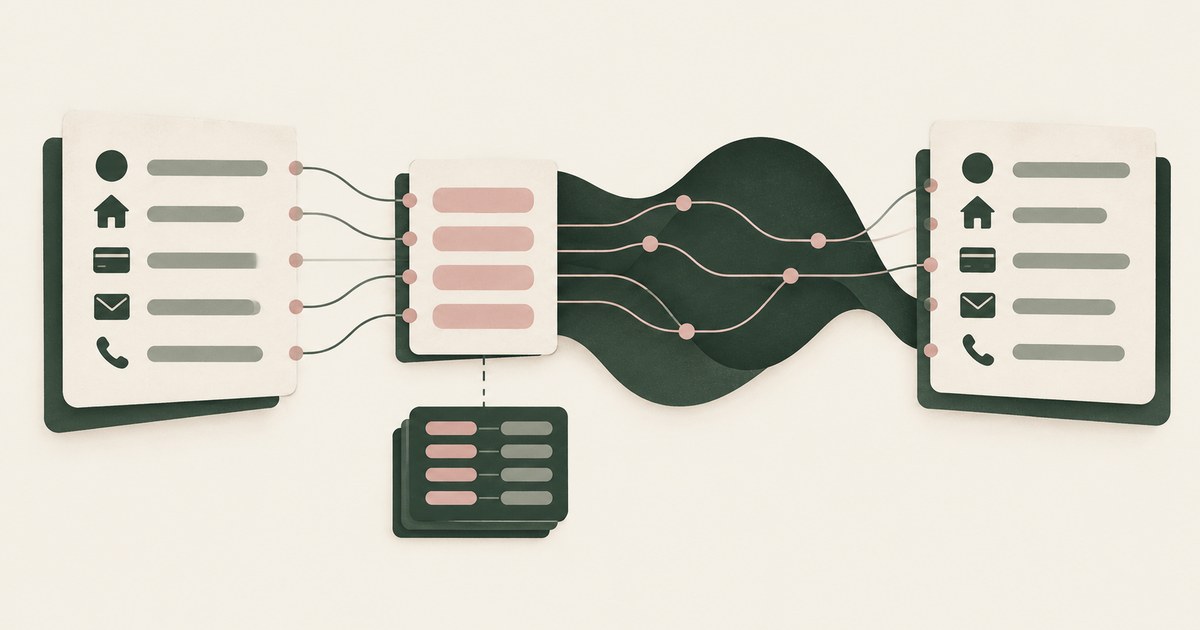
By reading tokens instead of values: each identifier is replaced with a consistent surrogate before the model sees it and restored at the destination.
By inheritance: an agent takes over a signed-in session, reads overshared data and runs under a broad service identity. Check which path each agent took.
Separate workflow access, meaning navigating and filling fields, from access to screen values, granted at approved destinations. Check what a platform has.
Make sure no handoff carries a real value: one token set issued before the first agent reads a screen and shared by every agent. Check what crosses a hop.
Treat the agent and its model provider as a school official under direct control, and keep education record PII out of the model. Check what it sees.
Only when the reading agent cannot also hold real sensitive data and act outward in one session, since any page may carry instructions. Check which it has.