Is It Safe to Let AI Agents Access Financial Records?
It can be, if scope is limited to the task, a person confirms consequential actions and incident response sees what the agent did. Check PCI scope effects.
 redactsure
Research topic
Research on incident response: AI agent security, tokenization and checks for sensitive data access before allowing enterprise workflows to run.
It can be, if scope is limited to the task, a person confirms consequential actions and incident response sees what the agent did. Check PCI scope effects.
The risk is rarely the task; it is the side channels where an agent reuses customer details or a hostile page coaxes them out. Check what it carries on.
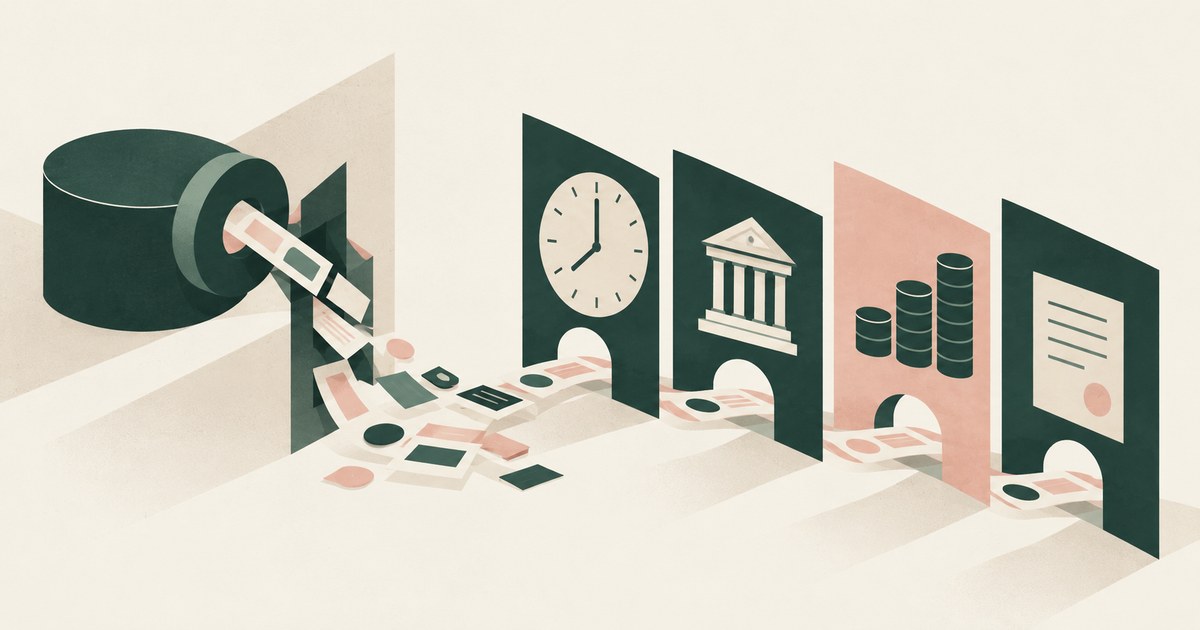
Notification clocks, regulator reviews, fine tiers and contract consequences run in order, whether a person or agent caused it. Keep PII out of the model.