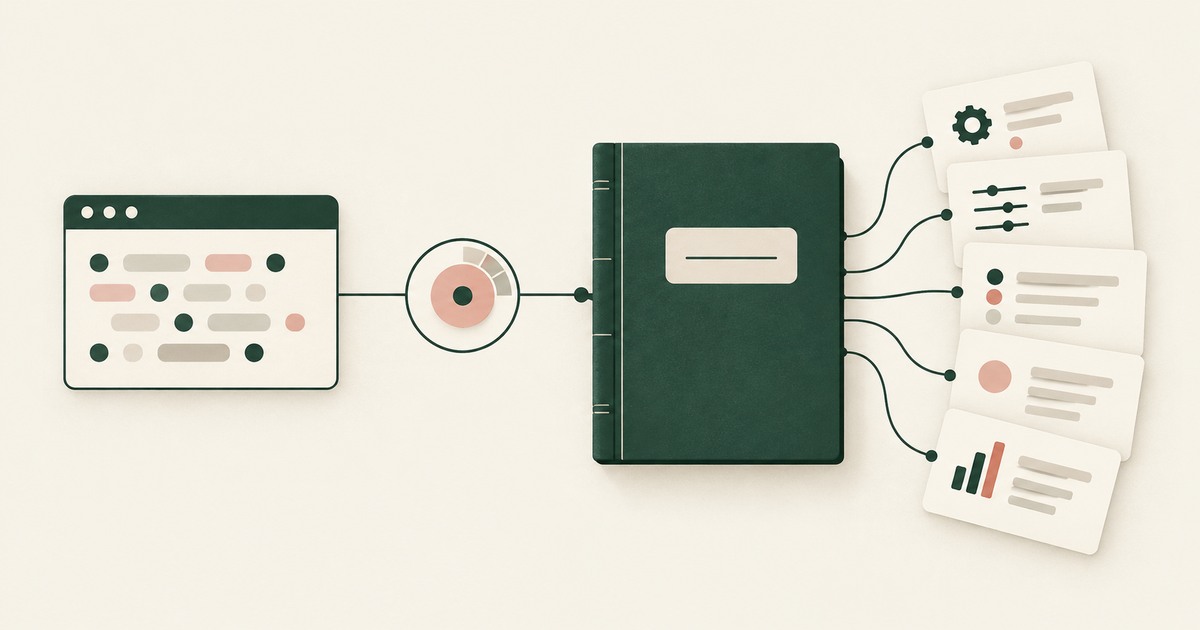
How Do You Audit What an AI Agent Saw and Did?
Explore AI agent audit evidence for sensitive claims and billing, including tokenization policies, approvals and logs that avoid raw PII.
 redactsure
Read research on AI agent audit records, tokenization and approval for payments, with source links and practical questions for regulated teams.
Explore AI agent audit evidence for sensitive claims and billing, including tokenization policies, approvals and logs that avoid raw PII.
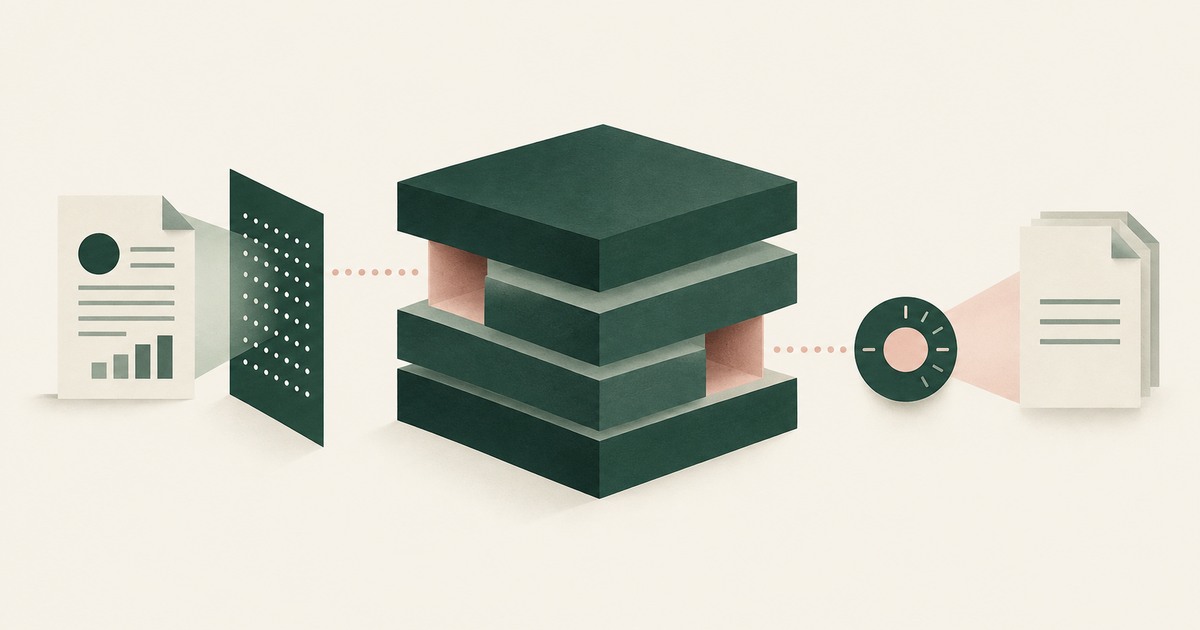
Examine AI agent security gaps in data visibility and accountability, and how tokenization and named approvals address sensitive PII.
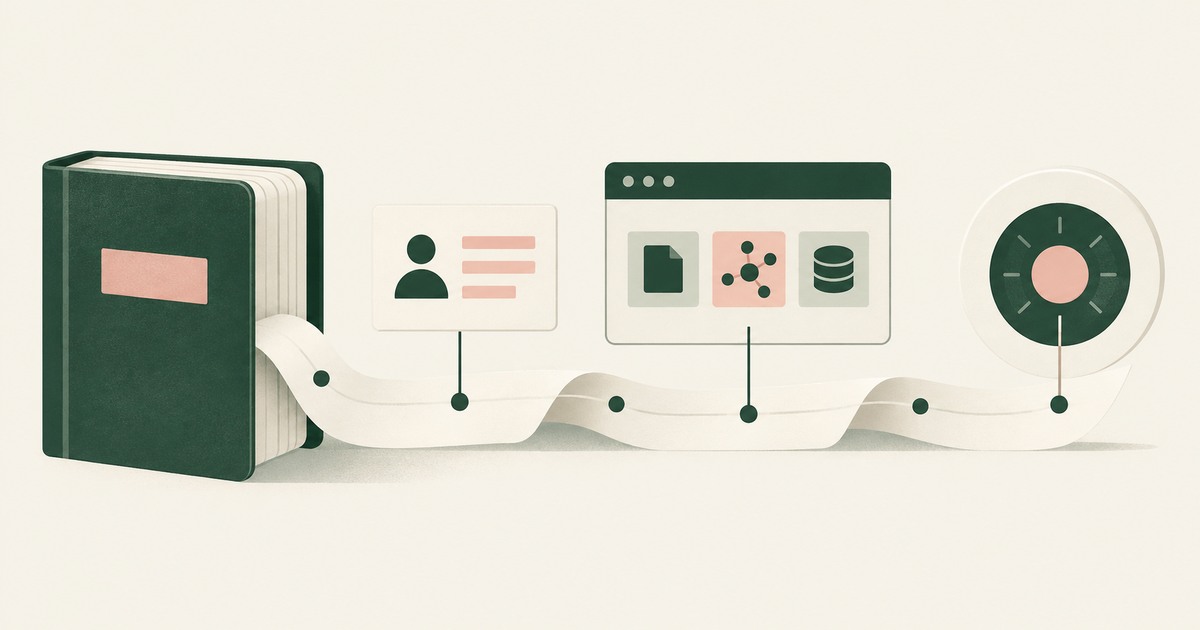
Explore an AI agent control record for billing and claims, linking permissions, tokenization decisions, approvals and audit evidence.
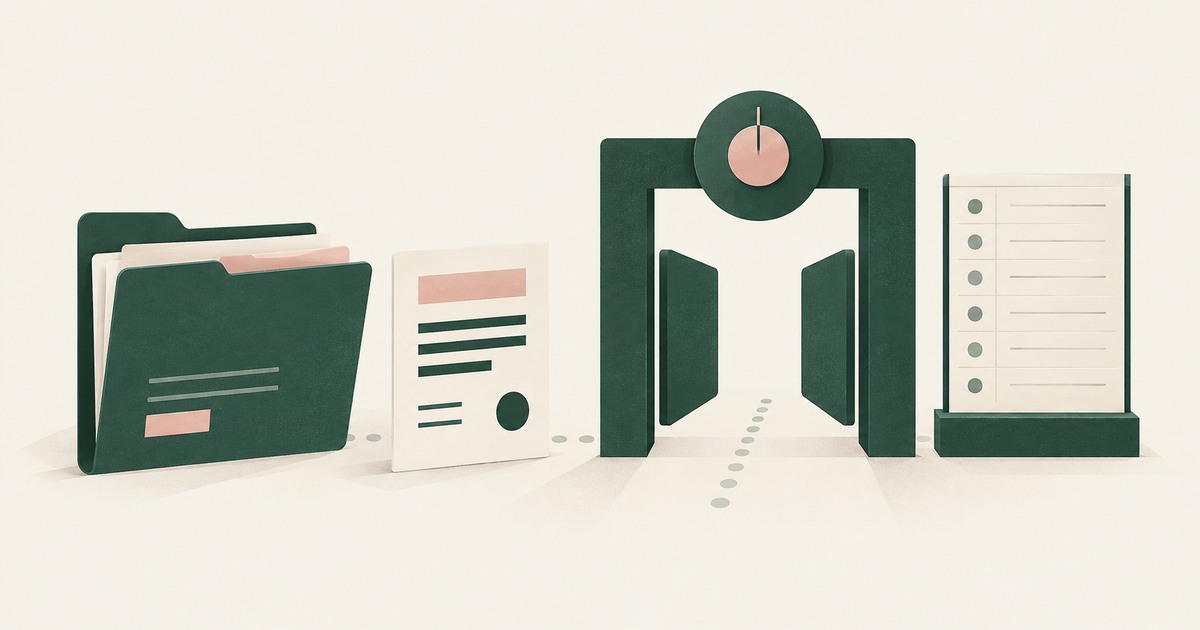
Examine human approval for AI agent claims payments, including PII tokenization, settlement authority and the evidence an auditor needs.
Review AI agent approval settings for claims, billing and payments, including standing permissions, named approvers and recorded decisions.
Review AI agent security, automated action reviewers and PII controls for regulated claims and payments, with customer approval evidence.
Review Monitor What an AI Agent Actually Accesses, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Not reliably. Benchmarks show careful agents still take irreversible actions. Check that reversibility is classified by the environment, not the model.
Yes, and the approval must be provable and tied to a named person, since agents already place unrequested orders. Check that the submit step records it.
Not for every action, but for any that is consequential, irreversible or leaves the organization. Check that the environment enforces the gate.
A named person's ability to stop an agent at once: end sessions, revoke credentials, halt actions in flight and preserve the record. Check you have each.
Separation of duties applied to the agent: it prepares the entry, a named person with posting authority commits it, and the record attributes each step.
Treating delete as privileged: removed from default rights, held for a named person's approval, backed by recoverable storage. Check if delete is in reach.
Enforcement outside the model: a permission scope the agent cannot exceed and an action gate held until a named person approves. Check neither trusts it.
The named person already accountable for releasing that data, such as the records custodian or account owner, not the AI team. Check each send goes there.
The business owner accountable for the outcome approves the workflow, and a named person approves each consequential action inside it. Name both.
The deploying organization, since a tribunal refused to treat a chatbot as a separate actor and EU law treats AI as a product. Check you can show approval.
Bring one billing, collections, claims or patient-account workflow and your questions.
Book a demo