
Explainer · By Chris Sowa · Published
Last updated
Is Island Enterprise Browser Enough to Protect Data From AI Agents?
Island's enterprise browser enforces policy on what a person does with data, and its masking, detectors and last-mile controls do that documented job; what a model receives when an agent reads a permitted page is not described in the pages reviewed. Check what reaches the model from the rendered page, the step the browser needs alongside it.
Island's enterprise browser enforces policy on what a person does with data, and its masking, detectors and last-mile controls do that documented job; what a model receives when an agent reads a permitted page is not described in the pages reviewed. Check what reaches the model from the rendered page, the step the browser needs alongside it. This page evaluates one product against one question. It describes the controls Island documents and what a user sees, asks what they leave untouched when the reader is an agent's model, sets out the admin options and limits Island documents, and closes with what a governed environment adds.
Key findings
- Island describes its Enterprise Browser in terms of security, visibility, manageability, central policy enforcement, data loss prevention, boundaries, masking and detectors, all for the person using it (Island, 2026).
- Island's last-mile data controls cover a person's copy, paste, download, upload, screenshot capture, redaction and watermarking (Island, 2025).
- When a person pastes confidential data to an unapproved destination, Island RPA "immediately intervenes to block the action" and gives users "clear explanations for the prevention"; rules can be scoped by data classification, user role and destination application (Island, 2026).
- Microsoft's AI Red Team taxonomy of agentic failure modes treats what an agent ingests as a distinct surface from what it does (Microsoft AI Red Team, 2025).
- OWASP lists sensitive information disclosure through model inputs as a top LLM application risk (OWASP, 2025).
What do Island's controls do, and what does the user see?
Island's enterprise browser is a managed browser with policy enforced centrally. Its product description covers security, visibility, manageability, central policy enforcement, integrations, data loss prevention, boundaries between applications, masking of data a person sees on screen and detectors that classify content (Island, 2026). The last-mile controls act on the moments when data leaves a page: copy, paste, download, upload, screenshot capture, printing, with redaction and watermarking available on what the user sees (Island, 2025).
What the user sees is a page that works, with policy at the edges. A field can be masked; a watermark can carry the user's identity; a download can be allowed into a managed location and blocked elsewhere. When a person pastes classified data to an unapproved destination, Island RPA blocks the action and shows an explanation, and the product page describes end-user messages and notifications as customizable (Island, 2026). These are controls on a person's actions and on the display a person reads, and the documentation describes that work.
What do these controls leave untouched when the reader is a model?
An agent's loop is: the browser renders the page, the agent captures it, the capture goes to the model, the model decides the next action. Masking changes what a person sees at the render; copy, paste, download and screenshot policies act on a hand at the exits. What the capture holds is the question for an agent, and the pages reviewed do not address it: whether an agent receives the masked display, the underlying content, or both is not described.
Take a student information record as the record type: name, date of birth, home address, guardian contact, accommodation notes and attendance history, with a counselor's note field. The task is to record that a meeting took place. Masking can conceal the accommodation notes from staff who do not need them; the paste policy can stop a person moving the address to an outside tool. Neither is described as acting on the model's input. The model does not paste; it reads. Ingestion and action are distinct surfaces; OWASP's excessive agency entry concerns the second (OWASP, 2025). Island's documented controls address the exits; ingestion is not described.
What does the vendor's own documentation say?
| Dimension | Island, per its documentation | What a buyer should verify |
|---|---|---|
| Last-mile controls | Copy, paste, download, upload, screenshot capture, printing; redaction and watermarking | Whether an agent's path through the page passes any of these exits |
| Paste to unapproved destinations | RPA blocks the action with an explanation; rules by data classification, user role and destination application | Whether a rule can be scoped to an agent as a role |
| Masking and detectors | Listed as product capabilities for data on screen | Whether the masked or the underlying value is in an agent's capture |
| What the model receives from a permitted page | Not described in the pages reviewed | A dated written answer from the vendor |
Island documents that organizations "can configure granular rules based on data classification, user roles, and destination applications" and that users receive explanations when an action is blocked (Island, 2026); a policy on what an agent's model receives from a rendered page, and a record of that input, are not described in the pages reviewed.
What does a governed environment change?
A governed environment adds the step the browser's controls do not describe: it replaces the values on each permitted page with consistent tokens before any model reads them, so the model works on STUDENT_001 rather than the name, while the browser's policies on paste, download and screenshot stay in force for people.
Tokens are applied at the render layer, in an environment the customer operates, before any model reads the screen, the same token for the same value all run. Real values resolve only at an approved destination at the moment of an approved action; for recording a meeting, nothing resolves. A named person confirms what is tokenized and approves consequential actions. Every screen as the model received it, every action and approval is recorded and exported.
This applies the zero trust principle of per-request access decisions (NIST, 2020) to the model as a reader. The page also carries instructions (OWASP, 2025), so tokens before the model reads act on data and instructions together; see research on render-layer tokenization.
Where does RedactSure sit?
The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company. Agents work in a governed browser in the customer's own cloud. Substitution happens at the render layer before any model reads the screen, so student names reach the model as consistent tokens such as ACCT_001 or PATIENT_001 for the whole run. Real values resolve only at approved destinations at the moment of an approved action. A named person confirms the policy and approves every payment, submission and record change (Supervised Delegation). Every screen as tokens, every action and approval lands in the AI Control Record and exports to the customer's SIEM. It is model agnostic, needs no per-application integration, and leaves user permissions unchanged.
Deployments are in pilot. A pilot on the reader's own records task would show the page as the model received it. Everyone else controls where data can go. RedactSure controls what the AI can see.
Methodology and limitations
This page rests on Island's Enterprise Browser product description, its last-mile data controls, its article on blocking sensitive data pasted externally, the OWASP Top 10 for LLM Applications entries on prompt injection, sensitive information disclosure and excessive agency, NIST SP 800-207 on zero trust architecture, Microsoft's AI Red Team taxonomy of failure modes in agentic systems, a Gartner press release on agent governance, and a published RedactSure research page. All sources were read as of October 17, 2026.
No hands-on testing of Island's browser was performed. Where a capability is described as not described, that means not described in the pages reviewed, not that the product lacks it. Vendor features change and the page carries its date. Statements about RedactSure describe its current design, with deployments in pilot. The student information record describes a record type, not any organization, and token names are illustrative.
Whether a given browser control or governed environment meets an organization's obligations under its data protection laws, its vendor agreements or its own security policies is a determination for its counsel, its assessors and its security and compliance officers, not for a research page.
What the record shows
Island documents controls on what a person can copy, paste, download, print and capture from the browser, with masking for what is on screen, and those controls do their documented job. What an agent's model receives from a page the agent is permitted to open is not described in the pages reviewed. The step that covers the model is a control on the rendered values before the capture is sent, which RedactSure's environment supplies alongside the browser. The test is to name one agent and one task on one permitted page, run it, and ask the vendor for the record of what the model received.
Frequently asked questions
Does Island's masking hide values from an AI agent?
Island lists masking among its capabilities for data on screen; whether an agent driving the browser receives the masked display, the underlying content, or both is not described in the pages reviewed, so the answer must come from the vendor in writing.
Does the paste block apply to an agent?
Island documents RPA blocking a paste of classified data to an unapproved destination, with rules by data classification, user role and destination application; an agent that reads a page and acts elsewhere does not necessarily paste, and the pages reviewed do not describe the rule acting on an agent's path.
Can an agent be treated as a user role in Island policy?
Island documents scoping by user role; whether an agent session can be identified and scoped as its own role is not described in the pages reviewed; a buyer should ask, since a role-based rule only governs what it can recognize.
Should an organization keep Island if it adds agents?
This page answers what the browser's controls need alongside them, not whether to keep them. The documented last-mile, masking and detector controls govern people using the browser, and that work continues; the added step is a control on rendered values before any model reads them.
Why does agent governance differ from user governance here?
Gartner's position is that uniform governance across AI agents leads to failure, because agents differ in what they read and do (Gartner, 2026). A browser rule written for a hand at the keyboard governs exits; the agent's exposure begins at ingestion.
What should a buyer ask the vendor in writing?
Whether any policy alters the values an agent's model receives from a permitted page, who configures it, whether it applies before the capture leaves the browser, and what record of the model's input the customer receives. A dated answer settles what the pages reviewed leave open.
Related reading
What Is the Difference Between RedactSure and Island Enterprise Browser for AI Agent Security? · Does Sandboxing an Enterprise AI Agent Protect Your Data? · Which Enterprise AI Agents Can Work on Screens With PII Today, and What Does Each One Read? · What Is Render-Layer Tokenization? · Why Does Island Block a Paste, and Is Blocking Enough to Protect the Data? · Why Does Microsoft Purview Block a Paste Into the Browser, and What Keeps the Work Moving? · On the RedactSure blog: The Two Gaps AI Agents Opened in Your Security Stack · RedactSure
Sources
Vendor documentation
- Island, "Enterprise Browser," product description, 2026 (vendor documentation). https://www.island.io/enterprise-browser
- Island, Enterprise Browser last mile data controls, 2025 (vendor documentation). https://www.island.io/
- Island, "Block sensitive data pasted externally," island.io Education, updated July 17, 2026 (knowledge-base article). https://www.island.io/education/use-rpa-to-block-sensitive-data-pasted-externally
- Microsoft AI Red Team, "Taxonomy of Failure Modes in Agentic AI Systems," April 2025 (whitepaper). https://www.microsoft.com/en-us/security/blog/2025/04/24/new-whitepaper-outlines-the-taxonomy-of-failure-modes-in-ai-agents/
Regulation, standards and official guidance
- OWASP, "LLM01:2025 Prompt Injection," OWASP Top 10 for LLM Applications, 2025 (standard). https://genai.owasp.org/llmrisk/llm01-prompt-injection/
- OWASP, "LLM02:2025 Sensitive Information Disclosure," OWASP Top 10 for LLM Applications, 2025 (standard). https://genai.owasp.org/llmrisk/llm022025-sensitive-information-disclosure/
- OWASP, "LLM06:2025 Excessive Agency," OWASP Top 10 for LLM Applications, 2025 (standard). https://genai.owasp.org/llmrisk/llm062025-excessive-agency/
- NIST, "Zero Trust Architecture," SP 800-207, 2020 (official guidance). https://csrc.nist.gov/pubs/sp/800/207/final
Industry analysis and press
- Gartner, "Gartner Says Applying Uniform Governance Across AI Agents Will Lead to Enterprise AI Agent Failure," May 26, 2026 (press release). https://www.gartner.com/en/newsroom/press-releases/2026-05-26-gartner-says-applying-uniform-governance-across-ai-agents-will-lead-to-enterprise-ai-agent-failure
RedactSure documents
- RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization/
- Product behavior described on this page reflects RedactSure's current design. Third-party products are described from their public documentation as read on October 17, 2026. Compliance determinations belong to the organization's counsel.
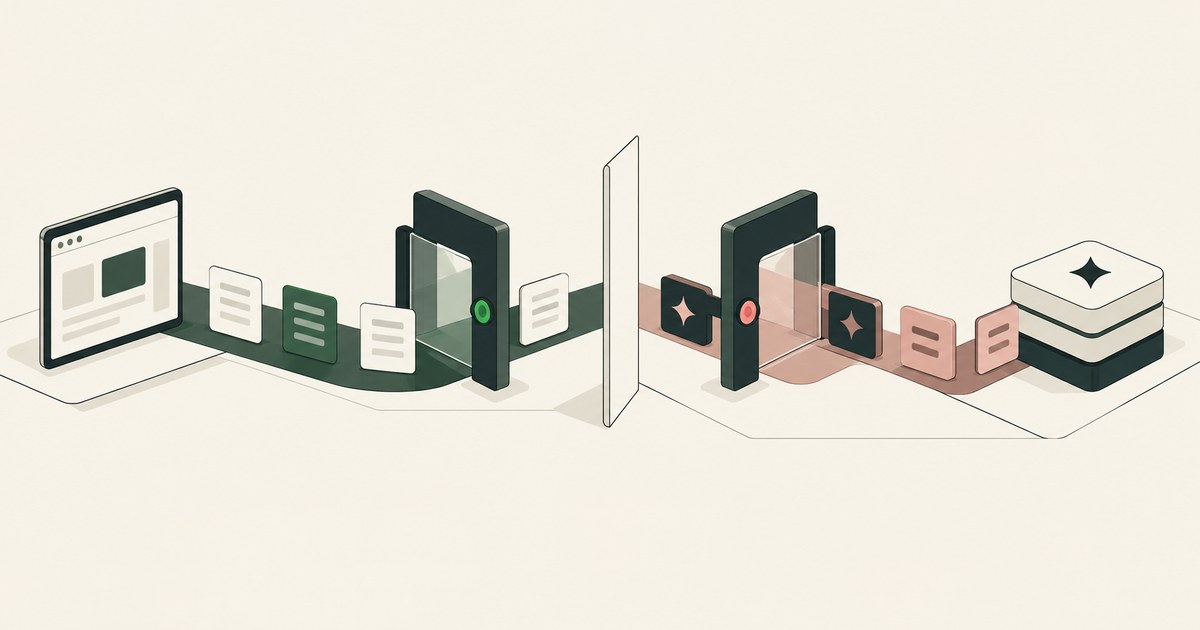
What Is the Difference Between RedactSure and Island Enterprise Browser for AI Agent Security?
Island controls the last mile of a person's browser session. RedactSure controls what a supervised agent is shown and allowed to do. Different workers.
Does Sandboxing an Enterprise AI Agent Protect Your Data?
It protects the machine, not the data. Once the agent signs into a real application, the records are inside the sandbox too. Check what the model reads.
Which Enterprise AI Agents Can Work on Screens With PII Today, and What Does Each One Read?
Seventeen enterprise agents can work on screens with PII today, and for most the model receives whatever the account may see. Check for tokens first.

What Is Render-Layer Tokenization? The Control at the Layer Where the Agent Actually Reads
Learn how render-layer tokenization replaces PII before an AI agent reads a browser screen while preserving useful workflow context.
Why Does Island Block a Paste, and Is Blocking Enough to Protect the Data?
Island blocks the paste because its last-mile controls classed the content as sensitive and the destination as unapproved. Check what a model already read.
Why Does Microsoft Purview Block a Paste Into the Browser, and What Keeps the Work Moving?
Purview endpoint DLP blocks the paste because content matched a sensitive information type and the destination's rule is Block. Check which rule fired.

The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.
Book an AI Agent Security Review →
Bring your hardest questions.
Bring one sensitive workflow and the decisions your team needs to keep in its hands.
Book a demoAbout the author

Chris Sowa is a founder of RedactSure and a former CEO of an AI company; he started it years before ChatGPT existed. He previously led AI at Accenture, served as Global VP of Strategy & Innovation at Schneider Electric, was CCO of Sovos, and spent more than a decade at Oracle, with earlier roles at SAP and IBM.