
Explainer · By Chris Sowa · Published
Last updated
Why Does Microsoft Purview Block a Paste Into the Browser, and What Keeps the Work Moving?
Purview endpoint DLP blocks the human paste because the content matched a sensitive information type and the destination sits in a sensitive service domain group whose rule is set to Block or Block with override. Check which rule fired, whether override with justification fits the workflow, and whether the value can be substituted so the task finishes.
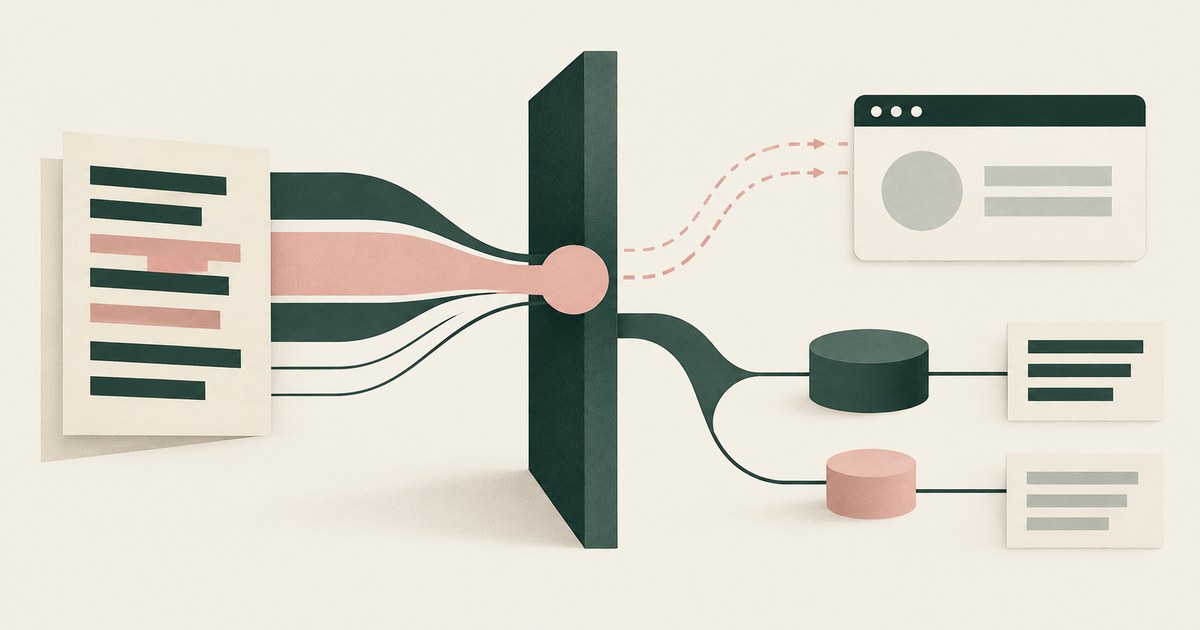
Purview endpoint DLP blocks the human paste because the content matched a sensitive information type and the destination sits in a sensitive service domain group whose rule is set to Block or Block with override. Check which rule fired, whether override with justification fits the workflow, and whether the value can be substituted so the task finishes. It covers what Microsoft documents, what the block protects and costs, and the step a block cannot take, building on research on reducing false positives in Microsoft Purview DLP.
Key findings
- Microsoft documents the control as a way to "restrict users from pasting sensitive content into browser-based applications," enforced per destination through sensitive service domain groups, with the restriction set to "Audit, Block with override, or Block" (Microsoft, 2026).
- Edge shows "policy-evaluation and check-complete notifications," while Chrome and Firefox show a "policy-evaluation toast"; the exact dialog text is not printed in the documentation (Microsoft, 2026).
- OWASP treats sensitive data entering a model's input as the disclosure event a paste block is meant to prevent (OWASP, 2025).
- A block protects the destination and leaves the task unfinished; replacing the value before it moves is the method described in research on render-layer tokenization.
What does Purview's paste restriction do, and what does the user see?
The control is an endpoint DLP setting, "Browser and domain restrictions to sensitive data," paired with "Sensitive service domain groups" that name the destinations. A DLP rule then uses the action "Audit or restrict activities on devices" with the activity "Paste to supported browsers," and the administrator can "Set the restriction to Audit, Block with override, or Block." Supported browsers are Edge on Windows and macOS, Chrome and Firefox on Windows and macOS with the Purview extension on Windows only, and Safari on macOS (Microsoft, 2026).
What the user sees depends on the browser. Microsoft states that "notifications are triggered when policy for the target website is configured to Block or Block with override paste to browser for that user." Edge shows policy-evaluation and check-complete notifications; Chrome and Firefox show a policy-evaluation toast. The documentation does not print the message text, so the wording users report is whatever the notification displays. With Block with override, the user can supply a justification and proceed; with Block, the paste does not happen.
What does the block protect, and what does it cost the task?
Take a student record as the record type. A registrar has a student's name, date of birth and student identifier open in the student information system and wants to paste a paragraph into a web-based AI assistant to draft a letter home. If the selection carries the identifier, the content matches a sensitive information type, the assistant's domain is in a restricted group, and the paste is blocked.
What it protects is the destination. The data never reaches the external site, which is the event OWASP describes when personal data enters a model's input (OWASP, 2025). It also enforces a boundary of the kind NIST's zero trust guidance describes (NIST, 2020).
What it costs is the task. The letter is not drafted. The registrar retypes the paragraph without identifiers or uses the override. Override records a justification and lets the data move, recovering the task by giving up the protection. Block has no third option: it cannot hand the assistant a working stand-in for the student identifier so the draft proceeds and the real value is filled in later by someone authorized.
What does the vendor's own documentation say?
The paste restriction requires "rules configured with Sensitive service domain groups" and governs the human paste. Purview's coverage for custom AI applications applies to "custom AI apps that are registered with Entra for user authentication, and integrated with the Microsoft Purview SDK," and "requires you to enable pay-as-you-go billing in your organization"; it covers neither agents nor browsers (Microsoft, 2026). DLP for Microsoft 365 Copilot is another location (Microsoft, 2025).
| Dimension | Microsoft, per its documentation | What to verify |
|---|---|---|
| Paste action | Audit, Block with override, Block | Which setting each group uses |
| Scope | Human paste to supported browsers, by domain group | Whether the AI site is grouped |
| Substituting the value | Not described in the pages reviewed | How the task finishes |
Whether it governs what a computer-using agent reads is raised in a Q&A thread (Microsoft, 2026), not in the pages reviewed.
What does a governed environment change?
A governed environment changes the moment at which the sensitive value is handled. Purview's paste restriction acts when the identifier is already on the clipboard. A governed environment replaces the value before any model reads the page, so there is nothing sensitive to paste and no override to justify.
On the student record, the name renders to the model as STUDENT_001 and the identifier as ID_001, consistently for the whole run. An assistant drafting the letter works on those tokens. The real values resolve only at an approved destination, the student information system's own correspondence field, at the moment of an approved action, and a named person approves that submission. Every screen as the model saw it, every action and every approval is recorded and exported to the organization's own logging. NIST's AI risk framework calls for AI risk to be governed, mapped, measured and managed with a reviewable record (NIST, 2023).
Blocking protects the destination and ends the task; substitution protects the value and lets the task finish. The Purview rule still does its documented job for human pastes to restricted domains.
Where does RedactSure sit?
The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company. Assistants work in a governed environment in the customer's cloud. Substitution happens at the render layer before any model reads the student record, so the identifier arrives as a consistent token such as ID_001 for the whole run. Real values resolve only at approved destinations at the moment of an approved action. A named person confirms the tokenization policy and approves every payment, submission and record change (Supervised Delegation). Every screen as tokens, every action and approval lands in the AI Control Record and exports to the customer's SIEM. It is model agnostic and leaves user permissions unchanged.
Deployments are in pilot. A pilot on the reader's own family correspondence workflow would show the letter drafted on tokens and the exported record. Everyone else controls where data can go. RedactSure controls what the AI can see.
Methodology and limitations
This page rests on Microsoft Learn documentation for restricting paste actions into browsers with Purview endpoint DLP, for Purview coverage of Entra-registered AI applications and for DLP with Microsoft 365 Copilot, a public Microsoft Q&A thread on Copilot computer-use coverage, the OWASP Top 10 for LLM Applications entry on sensitive information disclosure, NIST SP 800-207, the NIST AI Risk Management Framework, and published RedactSure research pages. All sources were read as of October 17, 2026.
No hands-on testing of Purview was performed. Where a capability is described as not described, the statement means not described in the pages reviewed, not that the product lacks it. The notification text is not printed in the documentation, so any wording quoted by users is what they report, not an official string. Vendor features change and the page carries its date. Statements about RedactSure describe its current design, with deployments in pilot. The student record is a record type, not an organization.
Whether a given paste policy or substitution control meets an organization's obligations under FERPA, state student privacy laws or its own policies is a determination for its counsel, assessors and its own security and compliance officers.
What the record shows
The block is Purview endpoint DLP enforcing a rule that matched a sensitive information type on a human paste to a domain in a restricted group, set to Block or Block with override. The documentation offers Audit, Block with override and Block. A block protects the destination and ends the task; an override recovers the task and lets the data move. Neither supplies a working substitute, the step a governed environment adds. The test is to name one task and one screen, such as drafting a letter home from a student record, and ask whether the work finished without the real value leaving the system.
Frequently asked questions
Why is the paste blocked in Chrome but not in another browser?
Enforcement depends on the browser. Microsoft lists Edge on Windows and macOS, Chrome and Firefox with the Purview extension on Windows only, and Safari on macOS. A browser outside that list, or a Chrome install without the extension, is not enforced.
What does Block with override do?
It shows the user a notice and lets them proceed after supplying a justification. The paste then happens and the justification is recorded. It keeps the work moving at the cost of the protection, so it fits workflows where the audit trail matters more than stopping the flow.
Can an administrator exempt one site?
Yes, by how the sensitive service domain groups are built. The rule applies to the domains in the group, so a destination outside the group is not restricted for that rule. Exemptions by data type within a destination are a matter of the rule's conditions.
Does the paste rule stop an AI assistant or agent from reading the screen?
The documentation describes the control as restricting the human paste action into supported browsers. Whether it governs what a computer-using agent reads from a rendered page is raised in a public Q&A thread and is not described in the pages reviewed. A model that reads a page receives what is on the page.
Does Purview's AI app coverage address the same problem?
No. That coverage applies to custom AI apps registered with Entra and integrated with the Purview SDK, and requires pay-as-you-go billing. Browser-based AI sites are handled by the endpoint DLP paste restriction, a separate scope.
What does substitution add that blocking does not?
A block cannot let the task complete without the real value. Substitution replaces the value with a consistent token before the model reads the page, so a draft is written on tokens and the real value resolves only at an approved destination with a named approver. The two controls act at different points and can run together.
Related reading
How to reduce false positives in Microsoft Purview DLP? · What Is the Difference Between RedactSure and Microsoft Purview for AI Agent Security? · Does Purview DLP Cover Computer-Using AI Agents? · What Is Render-Layer Tokenization? · Why Does Prisma Browser Say "Pasting This Data Is Prohibited," and What Makes the Policy Workable? · Why Does Island Block a Paste, and Is Blocking Enough to Protect the Data? · Is Prisma Browser Enough to Protect Data From AI Agents? · On the RedactSure blog: The Two Gaps AI Agents Opened in Your Security Stack · RedactSure
Sources
Vendor documentation
- Microsoft, "Help prevent leakage of sensitive content by restricting paste actions into browsers," Microsoft Learn (Purview), updated June 26, 2026 (how-to). https://learn.microsoft.com/en-us/purview/endpoint-dlp-create-policy-restrict-paste-in-browsers
- Microsoft, "Use Microsoft Purview to manage data security & compliance for Entra-registered AI apps," Microsoft Learn, May 1, 2026 (vendor documentation). https://learn.microsoft.com/en-us/purview/ai-entra-registered
- Microsoft, "Microsoft Purview DLP for Microsoft 365 Copilot," Microsoft Learn, 2025 (vendor documentation). https://learn.microsoft.com/en-us/purview/dlp-microsoft365-copilot-location-learn-about
- Microsoft Q&A, "Clarification on Purview DLP Coverage for Copilot 'Computer Use' Data Exfiltration Scenario," 2026 (vendor forum). https://learn.microsoft.com/en-gb/answers/questions/5915515/clarification-on-purview-dlp-coverage-for-copilot
Regulation, standards and official guidance
- OWASP, "LLM02:2025 Sensitive Information Disclosure," OWASP Top 10 for LLM Applications, 2025 (industry standard). https://genai.owasp.org/llmrisk/llm022025-sensitive-information-disclosure/
- NIST, "Zero Trust Architecture," SP 800-207, 2020 (official guidance). https://csrc.nist.gov/pubs/sp/800/207/final
- NIST, "Artificial Intelligence Risk Management Framework (AI RMF 1.0)," NIST AI 100-1, 2023 (official guidance). https://www.nist.gov/itl/ai-risk-management-framework
RedactSure documents
- RedactSure Research, "How to reduce false positives in Microsoft Purview DLP?" (2026). https://redactsure.com/research/how-to-reduce-false-positives-in-microsoft-purview-dlp/
- RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization/
- Product behavior described on this page reflects RedactSure's current design. Third-party products are described from their public documentation as read on October 17, 2026. Compliance determinations belong to the organization's counsel.
How to reduce false positives in Microsoft Purview DLP?
Review reduce false positives in Microsoft Purview DLP, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
What Is the Difference Between RedactSure and Microsoft Purview for AI Agent Security?
Microsoft Purview governs the data estate and whether an AI tool may process labeled content. RedactSure governs what the agent's model gets per screen.
Does Purview DLP Cover What a Computer-Using Agent Reads?
Assess Purview DLP coverage for AI agent sessions handling PII and payments, including screenshot inputs, file uploads and endpoint controls.

What Is Render-Layer Tokenization? The Control at the Layer Where the Agent Actually Reads
Learn how render-layer tokenization replaces PII before an AI agent reads a browser screen while preserving useful workflow context.
Why Does Prisma Browser Say "Pasting This Data Is Prohibited," and What Makes the Policy Workable?
The message is Prisma Browser's Clipboard Policy blocking a paste whose content matched a sensitive pattern. Check which rule fired and whether to swap.
Why Does Island Block a Paste, and Is Blocking Enough to Protect the Data?
Island blocks the paste because its last-mile controls classed the content as sensitive and the destination as unapproved. Check what a model already read.
Is Prisma Browser Enough to Protect Data From AI Agents?
Prisma Browser governs what a person does with data in the browser, and its controls do that job; what a model gets from a permitted page is undocumented.

The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.
Book an AI Agent Security Review →
Bring your hardest questions.
Bring one sensitive workflow and the decisions your team needs to keep in its hands.
Book a demoAbout the author

Chris Sowa is a founder of RedactSure and a former CEO of an AI company; he started it years before ChatGPT existed. He previously led AI at Accenture, served as Global VP of Strategy & Innovation at Schneider Electric, was CCO of Sovos, and spent more than a decade at Oracle, with earlier roles at SAP and IBM.