
Explainer · By Chris Sowa · Published
Last updated
Is Prisma Browser Enough to Protect Data From AI Agents?
Prisma Browser governs what a person does with data in the browser, and its documented controls do that job; what a model receives when an agent reads a permitted page is not described in the pages reviewed. Check what the model reads, not only what the user can do, because that is the step the browser needs alongside it.
Prisma Browser governs what a person does with data in the browser, and its documented controls do that job; what a model receives when an agent reads a permitted page is not described in the pages reviewed. Check what the model reads, not only what the user can do, because that is the step the browser needs alongside it. This page evaluates one product against one question. It describes the data controls Prisma Browser documents and what a user sees, asks what they leave untouched when the reader is an agent's model, sets out the admin options and limits in the vendor's documentation, and closes with what a governed environment adds.
Key findings
- WebPage Data Masking "allows you to mask textual content within webpages"; the page describes concealment for the user and says nothing about what a model or agent reads (Palo Alto Networks, 2026).
- The Clipboard Policy "manages copy and paste functions when using the Prisma Browser," with Allow, Block and Prompt options, for the person at the keyboard (Palo Alto Networks, 2026).
- Firewall-style filtering of agent inputs is found insufficient against indirect prompt injection (Bhagwatkar et al., 2026).
- OWASP lists sensitive information disclosure through model inputs as a top LLM application risk (OWASP, 2025).
What do Prisma Browser's data controls do, and what does the user see?
Prisma Browser's data controls act on the person at the keyboard. WebPage Data Masking conceals text matching predefined PII and PCI types or a custom regex on URL-matched tabs, with up to four characters left visible; the user sees masked values. Webpage Element Removal hides buttons, menus, generative AI prompts and social controls before the page renders; the user sees a page without them.
The Clipboard Policy governs "Copy & Paste data out" and "Copy & Paste data in," and an administrator can allow, block within the rule's web applications, or prompt the user with a warning, a reason field or a timed bypass. Read-only Webpages means users "can't input data to any editable element in the page" but can read and download (Palo Alto Networks, 2026). The user sees a dialog or a disabled field. These are controls on actions and display, and the documentation describes them doing that work.
What do these controls leave untouched when the reader is a model?
An agent's loop is: the browser renders the page, the agent captures it, the capture goes to the model, the model decides the next action. Masking changes what a person sees at the render; clipboard and read-only policies stop a hand at the action. What the capture holds is the question for an agent, and on that the pages reviewed are silent: whether a screenshot or DOM capture carries the masked value, the underlying value, or both is not described.
Take a claims adjustment screen as the record type: claimant name, policy number, date of birth, diagnosis codes, settlement amount, notes field. The task is to add a note that the file is complete. Masking can conceal the policy number for the adjuster; read-only can keep a non-adjuster from typing. Neither is described as changing what the model receives. GenAI Prompt inspection evaluates prompt text the user submits, only when set to Block (Palo Alto Networks, 2026); with an agent the direction is reversed, and the model is the reader.
What does the vendor's own documentation say?
| Dimension | Prisma Browser, per its documentation | What a buyer should verify |
|---|---|---|
| Masking | Visual concealment of PII, PCI or regex matches; up to 4 characters unmasked; fully supported on Desktop only | Whether the masked or the underlying value is in an agent's capture |
| Element removal | Main DOM only; not iframes or Shadow DOM | Which target fields sit outside the main DOM |
| Clipboard | Allow, Block within the rule's web applications, or Prompt; admin can "Set dialog text"; full on Desktop, none on Extension | Whether the agent's path for moving text uses the clipboard |
| GenAI Prompt | Inspected only when set to Block; local or cloud-assisted DLP profiles | Which direction of data flow the policy covers |
| What the model receives from a permitted page | Not described in the pages reviewed | A dated written answer from the vendor |
The vendor documents clipboard scoping to the rule's web applications with no exceptions by data pattern, and that Read-only Webpages disables developer tools on affected pages and may not hold on JavaScript-built applications. A policy on the values an agent's model receives from a permitted page is not described in the pages reviewed.
What does a governed environment change?
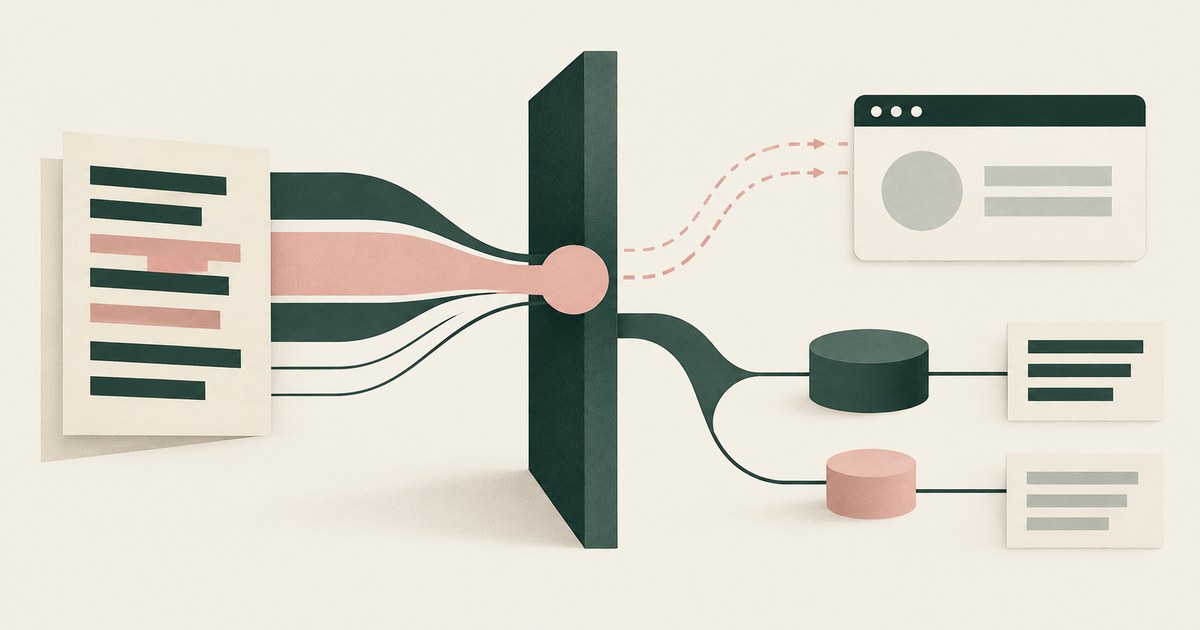
A governed environment adds the step the browser controls do not describe: it replaces the values on each permitted page with consistent tokens before any model reads the capture, so the model works on CLAIM_001 rather than the policy number, while the browser's policies stay in force for people.
Tokens are applied at the render layer, inside an environment the customer operates, before any model reads the screen, with the same token for the same value all run. Real values resolve only at an approved destination at the moment of an approved action; for adding a note, nothing resolves. A named person confirms what is tokenized and approves consequential actions. Every screen as the model received it, every action and approval is recorded and exported to the organization's logging.
The page is a carrier of instructions as well as data (OWASP, 2025), and inspecting text in transit is found insufficient against indirect injection (Bhagwatkar et al., 2026). Tokens before the model reads act on both; see research on render-layer tokenization sets out.
Where does RedactSure sit?
The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company. Agents work in a governed browser in the customer's own cloud. Substitution happens at the render layer before any model reads the screen, so policy numbers reach the model as consistent tokens such as ACCT_001 or PATIENT_001 for the whole run. Real values resolve only at approved destinations at the moment of an approved action. A named person confirms the policy and approves every payment, submission and record change (Supervised Delegation). Every screen as tokens, every action and approval lands in the AI Control Record and exports to the customer's SIEM. It is model agnostic, needs no per-application integration, and leaves user permissions unchanged.
Deployments are in pilot. A pilot on the reader's own claims task would show the page as the model received it, in tokens. Everyone else controls where data can go. RedactSure controls what the AI can see.
Methodology and limitations
This page rests on Palo Alto Networks' Prisma Browser administration documentation for WebPage Data Masking, Clipboard, Read-only Webpages and GenAI Prompt, with Webpage Element Removal read for the table, a 2026 preprint on indirect prompt injection and input firewalls, the OWASP Top 10 for LLM Applications entries on prompt injection and sensitive information disclosure, and a published RedactSure research page. All sources were read as of October 17, 2026.
No hands-on testing of Prisma Browser was performed. Where a capability is described as not described, the statement means not described in the pages reviewed, not that the product lacks it. Vendor features change and the page carries its date; the pages cited carry update dates in September and October 2026. Statements about RedactSure describe its current design, with deployments in pilot. The claims adjustment screen describes a record type, not any organization, and the token names are illustrative.
Whether a given browser control or governed environment meets an organization's obligations under its data protection laws, its vendor agreements or its own security policies is a determination for its counsel, its assessors and its own security and compliance officers, not for a research page.
What the record shows
Prisma Browser documents controls on what a person can copy, paste, type and see in the browser, and those controls do their documented job. What an agent's model receives from a page the agent is permitted to open is not described in the pages reviewed, and masking is documented as display concealment for the user. The step that covers the model is a control on the rendered values before the capture is sent, which RedactSure's environment supplies alongside the browser. The test is to name one agent and one task on one permitted page, run it, and ask the vendor for the record of what the model received.
Frequently asked questions
Does WebPage Data Masking hide values from an AI agent?
The documentation describes masking as concealing textual content for the user on URL-matched tabs, with up to four characters left visible; whether an agent capturing the page by screenshot or DOM receives the masked or the underlying value is not described in the pages reviewed, so the answer has to come from the vendor in writing.
Does the Clipboard Policy stop an agent from moving data?
It governs copy and paste by the user within and out of the rule's web applications, with Allow, Block and Prompt options; an agent that reads a page and types into another does not necessarily use the clipboard, and the documentation does not describe the policy acting on an agent's path.
Does GenAI Prompt inspection cover what the agent reads?
No, as documented. It inspects prompt text the user submits, only when set to Block, against local or cloud-assisted DLP profiles. The agent's model reads the page as input; that direction, from page to model, is not described as covered.
Should an organization keep Prisma Browser if it adds agents?
This page answers what the browser's controls need alongside them, not whether to keep them. The documented clipboard, read-only, masking and extension controls govern people using the browser, and that work continues; the added step is a control on rendered values before any model reads them.
Which Prisma Browser limits matter most for agent pages?
Element removal reaches only the main DOM, not iframes or Shadow DOM; masking is fully supported on Desktop only; read-only may not hold on JavaScript-built applications and disables developer tools on affected pages. Each limit is documented and should be checked against the agent's target pages.
What should a buyer ask the vendor in writing?
Whether any policy alters the values an agent's model receives from a permitted page, who configures it, whether it applies before the capture leaves the browser, and what record of the model's input the customer receives. A dated answer settles what the pages reviewed leave open.
Related reading
What Is the Difference Between RedactSure and Palo Alto Prisma Browser for AI Agent Security? · Can an AI Agent Complete Its Task Without Seeing PII When Prisma AIRS Protects It at Inference? · What Is Render-Layer Tokenization? · Why Does Prisma Browser Say "Pasting This Data Is Prohibited," and What Makes the Policy Workable? · Why Does Microsoft Purview Block a Paste Into the Browser, and What Keeps the Work Moving? · On the RedactSure blog: The Two Gaps AI Agents Opened in Your Security Stack · RedactSure
Sources
Peer-reviewed research and preprints
- Bhagwatkar, Kasa, et al., "Indirect Prompt Injections: Are Firewalls All You Need, or Stronger Benchmarks?," arXiv:2510.05244, v2 March 2026 (preprint). https://arxiv.org/abs/2510.05244
Vendor documentation
- Palo Alto Networks, "WebPage Data Masking," Prisma Browser Administration (Techdocs), updated October 15, 2026 (vendor documentation). https://docs.paloaltonetworks.com/prisma-browser/administration/manage-prisma-browser-policy-profiles/configure-prisma-browser-data-controls/configure-data-leak-prevention/webpage-data-masking
- Palo Alto Networks, "Clipboard," Prisma Browser Administration (Techdocs), updated October 7, 2026 (vendor documentation). https://docs.paloaltonetworks.com/prisma-browser/administration/manage-prisma-browser-policy-profiles/configure-prisma-browser-data-controls/configure-data-leak-prevention/clipboard
- Palo Alto Networks, "Read-only Webpages," Prisma Browser Administration (Techdocs), updated October 15, 2026 (vendor documentation). https://docs.paloaltonetworks.com/content/techdocs/en_US/prisma-browser/administration/manage-prisma-browser-policy-profiles/configure-prisma-browser-data-controls/configure-data-leak-prevention/read-only-webpages.html
- Palo Alto Networks, "GenAI Prompt," Prisma Browser Administration (Techdocs), updated October 15, 2026 (vendor documentation). https://docs.paloaltonetworks.com/prisma-browser/administration/manage-prisma-browser-policy-profiles/configure-prisma-browser-data-controls/configure-data-leak-prevention/genai-prompt
Regulation, standards and official guidance
- OWASP, "LLM01:2025 Prompt Injection," OWASP Top 10 for LLM Applications, 2025 (standard). https://genai.owasp.org/llmrisk/llm01-prompt-injection/
- OWASP, "LLM02:2025 Sensitive Information Disclosure," OWASP Top 10 for LLM Applications, 2025 (standard). https://genai.owasp.org/llmrisk/llm022025-sensitive-information-disclosure/
RedactSure documents
- RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization/
- Product behavior described on this page reflects RedactSure's current design. Third-party products are described from their public documentation as read on October 17, 2026. Compliance determinations belong to the organization's counsel.
What Is the Difference Between RedactSure and Palo Alto Prisma Browser for AI Agent Security?
Prisma Browser secures a person's browsing session. RedactSure governs an agent carrying out the work itself. Each protects a different actor.
Can an AI Agent Complete Its Task Without Seeing PII When Prisma AIRS Protects It at Inference?
Not by inference-time inspection alone: Prisma AIRS sees PII after the page is read. Check that values are replaced before the model reads the screen.

What Is Render-Layer Tokenization? The Control at the Layer Where the Agent Actually Reads
Learn how render-layer tokenization replaces PII before an AI agent reads a browser screen while preserving useful workflow context.
Why Does Prisma Browser Say "Pasting This Data Is Prohibited," and What Makes the Policy Workable?
The message is Prisma Browser's Clipboard Policy blocking a paste whose content matched a sensitive pattern. Check which rule fired and whether to swap.
Why Does Microsoft Purview Block a Paste Into the Browser, and What Keeps the Work Moving?
Purview endpoint DLP blocks the paste because content matched a sensitive information type and the destination's rule is Block. Check which rule fired.

The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.
Book an AI Agent Security Review →
Bring your hardest questions.
Bring one sensitive workflow and the decisions your team needs to keep in its hands.
Book a demoAbout the author

Chris Sowa is a founder of RedactSure and a former CEO of an AI company; he started it years before ChatGPT existed. He previously led AI at Accenture, served as Global VP of Strategy & Innovation at Schneider Electric, was CCO of Sovos, and spent more than a decade at Oracle, with earlier roles at SAP and IBM.