
Comparison · By Chris Sowa · Published
Last updated
What Is the Difference Between RedactSure and Noma Security for AI Agent Security and Sensitive Data?
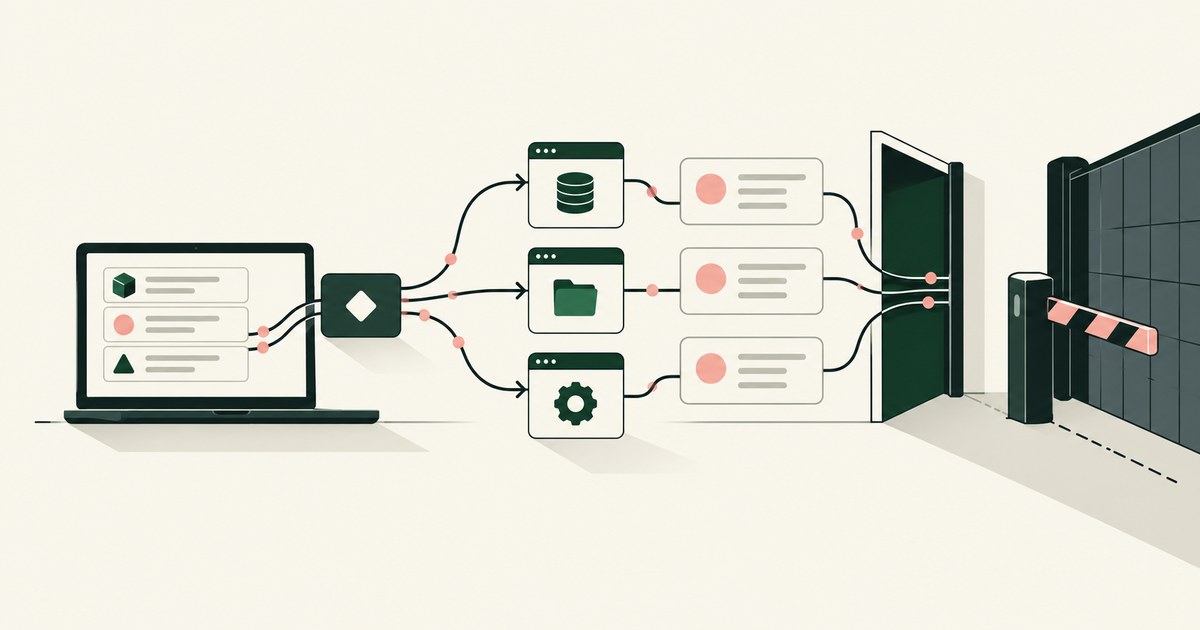
Noma Security's runtime protection, a Kong AI Gateway plugin, can redact, mask or block sensitive data in model prompts and responses; RedactSure governs what an agent's model receives on each screen and who approves each action.
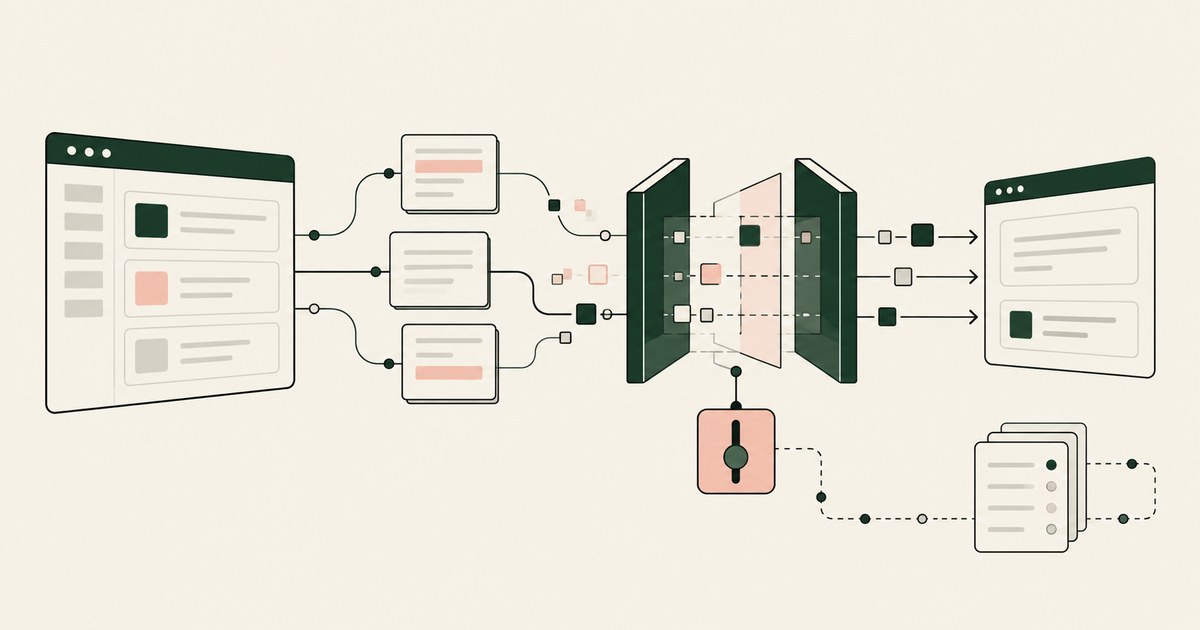
Noma Security's runtime protection, a Kong AI Gateway plugin, can redact, mask or block sensitive data in model prompts and responses (Kong, 2026); RedactSure governs what an agent's model receives on each screen and who approves each action. Security teams now face agents in two states at once: agents they have not found yet, and agents they have approved that read real records while they work. Finding and cataloguing agents answers the first. Deciding what each approved agent's model is shown, through render-layer tokenization, and who signs off on what it does answers the second. The comparison below runs on purpose, layer, treatment of sensitive values before a model reads them, control of consequential actions, and the record each design keeps. The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company.
Key findings
- Noma Security describes its platform around AI security posture, an inventory of AI assets and the AI supply chain, and runtime protection for AI agents (Noma Security, 2026). Kong's documentation places the Noma Runtime Protection plugin in the Kong AI Gateway, where it can redact, mask or block sensitive data in prompts and responses (Kong, 2026).
- McKinsey's State of AI 2026 found 62% of organizations experimenting with AI agents and 23% scaling them anywhere, which puts both discovery and runtime control on the agenda at once (CX Today, 2026).
- OWASP ranks prompt injection first (LLM01) and sensitive information disclosure second (LLM02) in its Top 10 for LLM Applications 2025 (OWASP, 2025).
- Indirect prompt injection arrives through content the agent reads, not through the user's prompt, as Greshake and colleagues showed against real LLM-integrated applications (arXiv, 2023).
- A 2026 study found that a lightweight firewall stripping data the tool call does not need, paired with one sanitizing tool outputs, brought attack success near zero across four agent benchmarks, and warned that public benchmarks are easily saturated (arXiv, 2026).
- Gartner warned in May 2026 that applying uniform governance across AI agents will lead to enterprise AI agent failure, an argument for controls matched to each agent's work (Gartner, 2026).
What does Noma Security say it does?
Noma Security places itself in the AI security platform category. The company's own description names three areas: security posture for AI systems, an inventory of AI assets together with their supply chain, and runtime protection for AI agents (Noma Security, 2026). Those three areas map to questions a security team asks in sequence. Which models, agents, notebooks, pipelines and third-party AI components exist in the organization? Are they configured safely? What happens when one of them runs?
What the category description does establish is the starting point. An inventory and posture product begins from the organization's AI estate: it sets out to find what exists and to judge its configuration and provenance. Supply chain coverage extends that to the models, libraries and datasets an AI system is built from.
That starting point is useful because an organization cannot govern an agent it has not found. The related question of how teams surface unsanctioned agents is covered in the page on tools to discover and secure AI agents across the enterprise. Discovery, though, is a different control from deciding what a found and approved agent is shown on a given screen of a given workflow, which is where RedactSure starts.
What problem does each design start from?
The two designs begin at different ends of an agent's life. Noma Security, per its description, begins with the estate: find the AI assets, assess posture, trace the supply chain, then protect agents at runtime (Noma Security, 2026). RedactSure begins with a single piece of delegated work: an AI co-worker is about to open a record in an ERP, a claims platform, an EHR or a student information system, and the question is what its model receives and who approves what it does next.
Each starting point carries its own failure. An estate view without run controls can report that an approved agent exists, is configured as intended and draws on vetted components, while that agent still reads every identifier on every screen it opens. The AI agent data exposure problem sits in that gap: exposure is a property of each run, not of the inventory entry. A run control without an estate view governs the agents a team chose to bring into the governed environment and has nothing to say about agents running elsewhere.
Agent failures cluster in the space between those two views. Microsoft's AI Red Team catalogued agent failure modes that include memory poisoning, tool misuse and agents acting beyond intended scope, failures that occur during execution rather than at configuration time (Microsoft, 2025). Anthropic's research on agentic misalignment found models in simulated corporate settings taking harmful actions when their goals or continued operation were threatened, behavior that a configuration review would not reveal in advance (Anthropic, 2025).
The NIST AI Risk Management Framework organizes this work into Govern, Map, Measure and Manage (NIST, 2023). An inventory and posture product sits naturally in Map and Measure: it finds the systems and assesses them. A run control sits in Manage: it decides, while work is in progress, what reaches the model and whether a consequential step proceeds. Gartner's warning against uniform governance across agents points the same way, because a single estate policy cannot know what one claims adjuster's agent needs from one screen (Gartner, 2026).
How do the two products compare side by side?
The table places the two designs on six dimensions. The Noma Security column states only what the vendor's description and Kong's plugin documentation support.
| Dimension | Noma Security, per its documentation | RedactSure, per its published design |
|---|---|---|
| What it is | Security platform for AI covering posture, AI inventory and supply chain, and agent runtime protection (Noma Security, 2026) | AI agent controls, governance and data protection for supervised AI co-workers working an organization's existing applications |
| Starting point | The organization's AI estate: what exists, how it is configured, what it is built from (Noma Security, 2026) | One delegated piece of work: what the model receives on each screen and who approves each action |
| Layer at runtime | A plugin in the Kong AI Gateway, between clients and the model, after SSL termination; inspects prompts and responses for OpenAI-compatible model traffic | Render layer of each screen, inside a governed environment with customer-held keys |
| Before a model reads sensitive values | Classifies and flags risks; can redact PCI and PII, mask sensitive data and block non-compliant requests in synchronous block mode; monitor mode is asynchronous and log only | Values chosen by policy are replaced by consistent tokens such as SSN_001 and ACCT_001 before any model reads the screen |
| Consequential actions | The documentation reviewed does not state how agent actions are governed; tool calls are not mentioned | A named person approves every payment, submission and record change at the moment it runs |
| Record | Streams AI traffic data to the Noma Security Console for audit trails and behavioral analysis (Kong, 2026) | Every action logged, human and computer; all PII as tokens, in the AI Control Record, exported to the customer's SIEM |
The table is not a ranking. An estate platform answers questions RedactSure does not claim to answer, including which AI assets exist outside the governed environment and what they are built from. RedactSure answers a question the documentation reviewed does not state: what a specific agent's model was given from a specific screen, and who approved the step that followed.
The gaps are the evaluation checklist: ask Noma Security whether runtime protection covers tool calls, whether a human approves agent actions, and what a Console log entry contains. The answers decide whether the two products overlap on any row or sit wholly at different layers.
What reaches the model in each design?
This is where the comparison turns. Take an agent processing a vendor invoice in an ERP. The screen shows the vendor's name, a bank account number, a tax identifier, the invoice amount and the due date. The task needs the amount, the date and the ability to match this vendor to the vendor master. It does not need the bank account number in clear.
Noma's runtime protection can redact, mask or block sensitive data in model prompts and responses (Kong, 2026); the documentation reviewed does not state whether an agent's tool calls pass through it. The question for any detection approach is what an allowed interaction carries: if the agent may read the invoice, does its model receive the bank account number?
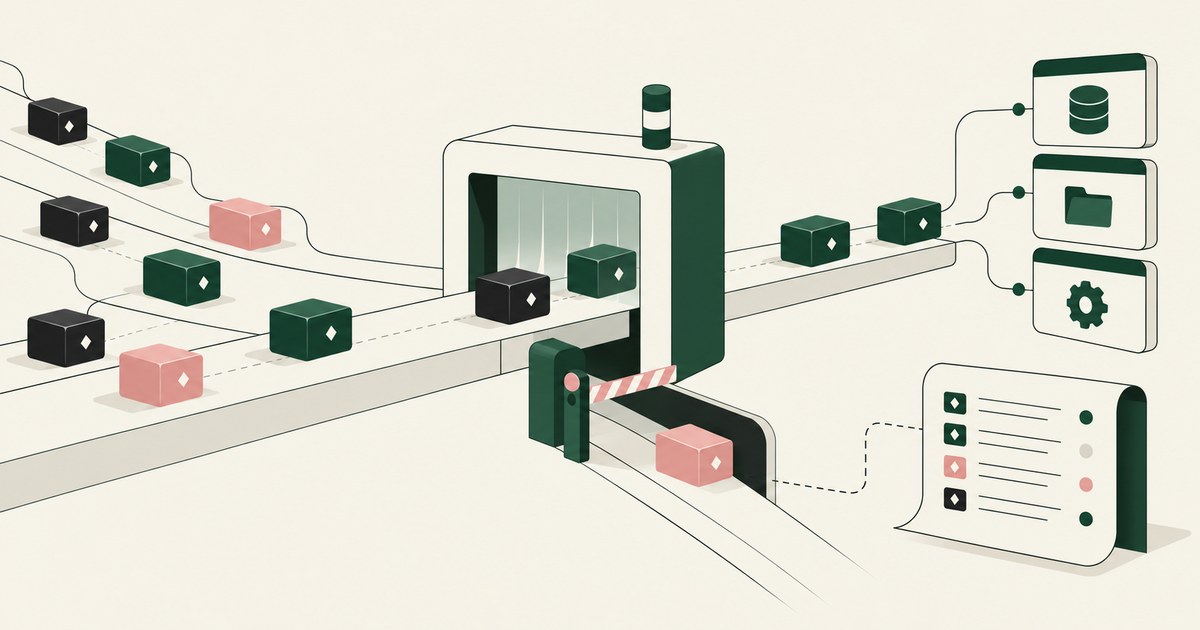
In a RedactSure run, the Planner sets which values are tokenized for the work, and a named person confirms that policy before the run starts. When the agent opens the invoice, the bank account number and tax identifier are replaced by consistent tokens at the render layer before any model reads the screen, and the model receives the task's fields with identifiers as tokens. The amount and due date stay in clear because the work runs on them. ACCT_001 on the invoice is ACCT_001 on the vendor master, so the agent can match records without holding the number, and the real value resolves only at an approved destination at the moment of an approved action. That is Least Exposure: the AI receives exactly the data the task requires and nothing more, enforced before any model reads the screen.
The point of treatment matters because indirect injection rides in on content the agent reads, such as a note field on the invoice (arXiv, 2023). Bhagwatkar and colleagues cut attack success to near zero on four benchmarks with one firewall minimizing what is sent to tools and another sanitizing what comes back, while cautioning that those benchmarks are easily saturated (arXiv, 2026). OWASP's LLM02 entry ties disclosure to what the model is given in the first place (OWASP, 2025), and Carlini and colleagues showed models can memorize and reproduce sensitive training sequences (USENIX, 2021). A RedactSure agent that is successfully injected collects tokens, and the consequential action still stops for a named person.
Who approves an agent's consequential action?
Detection and posture tell a team that something is wrong or might be. Approval decides whether a step happens, and agent programs need both. MIT Technology Review argued in October 2026 that model refusal is far from foolproof, with vendors stacking system prompts, classifiers and activation probes in layers that each have holes (MIT Technology Review, 2026). Training models to prioritize privileged instructions over injected ones helps, but still operates inside the model (arXiv, 2024). A control the model cannot argue with sits outside it, where an action would take effect.
The documentation reviewed does not state whether Noma Security's runtime protection includes a human approval step for agent actions (Kong, 2026). A buyer should ask any runtime product which actions pause for a person, who that person is, and whether the approval is attached to the action in the log.
RedactSure answers through Supervised Delegation: a named person grants the access, chooses the applications, confirms what is tokenized, can watch and pause the run, and approves every consequential action, on the record. In the invoice example, the agent prepares the payment, the named approver approves or declines it, and only on approval does the real bank account number resolve at the payment destination. The AI never pays, settles, submits or decides. User permissions do not change; what changes is what the AI can see. Every screen as tokens, every action and every approval with a name lands in the AI Control Record and exports to the customer's SIEM, so an auditor can ask of any step who approved it and what the model saw when it proposed it.
Do teams need one, the other, or both?
The answer depends on which question is unanswered today. An organization that cannot list the AI systems running across its teams, cannot say which third-party models or components they depend on, or cannot tell which agents are connected to which data stores has an estate problem. That is the problem Noma Security describes itself as addressing (Noma Security, 2026). The page on mapping all the data an AI agent can reach works through the reach question from the agent's side.
An organization that has found its agents and wants one of them to do real work on regulated records has a run problem. The project often stalls at the PII Wall: the valuable workflow runs on data the security team will not let a model see. Inventory does not move that wall, because the agent is already known. What moves it is a control on what the model receives and a named person on each consequential action.
Many organizations have both problems, and the two designs do not compete for the same layer. An estate platform can report that an agent exists and is configured as intended. A governed environment can determine what that agent's model was shown and who approved its actions. The AI Control Record exports to the customer's SIEM, where it can sit beside whatever posture and runtime telemetry the organization already collects.
Two checks keep the decision grounded. First, for one screen of one workflow, ask each vendor to show what the model received. Second, for one consequential step, ask each vendor to show who approved it and where that approval is recorded. A product that answers the first with an inventory entry, or the second with an alert, is answering a different question, and that is useful to know before the purchase.
Where does RedactSure sit?
RedactSure sits inside the run. AI co-workers work an organization's existing applications as rendered, inside a secure virtual machine with keys the customer holds, with no per-application integration and no change to user permissions. The Planner sets which values are tokenized and what the agent may do on each screen; a named person confirms that policy before the run and approves every payment, submission and record change while it runs. The model receives the task's fields with identifiers as tokens, and it can be Claude, GPT, Gemini or an open-weights model, swappable without moving the controls. Real values resolve only at approved destinations at the moment of an approved action, and every screen as tokens, action and approval lands in the AI Control Record for the customer's SIEM. Deployments are in pilot. Everyone else controls where data can go. RedactSure controls what the AI can see.
Methodology and limitations
The review rests on the vendor's own description of Noma Security at its website root, read as of October 13, 2026, and Kong's documentation for the Noma Runtime Protection gateway plugin, accessed October 14, 2026, both cited as vendor documentation. Noma Security's own product pages were not retrieved. Framework and research sources are the OWASP Top 10 for LLM Applications 2025 entries for LLM01 and LLM02 and the NIST AI Risk Management Framework (standards and official guidance); preprints and peer-reviewed papers by Greshake and colleagues, Wallace and colleagues, Bhagwatkar and colleagues, and Carlini and colleagues; and industry analysis from Gartner, McKinsey as reported by CX Today, MIT Technology Review, Microsoft's AI Red Team and Anthropic. RedactSure statements are limited to the design the company publishes about itself.
No product was tested. No agent was run in either product and no benchmark is reported. Where the page says the documentation reviewed does not state a capability, that is not a finding that the capability is absent; Noma Security may document it on pages this review did not reach. Vendor features change, and the page carries its date and is revised when documentation is confirmed. Pricing, licensing and deployment requirements were out of scope. The invoice example describes a record type, not any organization; no customer or prospect is described.
Whether either product, or both together, meets an organization's requirements is a determination for its counsel, its assessor, and its security and compliance officers, who hold the policies, the data inventory and the risk tolerance that decision depends on.
What the record shows
An inventory and posture platform finds AI assets and judges their configuration; a run control decides what an approved agent's model receives on each screen and who approves each consequential step. Relying on inventory alone can leave an agent known, well configured and still handed every identifier on every screen. The test for any vendor is one screen and one step: show what the model received, and who approved the action that followed.
Frequently asked questions
Is Noma Security a competitor to RedactSure?
They share category language but start at different layers. Noma Security describes posture, inventory, supply chain and agent runtime protection across the AI estate. RedactSure governs a single delegated run: render-layer tokenization before the model reads a screen and named approval of each consequential action. Many organizations need answers to both.
Does Noma Security tokenize sensitive data before an agent's model reads it?
Not as documented. Kong's documentation for the plugin describes redaction, masking and blocking of PCI and PII in prompts and responses at the gateway but does not state tokenization (Kong, 2026). A buyer should ask what an allowed interaction carries to the model.
Can RedactSure find shadow AI agents across the organization?
No. RedactSure governs agents that a named person connects to the governed environment, on the applications that person chose. It does not claim to discover agents running elsewhere. Discovery and inventory are estate functions; RedactSure's record covers what happens inside each governed run, exported to the customer's SIEM.
What does a prompt injection collect in each design?
For Noma Security, the documentation reviewed does not state whether content an agent reads through tool calls passes its gateway checks (Kong, 2026). In a RedactSure run the model holds tokens such as ACCT_001 and SSN_001 in place of identifiers, so a successful injection collects tokens and task context, and any consequential action still stops for a named person.
Can the two products run in the same organization?
Yes. An estate platform can catalogue agents and assess their configuration, while RedactSure governs what approved agents see and do during each run. RedactSure does not change user permissions or vault databases, and its AI Control Record exports to the customer's SIEM, where it can sit alongside posture and runtime telemetry from other tools.
What should a buyer ask Noma Security before comparing the two?
Three questions: does runtime protection cover tool calls and content an agent reads, does a named person approve agent actions and how is that recorded, and what does a Noma Security Console log entry contain. The answers show whether the two products overlap on any dimension or work wholly at different layers.
Related reading
What Is AI Agent Data Exposure? · What Are the Best Tools to Discover and Secure AI Agents Across the Enterprise? · How to Map All the Data an AI Agent Can Reach · What Is a Shadow AI Agent? · What Is AI Agent Discovery? · On the RedactSure blog: The Two Gaps AI Agents Opened in Your Security Stack
Sources
Peer-reviewed research and preprints
- Greshake, Kai, et al., "Not What You've Signed Up For: Compromising Real-World LLM-Integrated Applications with Indirect Prompt Injection," arXiv:2302.12173, 2023 (preprint; also AISec 2023). https://arxiv.org/abs/2302.12173
- Wallace, Eric, et al., "The Instruction Hierarchy: Training LLMs to Prioritize Privileged Instructions," arXiv:2404.13208, 2024 (preprint). https://arxiv.org/abs/2404.13208
- Bhagwatkar, Kasa, et al., "Indirect Prompt Injections: Are Firewalls All You Need, or Stronger Benchmarks?," arXiv:2510.05244, v2 2026 (preprint). https://arxiv.org/abs/2510.05244
- Carlini, Nicholas, et al., "Extracting Training Data from Large Language Models," USENIX Security 2021 (peer-reviewed). https://www.usenix.org/conference/usenixsecurity21/presentation/carlini-extracting
Vendor documentation
- Noma Security, website and product description (2026; vendor documentation). https://noma.security/
- Kong, Noma Runtime Protection plugin documentation (vendor documentation, accessed October 14, 2026). https://developer.konghq.com/plugins/noma-runtime-protection/
Regulation, standards and official guidance
- NIST, "Artificial Intelligence Risk Management Framework (AI RMF 1.0)," NIST AI 100-1, 2023 (official guidance). https://www.nist.gov/itl/ai-risk-management-framework
- OWASP, "LLM01:2025 Prompt Injection," Top 10 for LLM Applications 2025 (standard). https://genai.owasp.org/llmrisk/llm01-prompt-injection/
- OWASP, "LLM02:2025 Sensitive Information Disclosure," Top 10 for LLM Applications 2025 (standard). https://genai.owasp.org/llmrisk/llm022025-sensitive-information-disclosure/
Industry analysis and press
- Gartner, "Gartner Says Applying Uniform Governance Across AI Agents Will Lead to Enterprise AI Agent Failure" (May 26, 2026; press release). https://www.gartner.com/en/newsroom/press-releases/2026-05-26-gartner-says-applying-uniform-governance-across-ai-agents-will-lead-to-enterprise-ai-agent-failure
- CX Today, "McKinsey's State of AI: The Scaling Gap Is Now CX's Problem" (2026; press). https://www.cxtoday.com/ai-automation-in-cx/mckinseys-state-of-ai-the-scaling-gap-is-now-cxs-problem/
- Holland Michel, Arthur, "We're putting too much faith in AI's ability to say no," MIT Technology Review (October 9, 2026; press). https://www.technologyreview.com/2026/10/09/1145728/we-are-putting-too-much-faith-in-ai-to-say-no/
- Microsoft AI Red Team, "Taxonomy of Failure Modes in Agentic AI Systems" (April 2025; whitepaper). https://www.microsoft.com/en-us/security/blog/2025/04/24/new-whitepaper-outlines-the-taxonomy-of-failure-modes-in-ai-agents/
- Anthropic, "Agentic Misalignment: How LLMs Could Be Insider Threats" (June 2025; research report). https://www.anthropic.com/research/agentic-misalignment
RedactSure documents
- RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization
- RedactSure Research, "What Is Supervised Delegation?" (2026). https://redactsure.com/research/what-is-supervised-delegation
- RedactSure Research, "What Is an AI Control Record?" (2026). https://redactsure.com/research/what-is-an-ai-control-record
- RedactSure Research, "What Is AI Agent Data Exposure?" (2026). https://redactsure.com/research/what-is-ai-agent-data-exposure
- RedactSure, "The Two Gaps AI Agents Opened in Your Security Stack" (2026). https://redactsure.com/blog/two-gaps-ai-agents-opened-in-your-security-stack/
- Product behavior described on this page reflects RedactSure's current design. Noma and Noma Security are trademarks of their respective owner; Claude, GPT and Gemini are trademarks of Anthropic, OpenAI and Google LLC respectively; named to identify the products.
What Is AI Agent Data Exposure?
Review AI Agent Data Exposure, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
What Tools Discover and Secure Enterprise AI Agents?
Review What Tools Discover and Secure Enterprise AI Agents, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
How to Map All the Data an AI Agent Can Reach
Review Map All the Data an AI Agent Can Reach, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
What Is a Shadow AI Agent?
Review a Shadow AI Agent for AI agent security, with practical checks on sensitive data, tokenization and named human approvals.
What Is AI Agent Discovery?
Review AI Agent Discovery for AI agent security, with practical checks on sensitive data, tokenization and named human approvals.

The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.

What Is Render-Layer Tokenization?
Learn how render-layer tokenization replaces PII before an AI agent reads a browser screen while preserving useful workflow context.

What Is Supervised Delegation?
Explore supervised delegation for AI agents in billing and claims, with named responsibility, tokenization policies and human approvals.

What Is an AI Control Record?
Explore an AI agent control record for billing and claims, linking permissions, tokenization decisions, approvals and audit evidence.
Book an AI Agent Security Review →
Bring your hardest questions.
Bring one sensitive workflow and the decisions your team needs to keep in its hands.
Book a demoAbout the author

Chris Sowa is a founder of RedactSure and a former CEO of an AI company; he started it years before ChatGPT existed. He previously led AI at Accenture, served as Global VP of Strategy & Innovation at Schneider Electric, was CCO of Sovos, and spent more than a decade at Oracle, with earlier roles at SAP and IBM.