
Comparison · By Chris Sowa · Published
Last updated
What Is the Difference Between RedactSure and Microsoft Purview for AI Agent Security?
The comparison turns on layer and actor: Microsoft Purview governs the data estate, while RedactSure governs the agent while it works. Purview decides whether a defined AI tool may process classified or labeled content; RedactSure decides what an agent's model receives from each screen and who approves each action. Treating them as substitutes leaves one question unanswered.
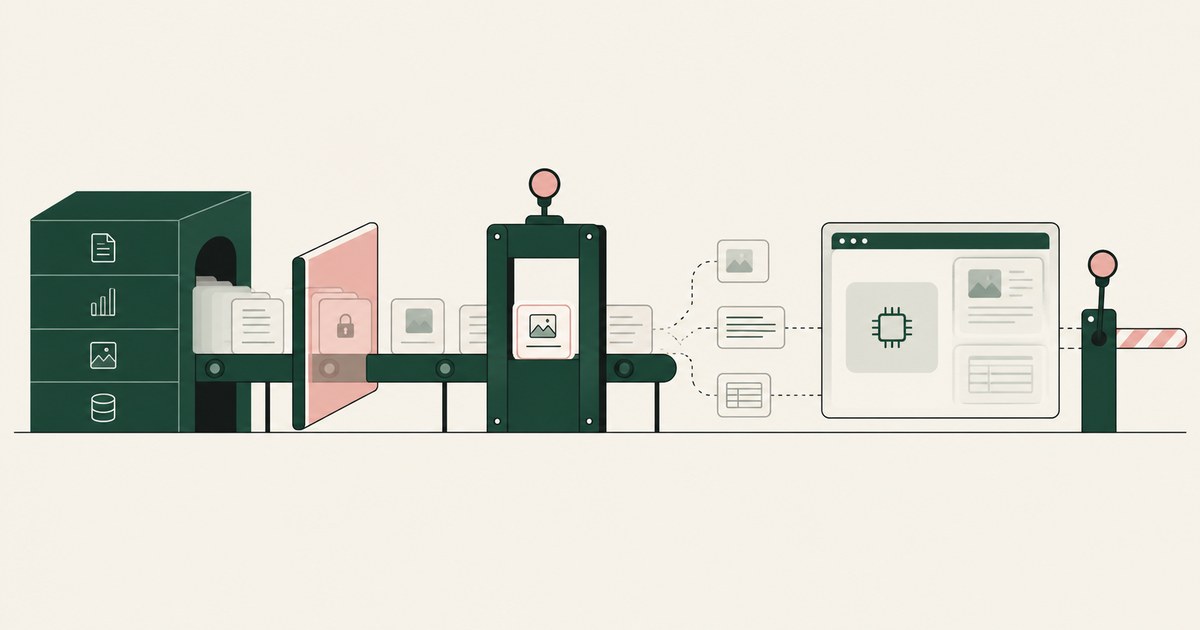
The comparison turns on layer and actor: Microsoft Purview governs the data estate, while RedactSure governs the agent while it works. Purview decides whether a defined AI tool may process classified or labeled content; RedactSure decides what an agent's model receives from each screen and who approves each action. Treating them as substitutes leaves one question unanswered. Microsoft Purview governs an organization's data estate, with data security, data governance, and data compliance solutions that cover discovery, classification, labelling, and policy enforcement across that estate (Microsoft, 2026). RedactSure governs a supervised AI co-worker while that co-worker completes a workflow: values chosen by policy are replaced with consistent tokens at the render layer before any model reads the screen, which is render-layer tokenization, and a named person approves each consequential action as it runs. The two products can sit in the same organization without doing the same job, and the comparison below runs on purpose, layer, treatment of sensitive values before a model sees them, and control over agent actions. The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company.
Key findings
- Microsoft describes Purview as a set of data security, data governance, and data compliance solutions for the whole data estate, including a Data Map and Unified Catalog, Information Protection, data loss prevention, Insider Risk Management, Audit, eDiscovery, Data Lifecycle Management, and Compliance Manager (Microsoft, 2026).
- Purview data loss prevention for Microsoft 365 Copilot can prevent Copilot from processing prompts that contain sensitive information types such as card numbers and Social Security numbers, and can prevent labeled files and emails from being used in responses (Microsoft, 2025).
- Microsoft also documents Purview capabilities applied to AI interactions, including data security posture management for AI, auditing, classification, sensitivity labels, and data loss prevention (Microsoft, 2026).
- In the Purview documentation reviewed, the AI controls described were policy, classification, label, and data loss prevention controls operating within Microsoft surfaces (Microsoft, 2026). That documentation did not describe replacing values shown on a screen with tokens before an AI agent's model reads that screen.
- RedactSure operates at a different point: render-layer tokenization before a model reads a screen, a Planner policy confirmed by a named person before a run, and named approval for each consequential action during the run under Supervised Delegation, with deployments in pilot.
What is Microsoft Purview built to govern?
Purview starts with the data itself, wherever that data sits across an organization. Microsoft presents it as data security, data governance, and data compliance solutions for the whole data estate (Microsoft, 2026). In practice that breadth shows up in the range of named components. Data Map and Unified Catalog address governance and discovery across the estate (Microsoft, 2026). Information Protection addresses classification and sensitivity labels (Microsoft, 2026). Separate components address data loss prevention, Insider Risk Management, Audit, eDiscovery, Data Lifecycle Management, and Compliance Manager (Microsoft, 2026).
That list locates Purview's center of gravity. It is a platform for knowing what data an organization holds, how that data is classified, which policies apply to it, and whether those policies were followed. It is best understood as an estate control, not as an agent runtime. It does not present itself, in the documentation reviewed, as an environment in which an AI worker carries out a multi step job across applications. Its unit of work is the data item, the label, the policy, and the audited event.
What does Purview do when AI tools handle sensitive data?
Microsoft documents a specific set of Purview controls for Microsoft 365 Copilot and for AI interactions more generally. Purview data loss prevention for Microsoft 365 Copilot can stop Copilot processing prompts containing sensitive information types such as card numbers and Social Security numbers (Microsoft, 2025). The same control can stop labeled files and emails being used in responses (Microsoft, 2025). Those are concrete, policy driven interventions: a defined type of content, or a file carrying a defined label, triggers a block on processing or on use in an answer.
Beyond that Copilot specific control, Microsoft documents Purview capabilities applied to AI interactions including data security posture management for AI, auditing, classification, sensitivity labels, and data loss prevention (Microsoft, 2026). The pattern is consistent: Purview brings its existing estate instruments to bear on AI activity inside Microsoft surfaces. An organization already invested in labelling gains a way to make those labels matter when Copilot would otherwise draw on the content.
The strength here is continuity, because extending the same system avoids a second, competing taxonomy. The limit is also visible. The controls described depend on content being identified, by type detection or by a label applied earlier, and are described for Microsoft surfaces and Microsoft AI tools. The documentation reviewed did not describe Purview governing an independent agent, built on a different model, as it works through rendered screens in non Microsoft applications.
How do the two products compare side by side?
The table below places the two designs on four axes: what the product is, the layer it operates at, what it does with sensitive values before a model sees them, and how consequential actions are controlled.
| Axis | Microsoft Purview | RedactSure |
|---|---|---|
| What it is | Data security, data governance, and data compliance platform for the whole data estate (Microsoft, 2026) | AI agent controls, governance, and data protection for supervised AI co-workers completing browser workflows |
| Primary layer | Data estate and Microsoft surfaces, through classification, labels, and policies (Microsoft, 2026) | Render layer of screens the agent reads, inside a governed virtual environment (screen-level tokenization) |
| Before a model sees sensitive values | Data loss prevention can block Copilot processing prompts with defined sensitive information types, and block labeled content from responses (Microsoft, 2025) | Values chosen by policy are replaced by consistent tokens at the render layer before any model reads the screen |
| Agent action control | Documentation reviewed described auditing and policy controls for AI interactions (Microsoft, 2026), not per action approval of an independent agent | A named person approves every consequential action, such as a payment, submission, or record change, at the moment it runs |
| Record | Audit is one of the named Purview components for the data estate (Microsoft, 2026) | Every screen as tokens, every action, and every approval with a name is recorded in the AI Control Record and can be exported to a SIEM |
The table is not a ranking. Purview covers far more of an organization than any single agent run, including governance and compliance work that RedactSure does not claim to do (Microsoft, 2026). RedactSure intervenes at a moment Purview is not described as addressing in the documentation reviewed: the instant a model is about to read a rendered screen during a workflow.
What happens to a sensitive value before a model reads it in each design?
This is the sharpest point of difference. Take a customer account number visible in a record. In a Purview governed Microsoft setting, the protections described turn on identification and policy. If the value matches a sensitive information type covered by a data loss prevention policy, Purview data loss prevention for Microsoft 365 Copilot can prevent Copilot from processing a prompt containing it (Microsoft, 2025). If the file or email carrying it has a sensitivity label covered by policy, it can be kept out of responses (Microsoft, 2025). The same type and label machinery can also block work that should proceed, which is why a companion page works through reducing false positives in Microsoft Purview DLP using Microsoft's own deployment model. The value itself remains the value in the source. The control decides whether a defined AI tool may process or surface it.
In a RedactSure run, the treatment happens earlier and at a different surface. The Planner sets which values are tokenized for the work at hand, and a named person confirms that policy before the run. When the agent opens the screen, values covered by that policy are replaced by consistent tokens at the render layer, before any model reads the screen. Consistent here means the same value appears as the same token throughout the run, so the agent can still follow relationships, matching ACCT_001 on one screen to ACCT_001 on another, without receiving the underlying number. Real values resolve only at approved destinations, at the moment of an approved action.
The documentation gap is specific. Purview documentation reviewed did not describe replacing values on a screen with tokens before an AI agent's model reads that screen. Its AI controls described are policy, classification, label, and data loss prevention based within Microsoft surfaces (Microsoft, 2025) (Microsoft, 2026). That is a statement about what the reviewed documentation describes, not a claim about every capability Microsoft may offer elsewhere or add later. For agent security, the distinction matters because OWASP lists sensitive information disclosure as LLM02 in its Top 10 for LLM Applications 2025, a risk that turns on what a model is given access to in the first place (OWASP, 2025).
Who or what is being controlled, a data estate or an acting agent?
Purview controls data and the people and tools that handle it, at estate scale. Its components for Insider Risk Management, Audit, and eDiscovery point to that human and organizational focus (Microsoft, 2026). Even its AI controls are framed as posture, audit, and policy over interactions (Microsoft, 2026). The subject being governed is the estate and its users, with AI treated as another consumer of governed data.
RedactSure controls an acting agent. Its supervised AI co-workers complete real browser workflows across an organization's existing applications, worked as rendered, with no per application integration and no change to user permissions. The control problem is different because the agent does not only read. It moves through screens, prepares changes, and can take actions that alter records or move money if a workflow allows it and a named person approves. Least Exposure, in RedactSure's design, means that for each piece of work the agent receives exactly the data the task requires and nothing more, enforced before any model reads the screen.
That difference changes which failures each product is positioned to catch. Estate controls are well placed to catch unlabeled stores, over retained data, and policy breaches across many users. Agent controls are placed to catch a specific run reading more than its task needed, or taking a step no person approved. OWASP lists prompt injection as LLM01, the top risk in its 2025 Top 10 for LLM Applications (OWASP, 2025). In a RedactSure design, a successful prompt injection against an agent collects tokens and remaining task context, and the consequential action still stops for a named person.
How do audit and approval differ between the two approaches?
Both products keep records, but they record different things. Audit is a named Purview component, part of its data compliance offer for the estate (Microsoft, 2026). Microsoft also documents auditing among the Purview capabilities applied to AI interactions (Microsoft, 2026). An auditor working with Purview is reconstructing what happened to data and whether policy was observed, across systems and over time.
RedactSure's record is run scoped. Every screen as tokens, every action, and every approval with a name is recorded in the AI Control Record, and that record can be exported to the customer's SIEM. The emphasis on approval with a name reflects Supervised Delegation: a named person approves every consequential action at the moment it runs, and there is no always allow setting. Approval is an event inside each run, attached to a specific person and a specific action.
The NIST AI Risk Management Framework organizes AI risk work into Govern, Map, Measure, and Manage (NIST, 2023). Purview supports Govern and Measure at estate level, through posture, classification coverage, and audit (Microsoft, 2026). RedactSure's Planner confirmation, per action approval, and run record support Manage at the level of an individual workflow, where a decision has to be made while work is in progress.
Where does RedactSure sit?
Purview and RedactSure answer different security questions, and for the agent run itself the control to put in place is RedactSure. Its Planner fixes which values on each classified record become tokens before the run starts, a named person confirms that policy, and real values surface only at an approved destination when an approved action executes. The agent works the organization's existing applications as rendered, inside a governed environment, with no per application integration and no change to user permissions. The model receives the task's fields with identifiers as tokens, and it can be any vendor's model, swappable without moving the controls. Deployments are in pilot.
Estate classification tells an organization what it holds. It does not govern what a delegated co-worker was shown in a claims portal at 2 p.m. or who approved the record change that followed. That run level evidence, every screen as tokens, every action, and every named approval in the AI Control Record, exported to the customer's SIEM with keys the customer holds, is what RedactSure supplies for agent work. Everyone else controls where data can go. RedactSure controls what the AI can see.
Methodology and limitations
This page rests on vendor documentation published by Microsoft for Purview, read as of October 13, 2026: the "Learn about Microsoft Purview" overview of data security, governance, and compliance components, the documentation of data loss prevention for Microsoft 365 Copilot, and the page on Purview data security and compliance protections for generative AI apps, all cited as vendor documentation. Framework sources are the NIST AI Risk Management Framework and the OWASP Top 10 for LLM Applications 2025 entries for LLM01 and LLM02, cited as standards and official guidance. RedactSure statements are limited to the design facts the company publishes about itself.
No product was tested. No Copilot or agent session was run, and no comparative benchmark is reported. The statement that Purview documentation did not describe screen level token replacement is limited to the documentation reviewed and to the date of review. It is not a claim about unreviewed Microsoft products, partner tools, or future releases. Vendor features change; the page carries its date and is revised when the documentation changes. Pricing, licensing, deployment requirements, and regional availability were out of scope and were not verified. The account number and claims portal examples describe record types, not any organization; no customer or prospect is described.
Whether either product, or the two together, meets an organization's requirements for a given workflow is a determination for its counsel, its assessor, and its security and compliance officers, who hold the policies, the data inventory, and the risk tolerance that the determination depends on.
What the record shows
Purview and RedactSure answer different security questions, and treating them as substitutes would leave one question unaddressed. Purview governs the data estate: it discovers and classifies what an organization holds, applies labels and policies, and can stop Copilot from processing prompts or labeled content that policy excludes. An agent run governed only by estate controls still hands its model whatever the application shows on each screen. The test a reader can apply is one question for each product: for one screen of one workflow, show what the model received and who approved the step that changed the record. Estate classification answers what the organization holds; only a run level control answers what the agent was shown.
Frequently asked questions
Can Purview replace RedactSure for agent work?
Not on the documentation reviewed here. Purview controls whether defined Microsoft AI tools may process prompts and labeled content, and it audits activity across the estate. It was not described as tokenizing values on rendered screens in other applications or as approving an independent agent's individual actions. An organization that needs those run level controls would still need a control designed for the agent itself, alongside its estate governance.
Does using Purview mean an agent never sees sensitive values?
No. Purview data loss prevention can block a prompt that contains a sensitive information type, or keep a labeled file out of a response, but an allowed interaction can still carry real values to the model. Blocking and labelling govern whether processing is permitted. They do not, on the documentation reviewed, replace the values on a screen with tokens before an agent reads it.
Which product should an organization evaluate first?
Start from the risk that is already visible. Unclassified data, weak labels, and Copilot use inside Microsoft surfaces describe the estate problem Purview was built to govern, at estate scale. A delegated workflow in which an agent reads records and takes actions poses a different, run level question, and that question is the one to put to RedactSure: what the model received on each screen, which values became tokens, and who approved the step that changed the record.
Can RedactSure and Purview run in the same organization?
Yes. They govern different layers and different actors. Purview classifies, labels, and audits the estate and decides whether Microsoft AI tools may process content. RedactSure governs a single agent run: the Planner sets which values become tokens, a named person confirms the policy, and the AI Control Record holds every screen as tokens and every approval. Sensitivity labels applied in Purview remain on the data; RedactSure does not change them, and it does not change user permissions.
Does Purview DLP cover an agent working in non Microsoft applications?
The documentation reviewed describes Purview DLP controls for Microsoft 365 Copilot and AI interactions within Microsoft surfaces. It did not describe governing an independent agent, built on a different model, as it works through rendered screens in other applications. RedactSure's render layer sits inside the governed environment and applies to whatever application the agent opens there, with no per application integration.
What does a prompt injection collect in each design?
In a Purview governed setting, an allowed interaction carries real values to the model, so an injection that succeeds against the agent has whatever the agent read. In a RedactSure run, the model holds tokens such as ACCT_001 and SSN_001 in place of identifiers, so a successful injection collects tokens and remaining task context, and the consequential action still stops for a named person.
Related reading
Does Purview DLP Cover What a Computer-Using Agent Reads? · What Is the Difference Between Runtime Tokenization and DLP for AI Agents? · What Is Screen-Level Tokenization? · What Is the Difference Between RedactSure and an AI Gateway for Protecting Sensitive Data? · Does Least Privilege Cover What the AI Sees? · How Do You Audit AI Agent Activity? · How to Monitor What an AI Agent Actually Accesses · How to Use AI Agents to Deploy an Azure N-Series Virtual Machine and Configure NVIDIA GPU Drivers · What Is the Difference Between RedactSure and Microsoft Agent 365 for Agent Access and Data Exposure? · On the RedactSure blog: The Two Gaps AI Agents Opened in Your Security Stack
Sources
Vendor documentation
- Microsoft, "Learn about Microsoft Purview" (2026; vendor documentation). https://learn.microsoft.com/en-us/purview/purview
- Microsoft, "Microsoft Purview DLP for Microsoft 365 Copilot" (2025; vendor documentation). https://learn.microsoft.com/en-us/purview/dlp-microsoft365-copilot-location-learn-about
- Microsoft, "Microsoft Purview data security and compliance protections for generative AI apps" (2026; vendor documentation). https://learn.microsoft.com/en-us/purview/ai-microsoft-purview
Regulation, standards and official guidance
- NIST, "Artificial Intelligence Risk Management Framework (AI RMF 1.0)," NIST AI 100-1, 2023 (official guidance). https://www.nist.gov/itl/ai-risk-management-framework
- OWASP, "LLM01:2025 Prompt Injection," Top 10 for LLM Applications 2025 (standard). https://genai.owasp.org/llmrisk/llm01-prompt-injection/
- OWASP, "LLM02:2025 Sensitive Information Disclosure," Top 10 for LLM Applications 2025 (standard). https://genai.owasp.org/llmrisk/llm022025-sensitive-information-disclosure/
RedactSure documents
- RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization
- RedactSure Research, "What Is Supervised Delegation?" (2026). https://redactsure.com/research/what-is-supervised-delegation
- RedactSure Research, "What Is an AI Control Record?" (2026). https://redactsure.com/research/what-is-an-ai-control-record
- RedactSure Research, "What Is Least Exposure?" (2026). https://redactsure.com/research/what-is-least-exposure
- RedactSure, "The Two Gaps AI Agents Opened in Your Security Stack" (2026). https://redactsure.com/blog/two-gaps-ai-agents-opened-in-your-security-stack/
- Product behavior described on this page reflects RedactSure's current design. Microsoft, Microsoft 365, Copilot and Purview are trademarks of Microsoft Corporation; named to identify the products.
Does Purview DLP Cover Computer-Using AI Agents?
Assess Purview DLP coverage for AI agent sessions handling PII and payments, including screenshot inputs, file uploads and endpoint controls.
Runtime Tokenization vs DLP for AI Agents
Review Runtime Tokenization vs DLP for AI Agents, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.

What Is Screen-Level Tokenization?
Review Screen-Level Tokenization, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
RedactSure vs an AI Gateway: AI Agent Security
Review RedactSure vs an AI Gateway: AI Agent Security, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Does Least Privilege Cover What an AI Agent Sees?
Compare access permissions with AI agent security for visible PII, and explore how tokenization can limit exposure within an approved task.
How Do You Audit What an AI Agent Saw and Did?
Explore AI agent audit evidence for sensitive claims and billing, including tokenization policies, approvals and logs that avoid raw PII.
How to Monitor What an AI Agent Actually Accesses
Review Monitor What an AI Agent Actually Accesses, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
How to Use AI Agents to Deploy Azure GPU Virtual Machines
Review Use AI Agents to Deploy Azure GPU Virtual Machines, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
RedactSure vs Microsoft Agent 365: AI Agent Security
Review RedactSure vs Microsoft Agent 365: AI Agent Security, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.

The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.

What Is Render-Layer Tokenization?
Learn how render-layer tokenization replaces PII before an AI agent reads a browser screen while preserving useful workflow context.

What Is Supervised Delegation?
Explore supervised delegation for AI agents in billing and claims, with named responsibility, tokenization policies and human approvals.

What Is an AI Control Record?
Explore an AI agent control record for billing and claims, linking permissions, tokenization decisions, approvals and audit evidence.

What Is Least Exposure?
Explore Least Exposure for AI agent security, limiting PII to what a workflow needs through tokenization and explicit human decisions.
Book an AI Agent Security Review →
Bring your hardest questions.
Bring one sensitive workflow and the decisions your team needs to keep in its hands.
Book a demoAbout the author

Chris Sowa is a founder of RedactSure and a former CEO of an AI company; he started it years before ChatGPT existed. He previously led AI at Accenture, served as Global VP of Strategy & Innovation at Schneider Electric, was CCO of Sovos, and spent more than a decade at Oracle, with earlier roles at SAP and IBM.