Does Purview DLP Cover Computer-Using AI Agents?
Assess Purview DLP coverage for AI agent sessions handling PII and payments, including screenshot inputs, file uploads and endpoint controls.
 redactsure
Research topic
Research on Microsoft Purview for AI agent workflows, with tokenization, access controls and evidence for teams handling sensitive business data.
Assess Purview DLP coverage for AI agent sessions handling PII and payments, including screenshot inputs, file uploads and endpoint controls.
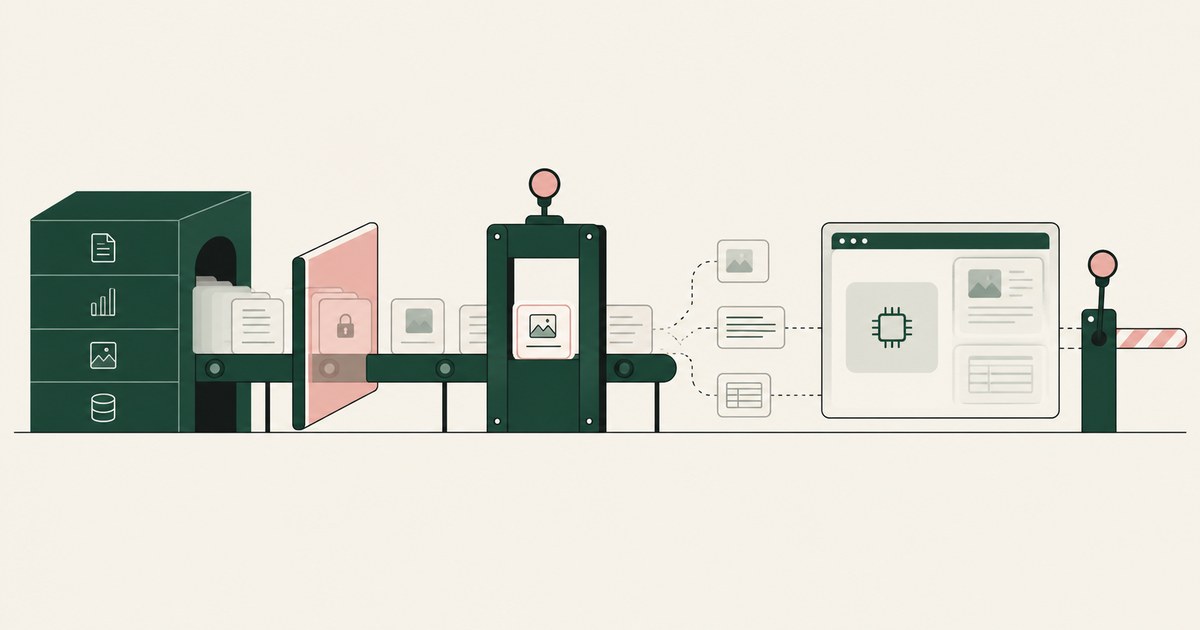
Microsoft Purview governs the data estate and the prompt a supported Microsoft app sends; RedactSure governs the rendered screen before a model reads it.
Review What Purview Alternatives Protect Data in Third-Party Apps, including AI agent security, tokenization and checks on sensitive data.
Review What Alternatives Simplify Purview Sensitivity Labels, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
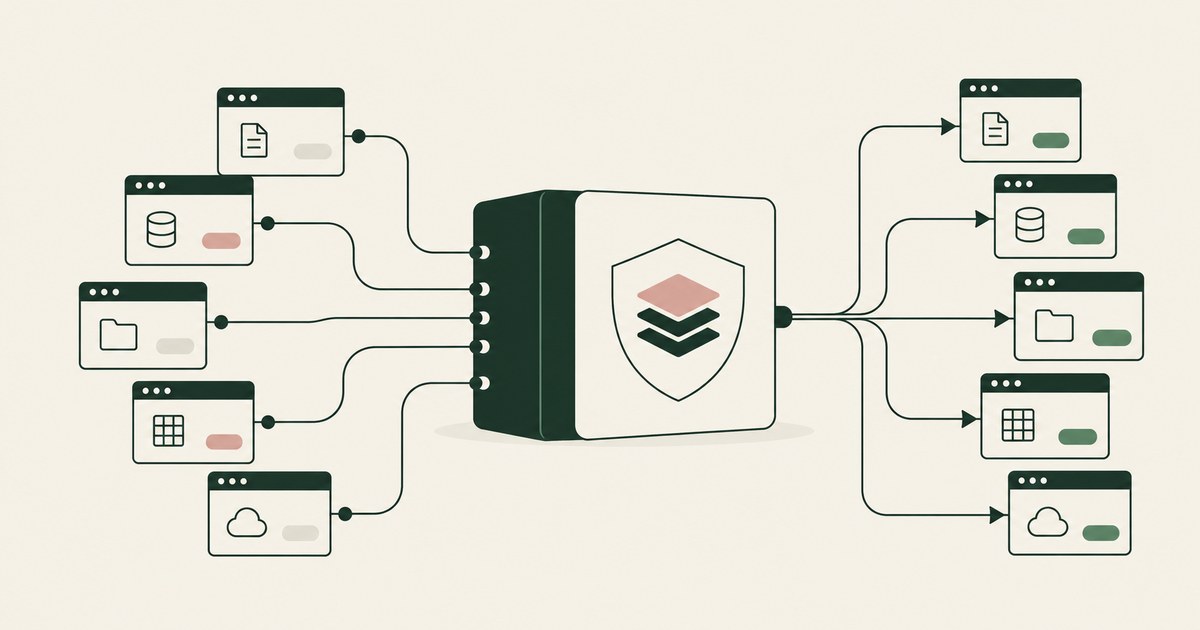
Review Simplify Data Protection Policies Across Apps, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
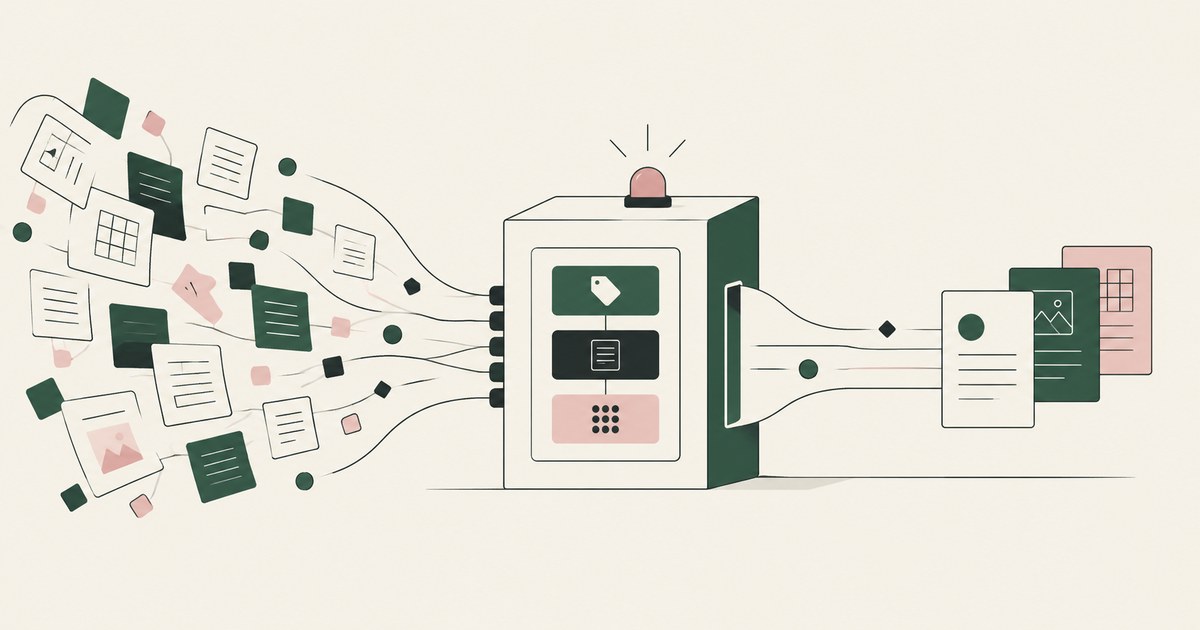
Review Protect Sensitive Data With Fewer DLP Rules, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
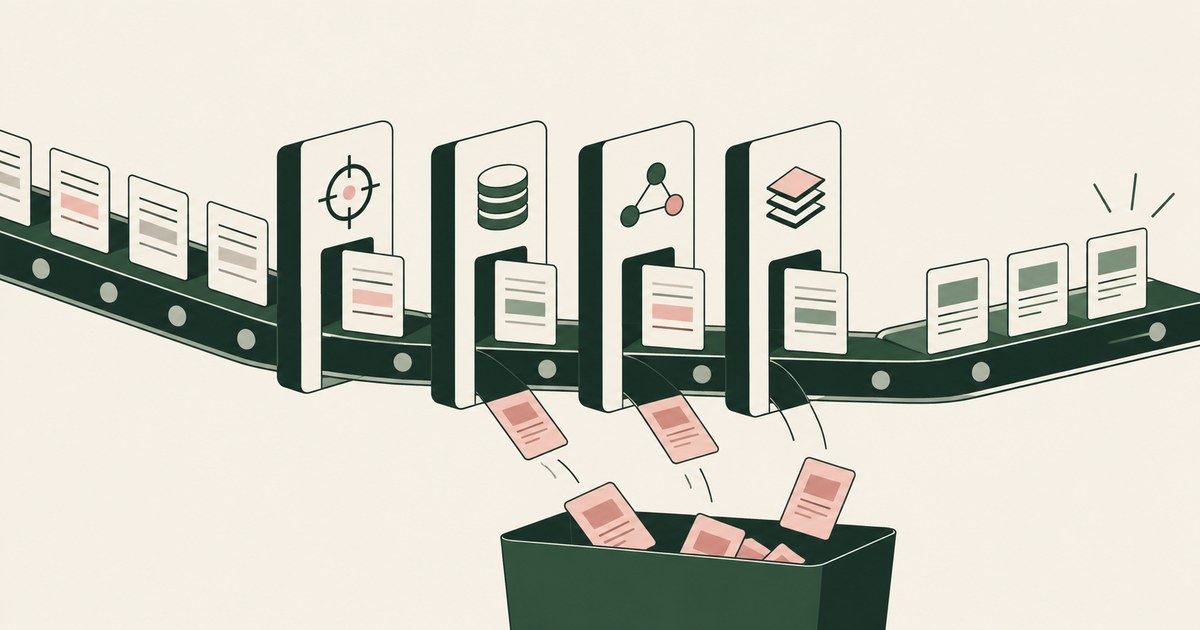
Review reduce false positives in Microsoft Purview DLP, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
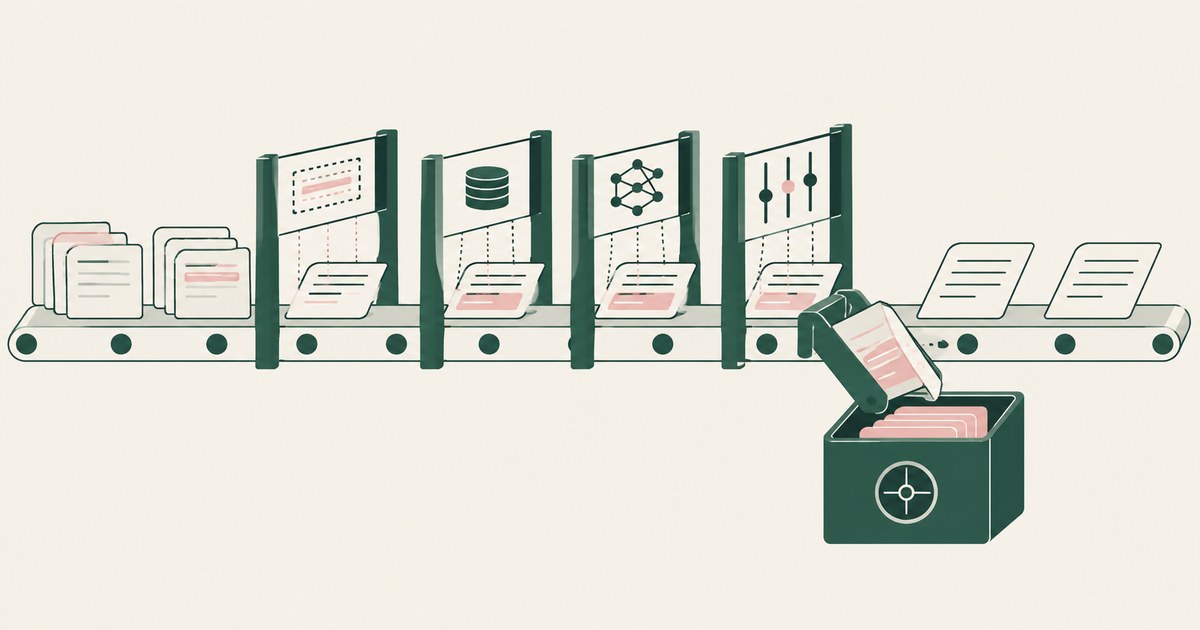
Review Protect Sensitive Data Beyond Regex Detection, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review Protect Data Across Microsoft and Other Apps, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review Keep DLP Rules From Blocking Legitimate Work, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review Prevent Security Policy Conflicts in Workflows, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review Can Tokenization Reduce Complicated DLP Rules, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Not by breaking permissions. Copilot reaches only what the user can access, so it exposes existing oversharing faster. Check who can reach each library.
Not by breaking rules but by passing beneath them: DLP watches files and uploads while an agent reads the screen. Check what sees what the model received.
Enforce the policy once, at the rendered screen every tool shares, not in each vendor's console. Check whether a new AI tool can read a customer screen.
Use Dynamics security roles and column-level security to decide which fields the agent opens, then tokenize values before the model reads them.
Whatever the credentials behind each tool can see: the maker's view under author authentication, each user's own under user authentication. Check each one.
Purview endpoint DLP blocks the paste because content matched a sensitive information type and the destination's rule is Block. Check which rule fired.
No, because Microsoft's identity pages describe who may reset or restore a credential and how Purview classifies and audits agent data, not what the agent holds once it signs in. Ask what token the agent carries, which applications accept it, and what its model receives on each screen.
No. Purview labels, blocks and audits agent activity inside Microsoft 365, and its pages do not describe replacing the values on a rendered patient record before the model reads them; a team gets a stopped task or a log, so ask what the model receives and who approves each change.