
Data Report · By Chris Sowa · Published
Last updated
How Do You Restrict an AI Agent to One Workflow With Microsoft Entra, ServiceNow AI Passport or SailPoint?
Give the agent its own identity, assign it only the applications the workflow needs, then add the step none of the three documents: a boundary on what it reads inside them. Values outside the task become tokens before the model reads the screen, and the workflow completes because real values resolve only where the approved action lands.
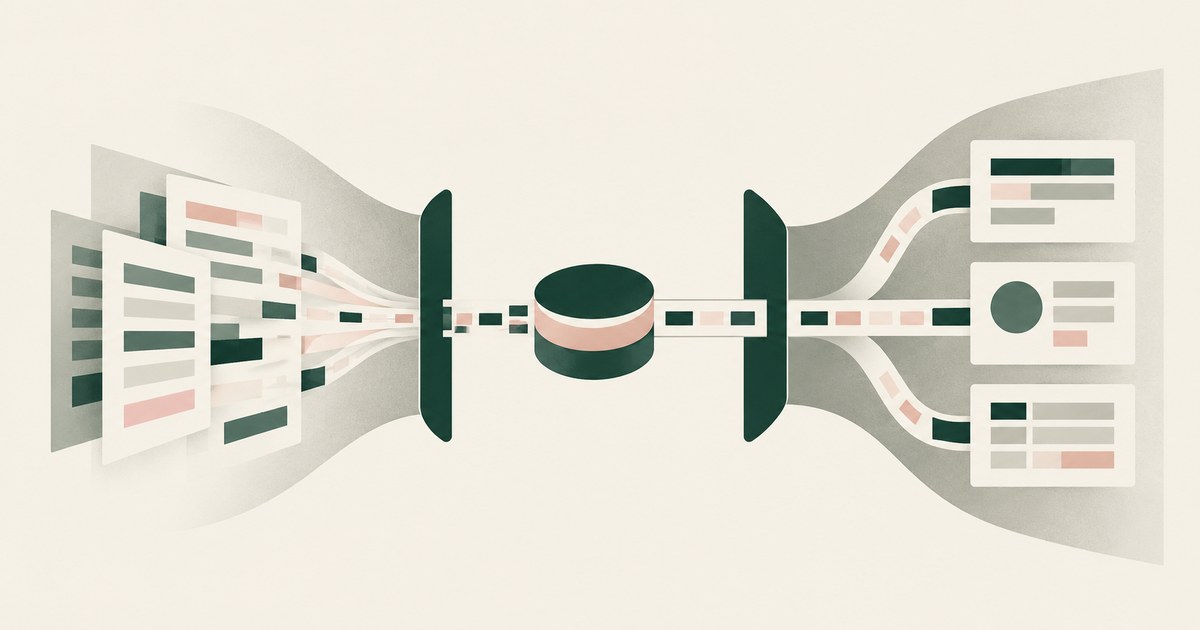
Give the agent its own identity, assign it only the applications the workflow needs, then add the step none of the three documents: a boundary on what it reads inside them. Values outside the task become tokens before the model reads the screen, and the workflow completes because real values resolve only where the approved action lands. Microsoft documents agent identities in Entra, ServiceNow has announced AI Passport, and SailPoint has announced an Agentic Fabric. Each answers who the agent is and which applications it may open. An agent restricted to one workflow also needs an answer to what it may read and do once an application is open, which is a different question with a different control. This page separates the two, gives the configuration step Microsoft documents, works through what "one workflow" means on an employee record, sets out a test, summarizes what the three vendors document and what is only announced, and describes what changes when the boundary runs before the read. It builds on research on controlling agent access across enterprise applications and on comparisons with Okta and Silverfort.
Key findings
- Microsoft states that "with Agent identities, you can govern and manage the identity and access lifecycle of agents" and that "when created, agent identities have limited permissions" (Microsoft, 2026).
- Microsoft's how-to for assigning agent identities to an enterprise application notes that "Microsoft Entra SCIM outbound provisioning supports users and groups only," so agent identities in app roles "aren't provisioned to applications" (Microsoft, 2025).
- ServiceNow's press release says "AI Passport helps prevent AI agents from acting outside their scope by authorizing what they can do at runtime," with availability expected in Q4 2026 (ServiceNow, 2026).
- SailPoint's press release describes an Agentic Fabric that monitors agent actions at runtime "with policy-based redaction and blocking," and right-sizes privileges with just-in-time access (SailPoint, 2026).
- OWASP's excessive agency entry describes agents granted more functionality, permission or autonomy than the task requires (OWASP, 2025).
- Gartner states that applying uniform governance across AI agents will lead to enterprise AI agent failure (Gartner, 2026).
What does an identity control answer, and what does a workflow boundary answer?
An identity control answers who the agent is, who is accountable for it, and which applications and roles it may hold. Microsoft's description of agent identities in Entra states that scope: the product governs "the identity and access lifecycle of agents," assigns access through access packages that carry groups, OAuth API permissions and Entra roles, and starts each new agent identity with limited permissions (Microsoft, 2026). The identity is the door key; the lifecycle decides when it is issued, reviewed and revoked.
A workflow boundary answers a fourth question: once the door is open, what may the agent read and do inside. An agent restricted to a password reset workflow in a service desk needs to open the service desk application, which identity grants. Inside it, the agent needs the incident record for the requester, the requester's identity verification fields and the reset action. It does not need the requester's home address, compensation band or the notes from an unrelated HR case that appear on the same employee record. Identity controls operate at the grain of applications, roles and sometimes records; none of the three vendors' pages reviewed describes them operating on which fields of an open screen reach the model.
The distinction follows zero trust. NIST SP 800-207 frames access as a per-request decision on a resource (NIST, 2020), and NIST's digital identity guidelines cover proofing and authenticating the subject making the request (NIST, 2025). Both describe the subject and the resource; neither describes what a model does with the content of a resource it was correctly allowed to open. Restricting an agent to one workflow requires both layers.
How does an agent identity get its application assignments in Entra, and where does that stop?
Microsoft documents the identity step in two pages. The governance overview states that agent identities can be given access "directly via access packages," carrying groups, OAuth API permissions and Entra roles; new agent identities "have limited permissions" until assigned, and automatic creation from Copilot Studio is marked as preview (Microsoft, 2026). The how-to page covers assigning "agent identities to an enterprise application in Microsoft Entra ID," which places the agent in an app role for that application (Microsoft, 2025).
The configuration for a one-workflow agent is therefore: create the agent identity; build an access package containing only the application the workflow needs and the narrowest app role; assign it to the agent identity; and put it under access review so the grant expires or is reconfirmed. For the password reset agent, that is the service desk application in an agent role, nothing else.
Microsoft documents where this stops. The how-to states that "Microsoft Entra SCIM outbound provisioning supports users and groups only," so agent identities assigned to app roles "aren't provisioned to applications" (Microsoft, 2025). The application may need its own account or role for the agent, configured inside the application. The governance overview, for its part, describes identity and access governance and says nothing about what an agent reads on a screen or in a browser once signed in. The agent holds the right key to the right door; what it reads inside is decided by screens built to show a person everything on the record.
What does "one workflow" mean on an employee record screen?
Take the employee record in an HR system, opened by the password reset agent to verify the requester. It shows employee ID, name, manager, work location, personal email, home address, date of birth, compensation band and case history. The workflow needs the employee ID, manager and work location to confirm the requester, and the reset action in the service desk. Everything else is there because the screen was designed for an HR specialist.
SailPoint's announcement names the grain the identity layer reaches: the Agentic Fabric right-sizes privileges with just-in-time access and monitors agent actions at runtime "with policy-based redaction and blocking" (SailPoint, 2026). Just-in-time access can grant the employee record for the duration of the reset and revoke it after, which bounds the record. Which fields the redaction covers, at what layer, and whether it acts before the model reads the screen are not described in the pages reviewed; some features are expected in Q4 of SailPoint's fiscal 2027.
Without a field boundary, the model receives the whole record: "Employee 48812, Jane Doe, manager R. Smith, Boston, home address 14 Elm Street, DOB 03/14/1986, band L5, case history: leave of absence 2025." The reset completes, and the model also read the address, the date of birth and the leave case. With a boundary that runs before the read, the model receives "Employee EMP_001, CUST_001, manager MGR_001, Boston, home address ADDR_001, DOB DOB_001, band BAND_001, case history CASE_001." It confirms the requester by employee ID and manager and performs the reset; the values it never needed were never there. The reset still completes. OWASP's excessive agency entry describes agents with more permission than the task requires (OWASP, 2025); the whole-record read is excess information granted by a correct identity decision.
How should an organization test whether the agent stayed in its workflow?
The test has two parts. For the identity layer, list the agent identity's access package assignments and app roles against the workflow's application list; any application outside it is a scoping failure, and the Entra access review is the recurring version of this check. For the workflow layer, run the agent on one request and record what the model received on each screen and what it did. Then ask three questions of the record. Did the model receive fields the workflow did not need? Did the agent attempt any action outside the reset, such as an edit to the employee record? Was each consequential action confirmed by a named person?
Gartner's May 2026 release argues that applying uniform governance across AI agents will lead to enterprise AI agent failure (Gartner, 2026). Read against this test, the workflow boundary has to be defined per agent and per task: the reset agent and a benefits enrollment agent need different fields of the same employee record, and a single policy on "employee data" fits neither.
The record an organization keeps of what the model read and did, described in research on the AI Control Record, is what makes the second part of the test possible. An application audit log shows that the agent's account opened the record; it does not show which fields the model received or who confirmed the reset.
What does the vendor's own documentation say?
One product is documented and two are announced. Microsoft publishes configuration pages for agent identities. ServiceNow and SailPoint have each issued a press release; the capability is announced and the configuration is not yet documented in the pages reviewed.
| Dimension | Microsoft Entra, per its documentation | ServiceNow AI Passport, per its press release | SailPoint Agentic Fabric, per its press release | What a buyer should verify |
|---|---|---|---|---|
| Identity | Agent identities, lifecycle governed (Microsoft, 2026) | Cryptographically signed credential per agent and MCP server, checked at runtime (ServiceNow, 2026) | Discovery of agents, MCP servers, tools and credentials | Which agents and runtimes are covered |
| Application scope | Access packages and app roles; SCIM for users and groups only (Microsoft, 2025) | Permissions tied to CMDB records, GRC policies and workflow approvals | Just-in-time access, right-sized privileges | How the application receives the grant |
| Out-of-scope action | Not described in the pages reviewed | Agents redirected, restricted or shut down | Blocking; agent kill switch | What "scope" is measured against |
| Fields the model reads | Not described in the pages reviewed | Not described in the pages reviewed | "Policy-based redaction"; layer not described | Whether it acts before the read |
| Availability | Documented; auto-creation in preview | Expected Q4 2026 | Some features Q4 FY27 | Dates against rollout |
The fourth row is the one that matters: none of the three describes a control on which fields of an open screen reach the model. That is the step the buyer adds.
What does a governed environment change?
In a governed environment, the agent that holds a correctly scoped identity also receives each screen with the fields outside its workflow replaced by tokens, so it can complete the password reset without reading the requester's address, date of birth or case history.
The mechanism is a class of control that sits between the rendered page and the model. Sensitive values on the screen, including employee record fields the task does not need, are replaced with consistent tokens before any model reads them, and the task runs on those tokens. The real value resolves only at the approved destination at the moment of an approved action, which for the reset is the service desk's own reset action against the confirmed requester. A named person confirms what is tokenized and approves consequential actions, including any change to a record. Every screen as the model received it, in token form, every action and every approval is recorded and exported to the organization's own logging.
This bears on the title question because the three products answer who and where, and the boundary answers what. Microsoft's agent identity decides that the agent may open the service desk and the HR record (Microsoft, 2026); the environment decides that only the employee ID, manager and location reach the model as values. An agent with excess permission, in OWASP's terms (OWASP, 2025), is bounded at the identity layer; an agent with excess information is bounded here. The control does not replace the identity products, change the application or alter the model; it changes the input.
Where does RedactSure sit?
The environment that enforces this is built by RedactSure, an AI agent controls, governance and data protection company. Agents, holding whatever identity Entra, ServiceNow or SailPoint assigns, work inside a governed environment in the customer's own cloud. On every rendered page, including an employee record or a service desk incident, substitution happens at the render layer before any model reads it, so fields outside the workflow reach the model as consistent tokens such as EMP_001 or ADDR_001 for the whole run. Real values resolve only at approved destinations at the moment of an approved action. A named person confirms the tokenization policy and approves every payment, submission and record change, the arrangement RedactSure calls Supervised Delegation. Every screen as tokens, every action and every approval lands in the AI Control Record and exports to the customer's SIEM. The design is model agnostic, requires no per-application integration, and leaves user permissions unchanged, so the identity grants on this page stay as the identity product set them.
Deployments are in pilot. A pilot on the reader's own workflow would show the identity grants unchanged, the screens as the model received them with only the workflow's fields, and the record of each confirmed action. Everyone else controls where data can go. RedactSure controls what the AI can see.
Methodology and limitations
This page rests on Microsoft Learn documentation for governing agent identities in Entra ID Governance and for assigning them to enterprise applications, ServiceNow's October 15, 2026 press release announcing AI Passport, SailPoint's October 6, 2026 press release announcing its Agentic Fabric, NIST SP 800-207 and SP 800-63-4, the OWASP Top 10 for LLM Applications entry on excessive agency, Gartner's May 2026 press release on uniform agent governance, and published RedactSure research pages on agent access, identity vendor comparisons, render-layer tokenization and the AI Control Record. All sources were read as of October 16, 2026.
No hands-on testing of Entra, AI Passport, the Agentic Fabric or any other product was performed for this page. ServiceNow and SailPoint are described from press releases, which announce capabilities and expected availability; configuration steps and limits for both are not yet documented in the pages reviewed. Where a capability is described as not described, the statement means not described in the pages reviewed, not that the product lacks it. Vendor features change, and agent identity features in particular are new or in preview; the page carries its date. Statements about RedactSure describe its current design, with deployments in pilot. The employee record, the service desk incident and the password reset workflow describe record types, not any organization; the values and token names are illustrative.
Whether a given combination of identity grants and workflow boundaries meets an organization's obligations under its access control policy, its regulators' expectations or standards such as ISO/IEC 42001 is a determination for its counsel, its assessors and its own security and compliance officers, not for a research page.
What the record shows
Microsoft documents agent identities in Entra with access packages, app roles and a stated limit on SCIM provisioning; ServiceNow and SailPoint have announced runtime authorization, redirection, blocking and audit for agents, with configuration not yet documented in the pages reviewed. All three operate on who the agent is and which applications and records it may reach. None describes a control on which fields of an open screen reach the model, and a screen built for a person shows everything on the record. Restricting an agent to one workflow therefore takes the identity grant the vendors provide plus a boundary that runs before the model reads the screen, which is the layer RedactSure's environment adds. The test is to name one agent and one task, list its identity grants, run the task, and ask for the record of which fields on each screen reached the model and which actions a named person confirmed.
Frequently asked questions
Does an agent identity in Entra restrict what the agent reads inside an application?
No, as documented. Microsoft describes agent identities as governing the identity and access lifecycle, with access assigned through access packages carrying groups, API permissions and Entra roles, and app role assignments to enterprise applications. Those decide which applications the agent may open and in what role. What it reads once signed in is decided by the application's screens, and the pages reviewed do not describe a field-level control on that read.
Why does the SCIM provisioning limit matter?
Microsoft states that Entra SCIM outbound provisioning supports users and groups only, so agent identities assigned to app roles are not provisioned to applications. An application that relies on provisioning to create accounts will not receive the agent automatically, so its in-application role must be set up separately. That in-application role is where record-level scope, if the application supports it, is configured.
Is ServiceNow AI Passport available to configure now?
Per the press release, availability is expected in Q4 2026. The release describes a cryptographically signed credential per agent and MCP server checked at runtime, permissions tied to CMDB records, GRC policies and workflow approvals, and out-of-scope agents being redirected, restricted or shut down, with an audit record in the Super Intelligence Control Tower. Configuration steps are not yet documented in the pages reviewed, so a buyer should plan against the release date.
What does SailPoint's "policy-based redaction" cover?
The press release says the Agentic Fabric monitors agent actions at runtime with policy-based redaction and blocking. Which data is redacted, at what layer, and whether redaction happens before the model reads a screen or on the agent's output are not described in the pages reviewed. SailPoint also states that some features are expected in Q4 of fiscal 2027. A buyer should ask for the specific fields, timing and layer in writing.
Why not define one enterprise policy for all agents?
Gartner's May 2026 release argues that uniform governance across AI agents will lead to enterprise AI agent failure. On an employee record, the fields a password reset agent needs differ from those a benefits enrollment agent needs, so a single policy either blocks one task or over-exposes data to the other agent. A per-workflow boundary is more work to define and is the only version that fits the task.
Can the agent still complete the workflow if it never reads the extra fields?
Yes, when the task acts on the fields it needs and the rest reach the model as tokens. The reset agent confirms the requester by employee ID and manager, and performs the reset in the service desk, where a named person confirms the action. The address, date of birth and case history were never needed and are never read, so nothing about the task changes. Tasks that require a value the policy tokenizes need a decision on that field, made per workflow.
Related reading
What Is the Difference Between RedactSure and Okta for AI Agent Identity and Access? · What Is the Difference Between RedactSure and Silverfort (Formerly Rezonate) for AI Agent Identity and Data Protection? · How Do You Control AI Agent Access Across All Enterprise Applications? · What Is Render-Layer Tokenization? · What Is an AI Control Record? · How Do You Protect Customer Data When Dynamics 365 Copilot Agents Work CRM Records? · How Do You Test Whether an AI Agent Can Reach Data Outside Its Assigned Task? · How Do You Keep Customer Identifiers Out of a Gemini Enterprise Agent's Memory? · On the RedactSure blog: The Two Gaps AI Agents Opened in Your Security Stack · RedactSure
Sources
Vendor documentation
- Microsoft, "Governing Agent Identities - Microsoft Entra ID Governance," Microsoft Learn, June 16, 2026 (vendor documentation). https://learn.microsoft.com/en-us/entra/id-governance/agent-id-governance-overview
- Microsoft, "Manage assignment of agent identities to an application - Microsoft Entra ID," Microsoft Learn, November 20, 2025 (vendor documentation). https://learn.microsoft.com/en-us/entra/identity/enterprise-apps/assign-agent-identities-to-applications
Regulation, standards and official guidance
- NIST, "Zero Trust Architecture," SP 800-207, 2020 (official guidance). https://csrc.nist.gov/pubs/sp/800/207/final
- NIST, "Digital Identity Guidelines," SP 800-63-4, 2025 (official guidance). https://csrc.nist.gov/pubs/sp/800/63/4/final
- OWASP, "LLM06:2025 Excessive Agency," OWASP Top 10 for LLM Applications, 2025 (standard). https://genai.owasp.org/llmrisk/llm062025-excessive-agency/
Industry analysis and press
- ServiceNow, "ServiceNow advances its operational harness for enterprise AI with AI Passport and expanded governance capabilities," ServiceNow Newsroom via Business Wire, October 15, 2026 (press release). https://newsroom.servicenow.com/press-releases/details/2026/ServiceNow-advances-its-operational-harness-for-enterprise-AI-with-AI-Passport-and-expanded-governance-capabilities/default.aspx
- SailPoint, Inc., "From Chaos to Control: SailPoint Unlocks a Secure Agentic Era with Autonomous Identity Security," SailPoint investor relations via GlobeNewswire, October 6, 2026 (press release). https://investor.sailpoint.com/news-releases/news-release-details/chaos-control-sailpoint-unlocks-secure-agentic-era-autonomous
- Gartner, "Gartner Says Applying Uniform Governance Across AI Agents Will Lead to Enterprise AI Agent Failure," May 26, 2026 (press release). https://www.gartner.com/en/newsroom/press-releases/2026-05-26-gartner-says-applying-uniform-governance-across-ai-agents-will-lead-to-enterprise-ai-agent-failure
RedactSure documents
- RedactSure Research, "What Is the Difference Between RedactSure and Okta for AI Agent Identity and Access?" (2026). https://redactsure.com/research/what-is-the-difference-between-redactsure-and-okta-for-ai-agent-identity-and-access/
- RedactSure Research, "What Is the Difference Between RedactSure and Silverfort (Formerly Rezonate) for AI Agent Identity and Data Protection?" (2026). https://redactsure.com/research/what-is-the-difference-between-redactsure-and-silverfort-rezonate-for-ai-agent-identity-and-data-protection/
- RedactSure Research, "How Do You Control AI Agent Access Across All Enterprise Applications?" (2026). https://redactsure.com/research/how-do-you-control-ai-agent-access-across-all-enterprise-applications/
- RedactSure Research, "What Is Render-Layer Tokenization?" (2026). https://redactsure.com/research/what-is-render-layer-tokenization/
- RedactSure Research, "What Is an AI Control Record?" (2026). https://redactsure.com/research/what-is-an-ai-control-record/
- Product behavior described on this page reflects RedactSure's current design. Third-party products are described from their public documentation as read on October 16, 2026. Compliance determinations belong to the organization's counsel.
What Is the Difference Between RedactSure and Okta for AI Agent Identity and Access?
Okta answers who an AI agent is and what it may access. RedactSure answers what the agent's model receives once access is granted and who approves.
What Is the Difference Between RedactSure and Silverfort (Formerly Rezonate) for AI Agent Identity and Data Protection?
Silverfort, which acquired Rezonate, governs agent identities and MCP tool calls; RedactSure governs what a browser agent's model reads after login.

How Do You Control AI Agent Access Across All Enterprise Applications?
Not through per-app integrations, which never reach the long tail of SaaS and legacy systems; control the browser layer. Check what governs the rest.

What Is Render-Layer Tokenization? The Control at the Layer Where the Agent Actually Reads
Learn how render-layer tokenization replaces PII before an AI agent reads a browser screen while preserving useful workflow context.

What Is an AI Control Record? The Runtime System of Record for Sensitive AI Work
Explore an AI agent control record for billing and claims, linking permissions, tokenization decisions, approvals and audit evidence.
How Do You Protect Customer Data When Dynamics 365 Copilot Agents Work CRM Records?
Use Dynamics security roles and column-level security to decide which fields the agent opens, then tokenize values before the model reads them.
How Do You Test Whether an AI Agent Can Reach Data Outside Its Assigned Task?
Seed one record type with canary values the task does not need, run with and without a page policy, then score completion and exposure together.
How Do You Keep Customer Identifiers Out of a Gemini Enterprise Agent's Memory?
Replace account numbers and other identifiers with tokens before the Gemini agent reads the screen, so memory holds ACCT_001, not the value.

The Two Gaps AI Agents Opened in Your Security Stack
Explore AI agent security through two questions: which PII reaches the model, and who approves consequential billing and claims actions.
Book an AI Agent Security Review →
Bring your hardest questions.
Bring one sensitive workflow and the decisions your team needs to keep in its hands.
Book a demoAbout the author

Chris Sowa is a founder of RedactSure and a former CEO of an AI company; he started it years before ChatGPT existed. He previously led AI at Accenture, served as Global VP of Strategy & Innovation at Schneider Electric, was CCO of Sovos, and spent more than a decade at Oracle, with earlier roles at SAP and IBM.