Do OpenAI Dots Rules Control What the Agent Sees?
Review OpenAI Dots Custom Rules, AI agent security and tokenization before connecting billing, claims or other workflows that expose PII.
 redactsure
Research topic
Research on Least Exposure for AI agent workflows, with tokenization, access controls and evidence for teams handling sensitive business data.
Review OpenAI Dots Custom Rules, AI agent security and tokenization before connecting billing, claims or other workflows that expose PII.
Review OpenAI Dots for healthcare billing, PHI exposure, HIPAA terms and AI agent controls before connecting patient records in Epic.
Assess OpenAI Dots for student records, FERPA obligations and AI agent access before connecting PowerSchool or other district systems.
Assess OpenAI Dots for payments, PCI scope and vendor bank data, with AI agent input controls for accounts payable and cardholder workflows.
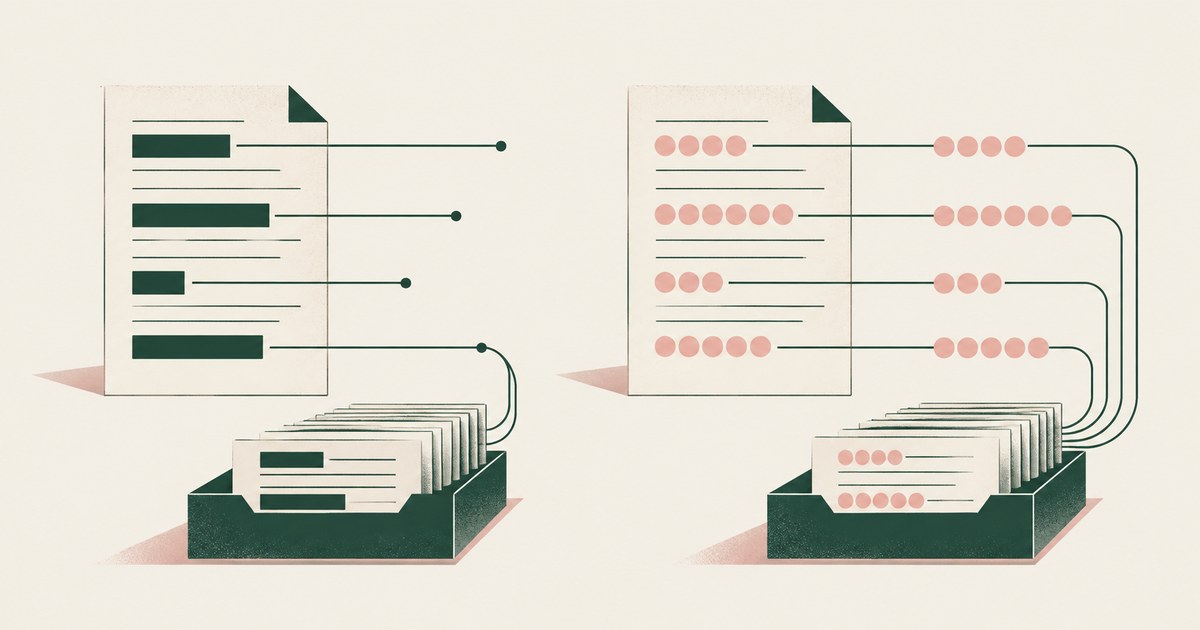
Compare data masking and tokenization for AI agent workflows that match claims, patient accounts and student records across application screens.
Compare payment tokenization with AI agent input controls for billing and accounts payable, including customer PII and vendor bank details.
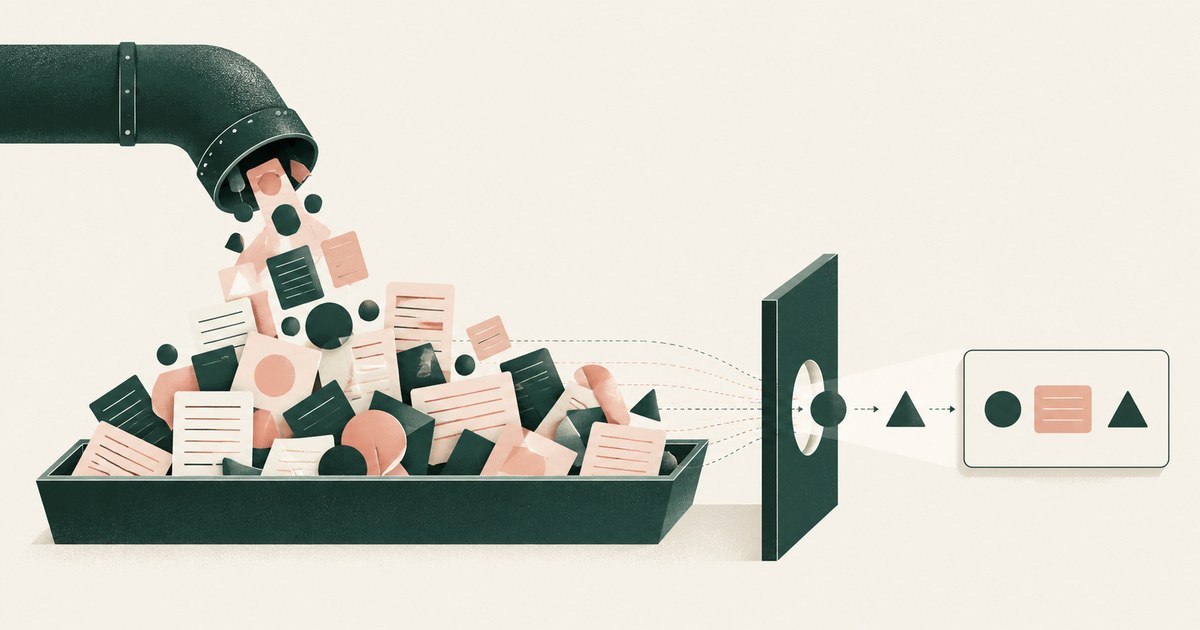
Assess AI agent connector responses for excess PII in billing, claims and student records, with field selection, filtering and tokenization.
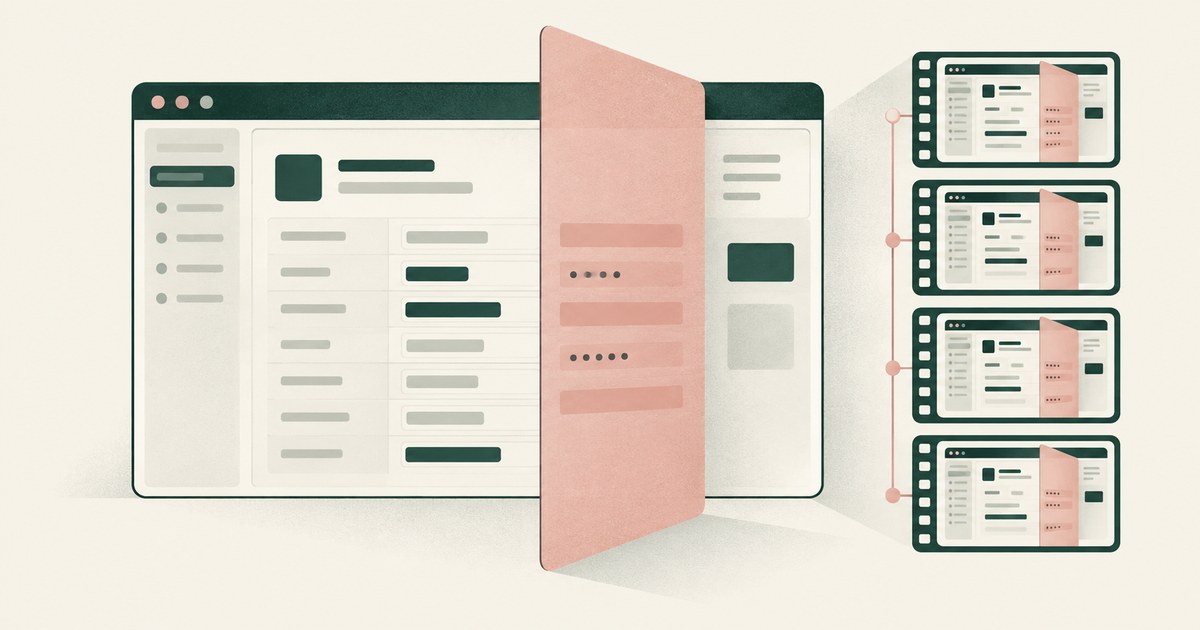
Review Copilot Studio AI agent screenshots, PII exposure and tokenization for claims and patient accounts, including replay retention settings.
Assess Model Armor input coverage, AI agent security and tokenization for billing and claims, including screenshots and connector responses.
Review AgentCore AI agent input controls, PII exposure and tokenization for claims and payments, including browser observations and recordings.
Compare screen automation, APIs and MCP for AI agent billing and claims workflows, with PII input controls, tokenization and human approvals.
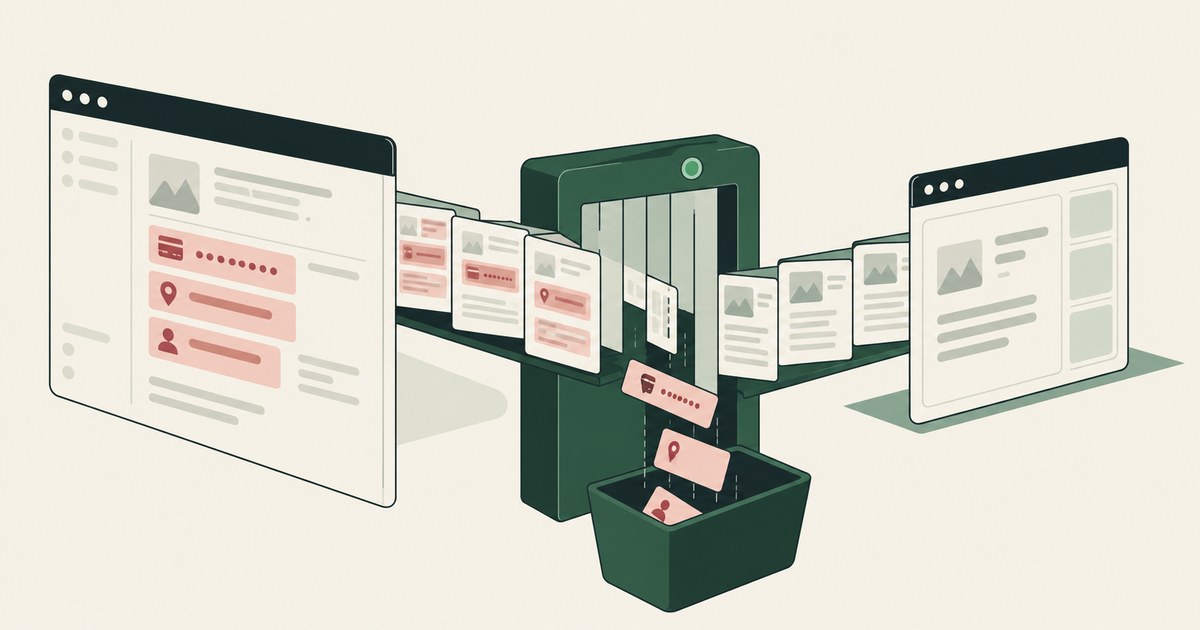
Review Protect Data From Screen-Reading AI Agents, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
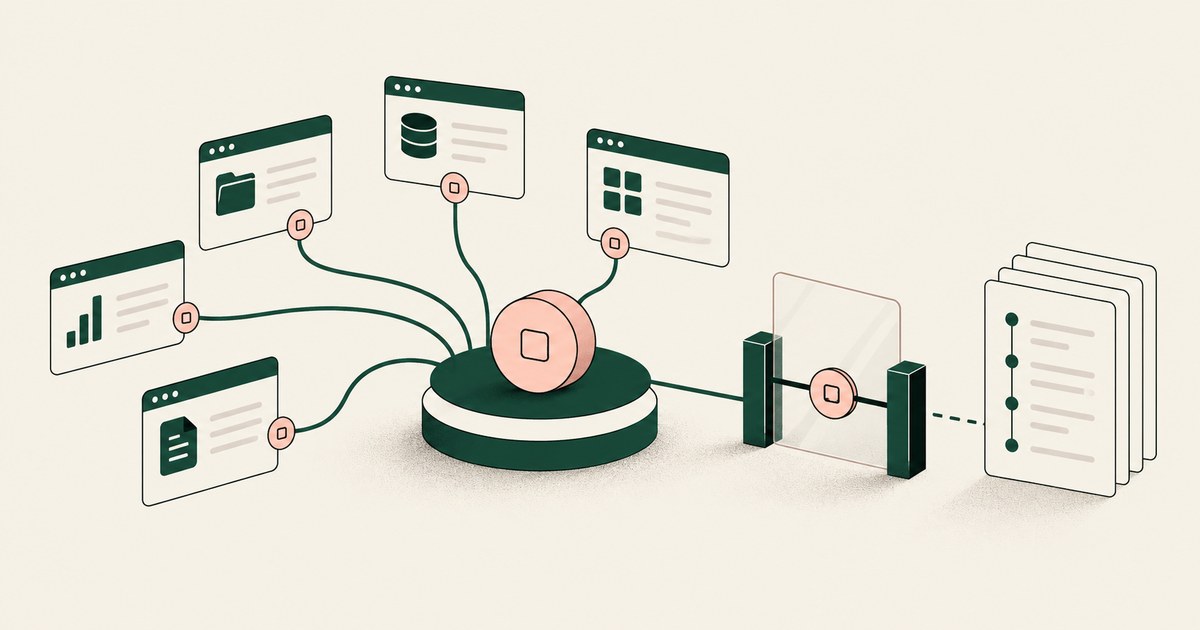
Review Secure AI Agents That Navigate Across Applications, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
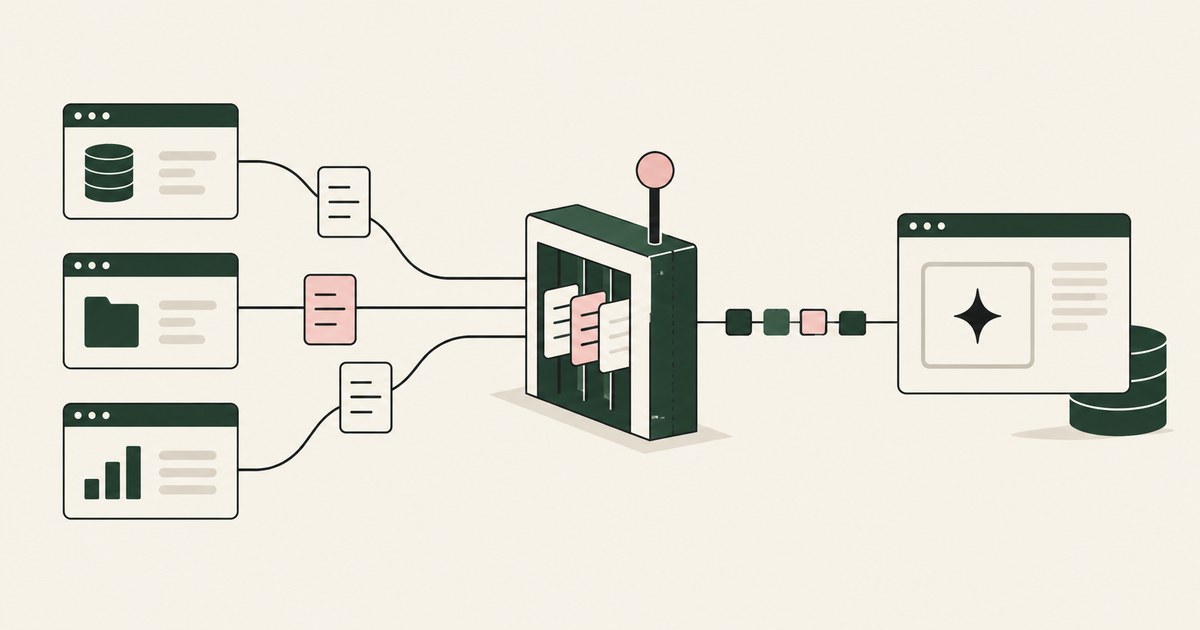
Review Limit Sensitive Data Access for AI Agents, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
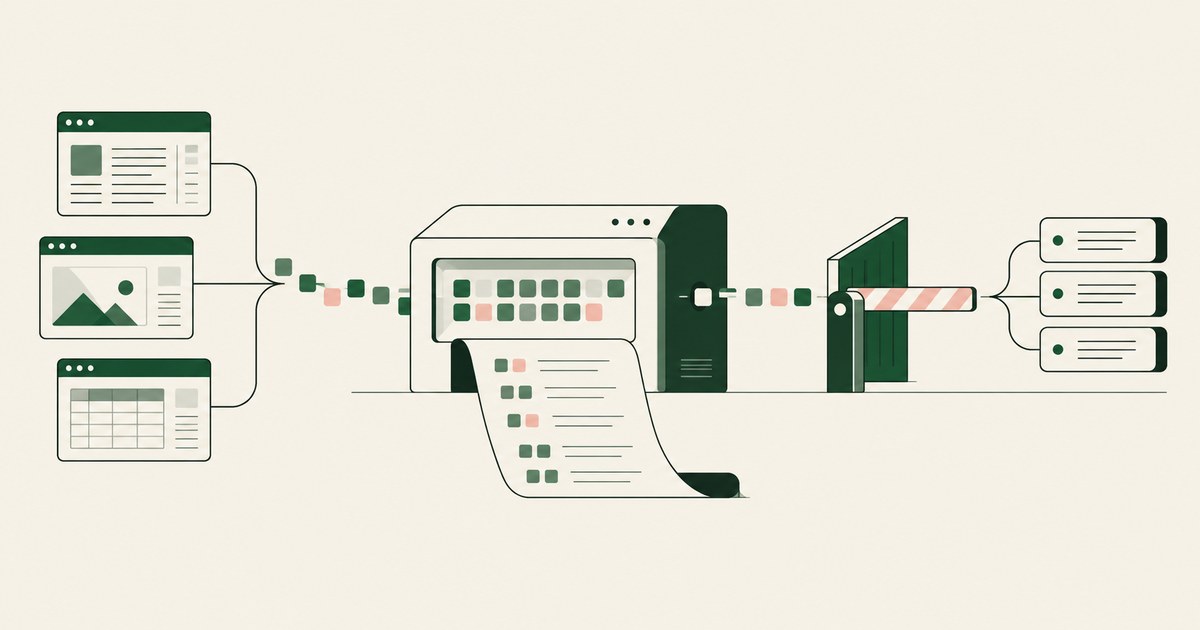
Review Monitor What an AI Agent Actually Accesses, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
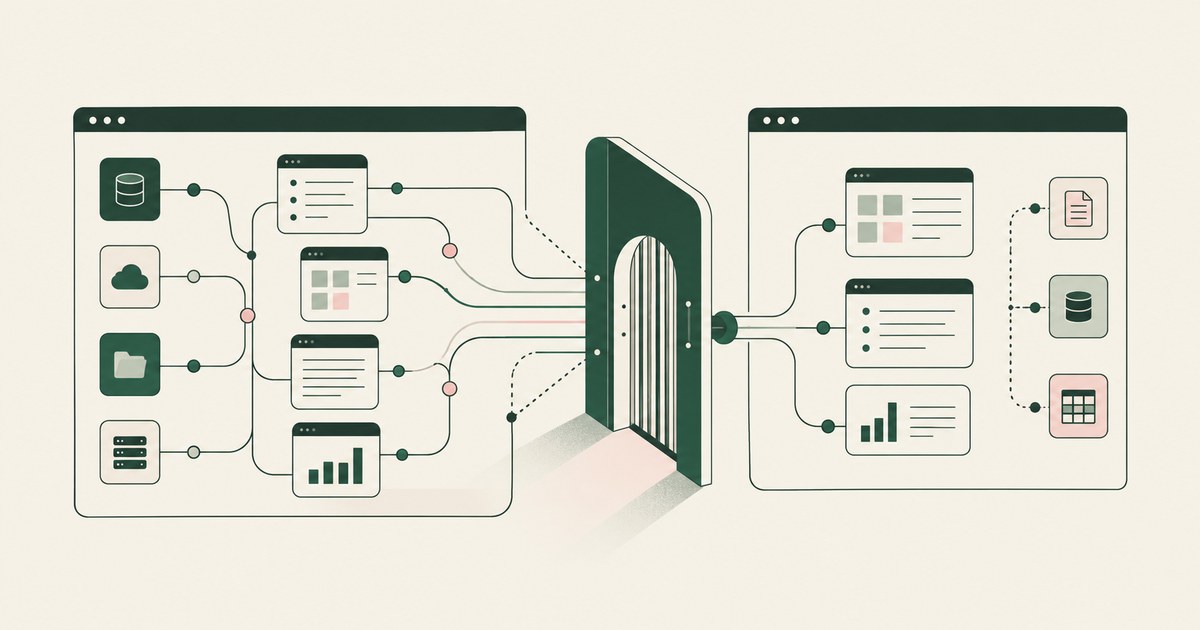
Review Map All the Data an AI Agent Can Reach, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
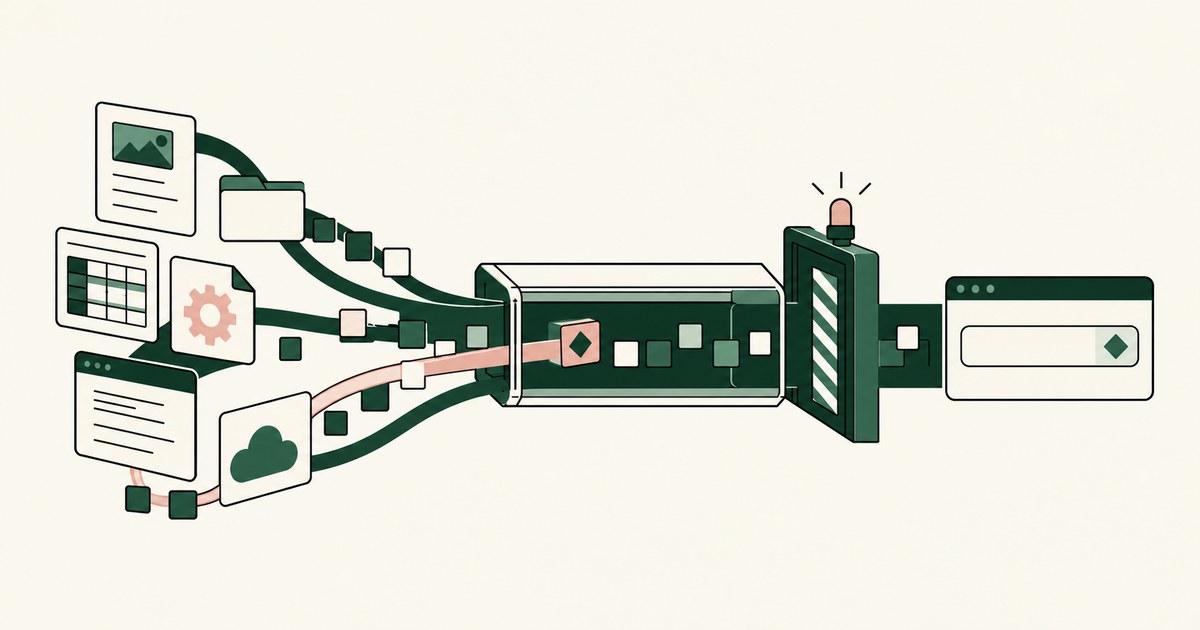
Review Do 80% of Prompt Injections Start Outside the Prompt, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
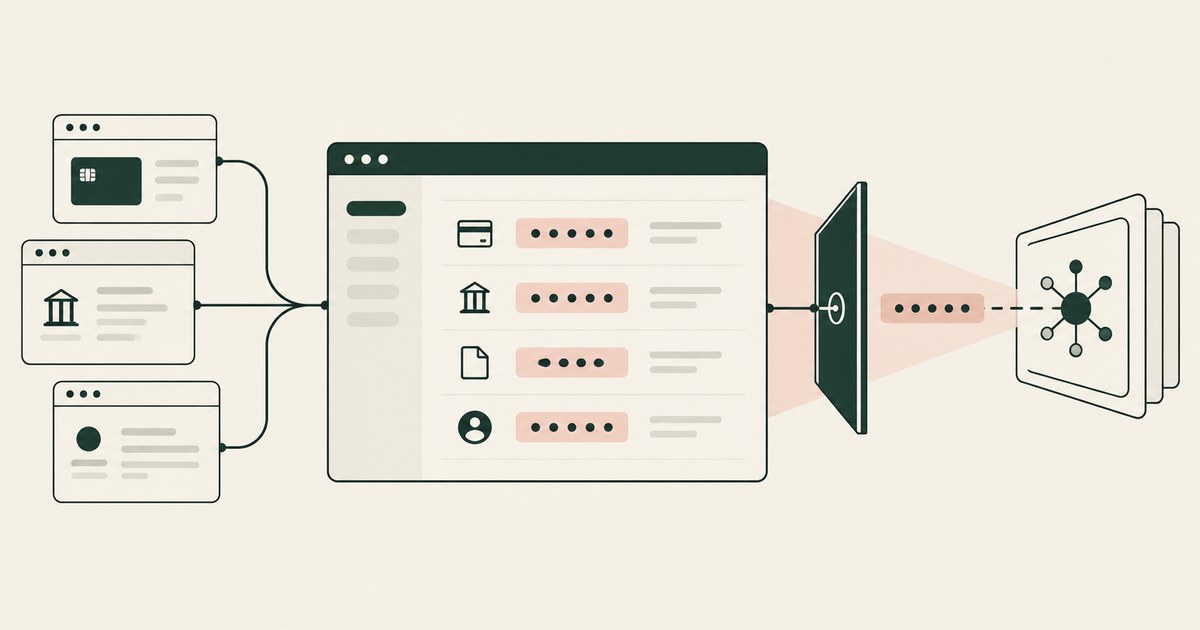
Review Screen-Level Tokenization, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
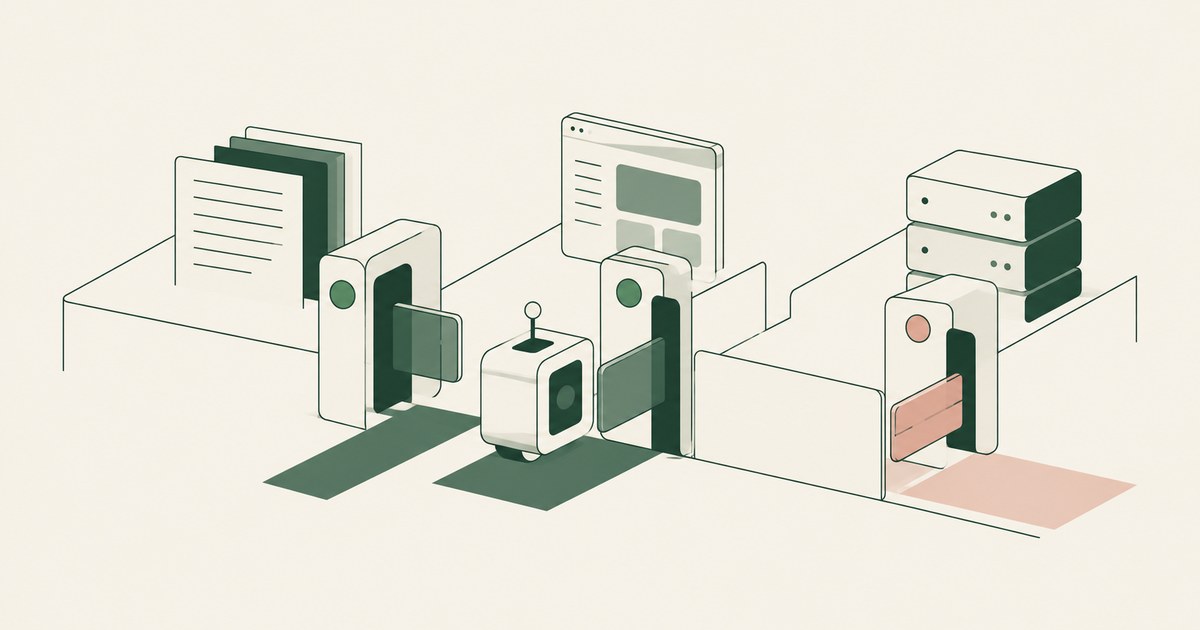
Review AI Agent Least Privilege, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
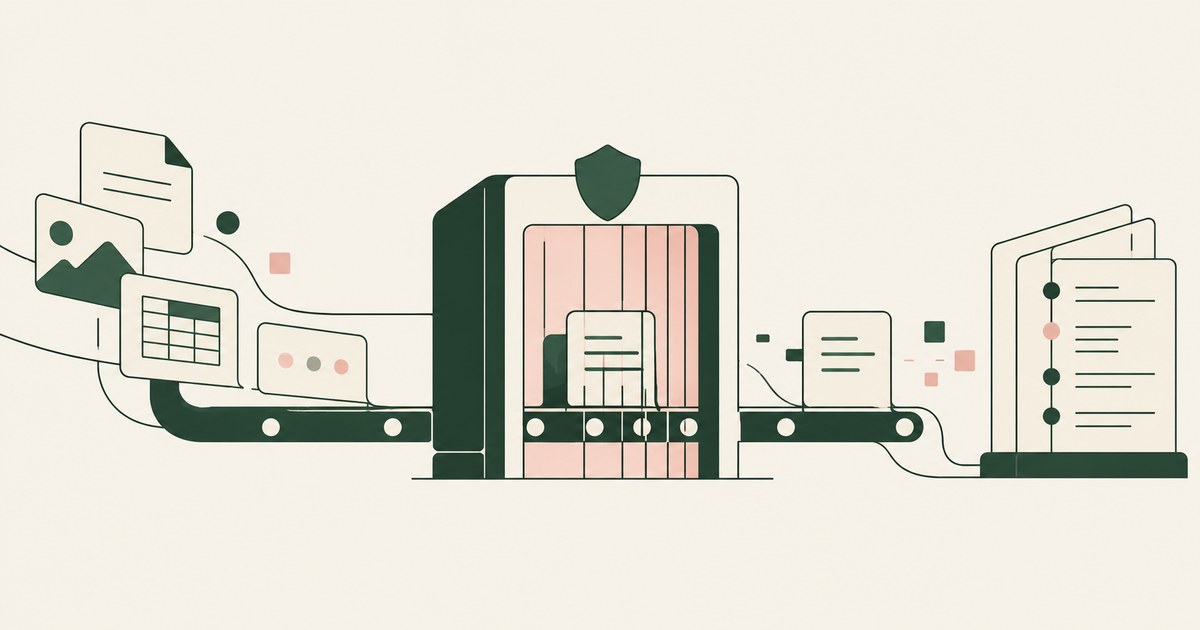
Review AI Agent Data Security, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review AI Agent Data Minimization, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review AI Agent Data Exposure, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review What Browser Alternatives Preserve Normal Workflows, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review secure AI agents for AI agent security, with practical checks on sensitive data, tokenization and named human approvals.
Review run an AI amnesty for AI agent security, with practical checks on sensitive data, tokenization and named human approvals.
Review Protect Sensitive Data Without App Lockdowns, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review Enforce Data Security Without Disrupting Work, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review Shadow AI for AI agent security, with practical checks on sensitive data, tokenization and named human approvals.
Review AI Agent Visibility, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review AI Agent Discovery for AI agent security, with practical checks on sensitive data, tokenization and named human approvals.
Review AI Agent Access Control, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review an Overprivileged AI Agent, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
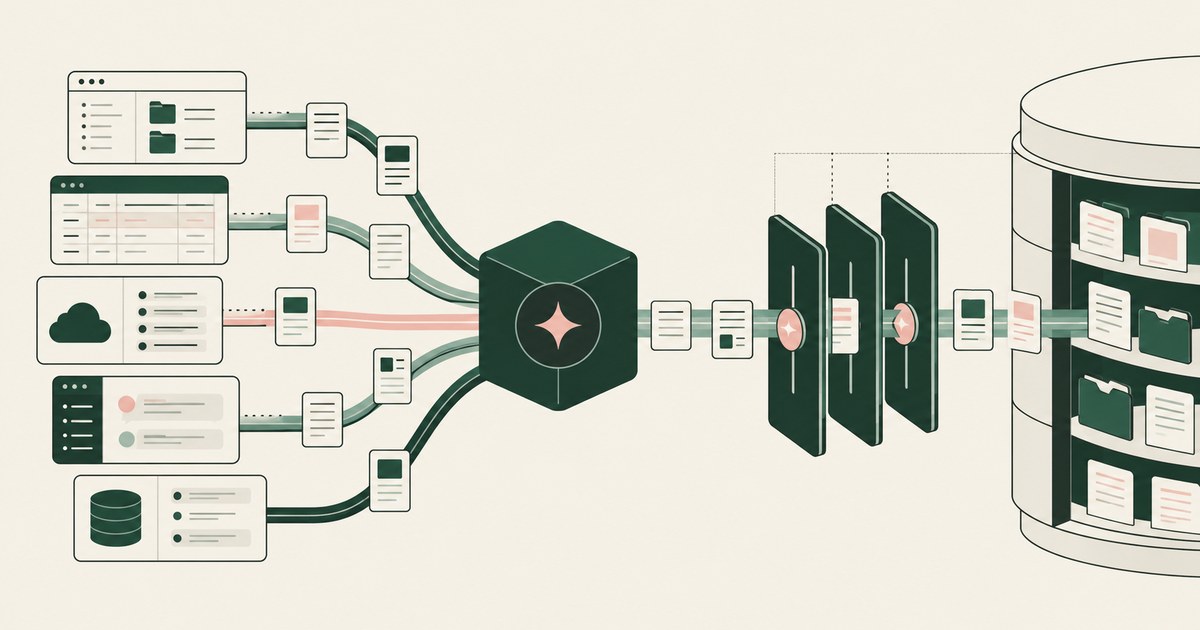
Review AI Agent Data Access, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review AI Agent Oversharing, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
Review AI Agent Data Reach, with AI agent security, tokenization and approval checks for sensitive enterprise workflows.
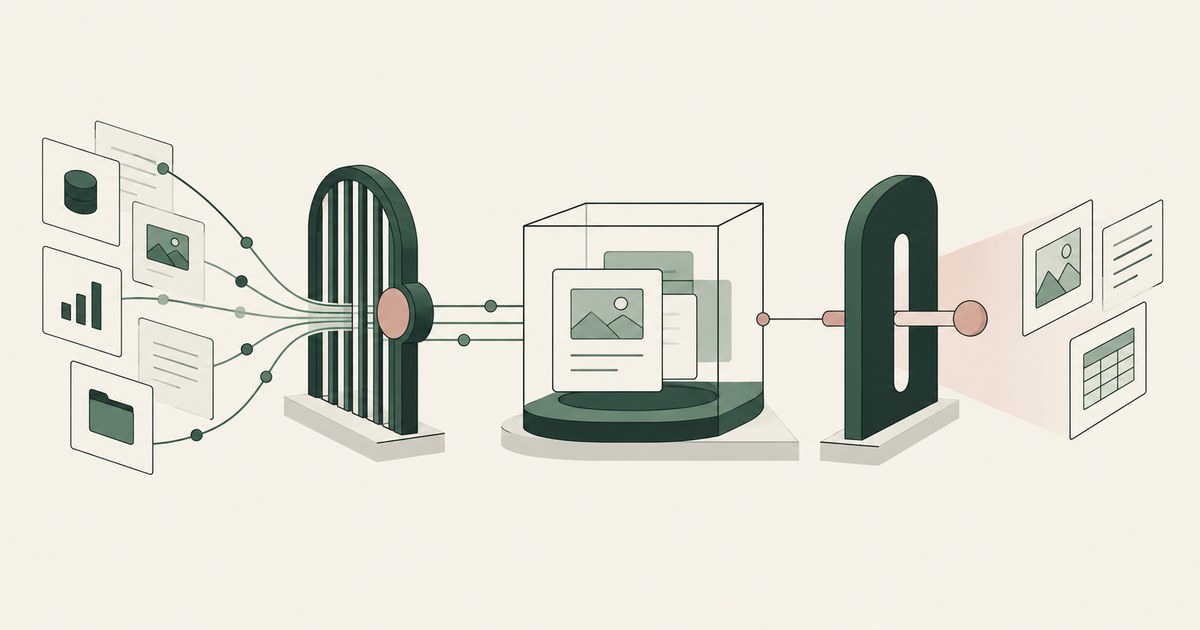
Microsoft Agent 365 governs agent reach via its registry, Entra and Purview; RedactSure replaces values on the rendered screen before any model reads it.
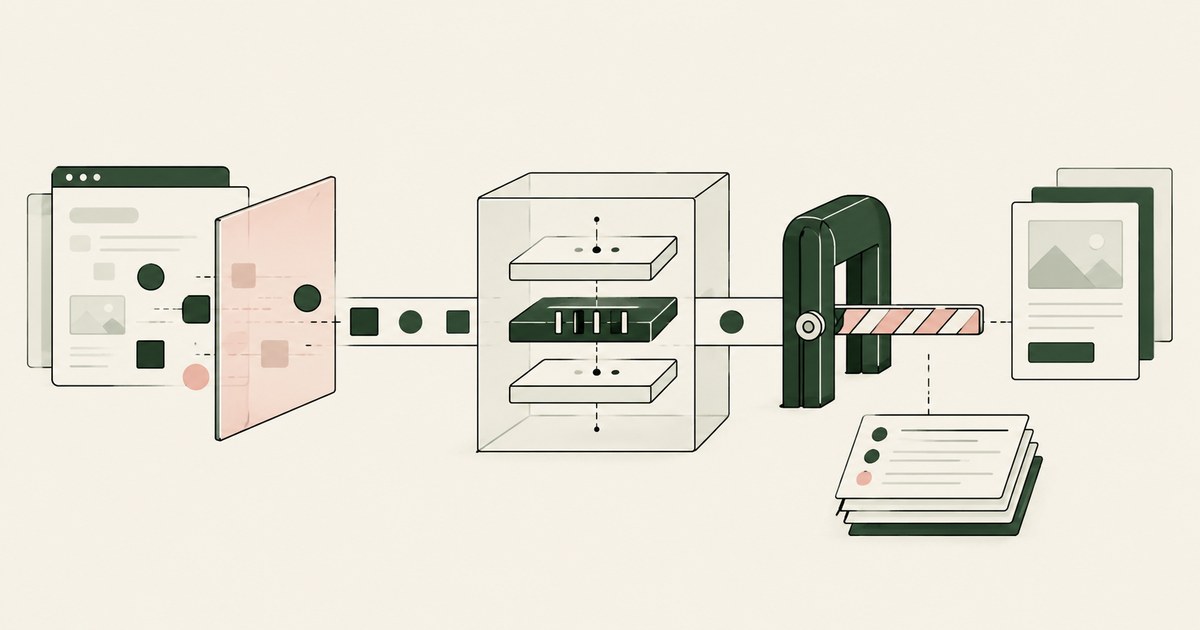
Arthur AI checks prompts and responses at the application LLM boundary around the model call. RedactSure tokens values before any model reads the screen.
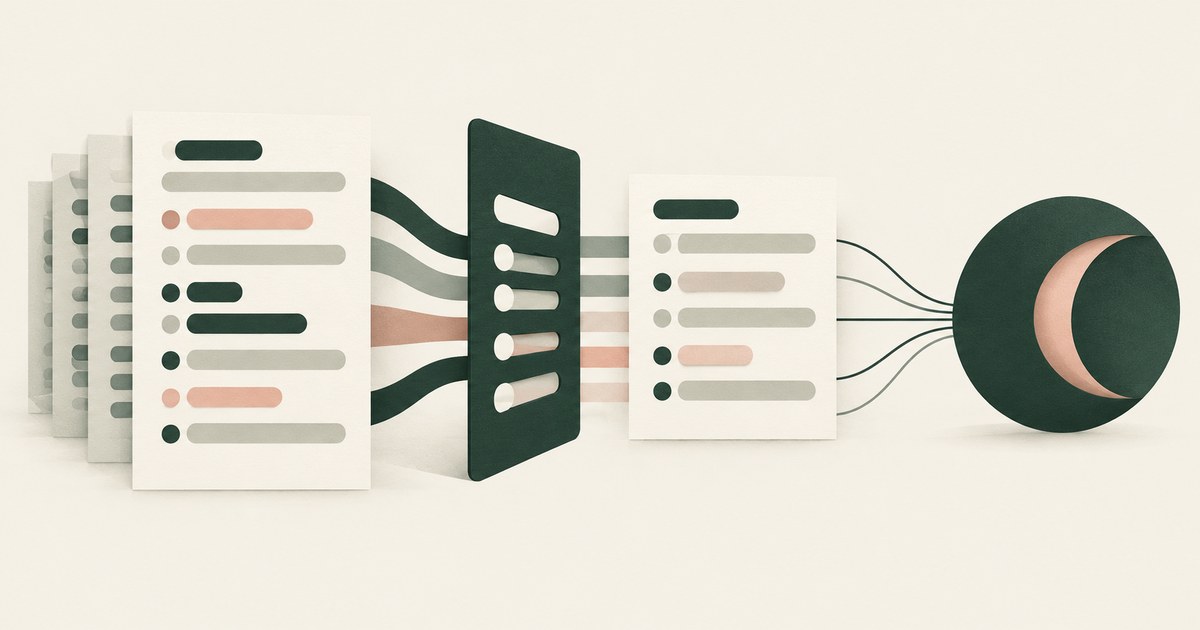
Apply data minimization at the moment the model reads: open the record it needs, but tokenize identifiers before it sees the screen. Check what it read.
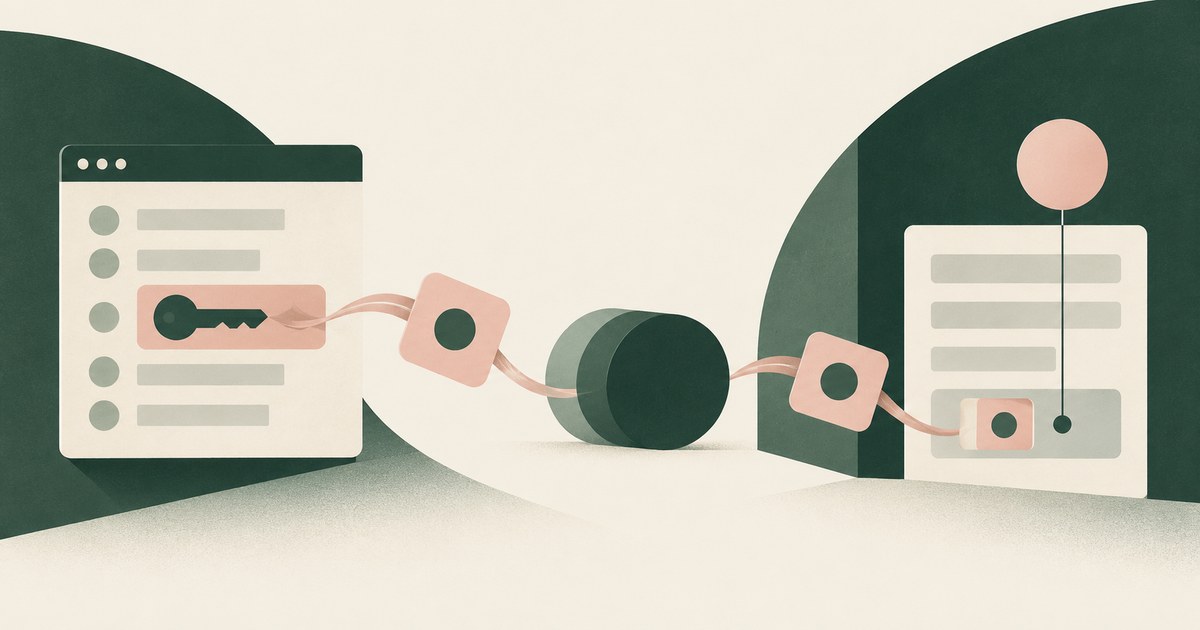
Less, and still some: an agent with no credentials can still push, delete or post under whatever grant it carries. Who approves those actions?